
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
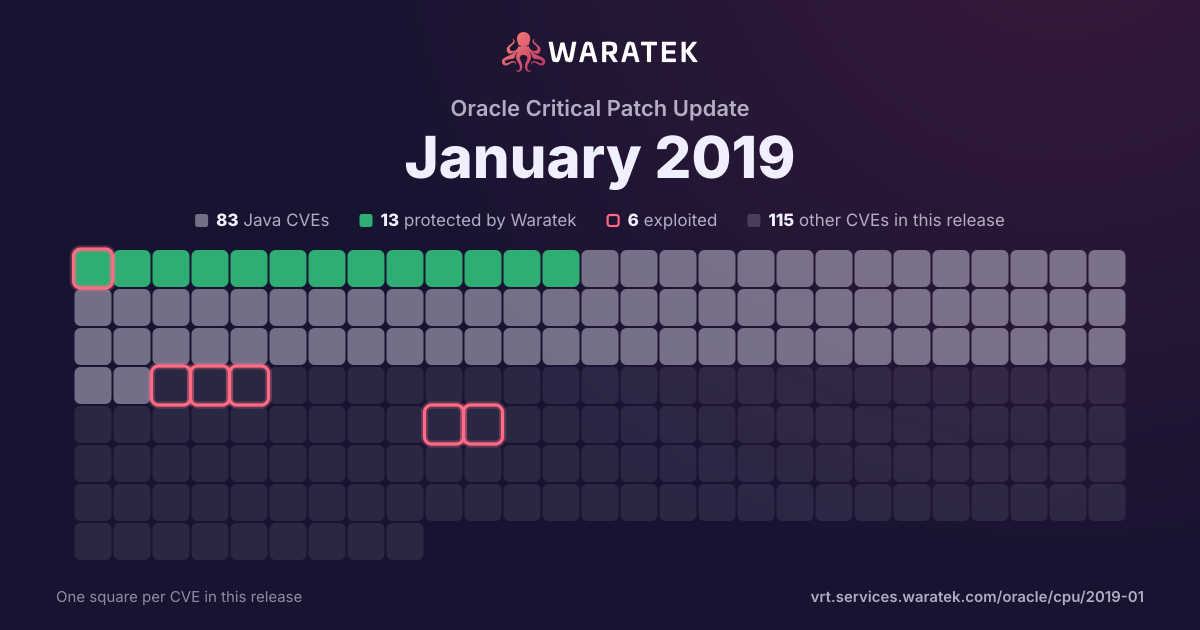
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 1 in Waratek scope · 1 protected · 3 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
7matches
1in Waratek scope14.3%
1protected14.3%
3exploited42.9%
0CISA KEV0.0%
2public PoC28.6%
2EPSS ≥ 0.528.6%
Protected by Waratek
1
14.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
42.9%
Not applicable
3
42.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
14.3%
partly blocked
0
0.0%
not blocked
6
85.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
42.9%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
57.1%
split by
peak 2 / quarter
Q1 171
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 170
Q3 171
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 181
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Q2 182
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
Exploited1
No public exploit1
Q3 182
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
Exploited1
No public exploit1
Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18Q3 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-11763 | Medium | 2018-09-25 | Outside Waratek scope | Exploited | In Apache HTTP Server 2.4.17 to 2.4.34, by sending continuous, large SETTINGS frames a client can occupy a connection, server thread and CPU time without any connection timeout coming to effect. This affects only HTTP/2 connections. A possible mitigation is to not enable the h2 protocol. |
| CVE-2018-3646 | Medium | 2018-08-14 | Not applicable | No public exploit | Systems with microprocessors utilizing speculative execution and address translations may allow unauthorized disclosure of information residing in the L1 data cache to an attacker with local user access with guest OS privilege via a terminal page fault and a side-channel analysis. |
| CVE-2018-3639 | Medium | 2018-05-22 | Outside Waratek scope | Exploited | Systems with microprocessors utilizing speculative execution and speculative execution of memory reads before the addresses of all prior memory writes are known may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis, aka Speculative Store Bypass (SSB), Variant 4. |
| CVE-2018-11212 | Medium | 2018-05-16 | Not applicable | No public exploit | An issue was discovered in libjpeg 9a and 9d. The alloc_sarray function in jmemmgr.c allows remote attackers to cause a denial of service (divide-by-zero error) via a crafted file. |
| CVE-2015-9251 | Medium | 2018-01-18 | Outside Waratek scope | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2016-9392 | Medium | 2017-03-23 | Not applicable | No public exploit | The calcstepsizes function in jpc_dec.c in JasPer before 1.900.17 allows remote attackers to cause a denial of service (assertion failure) via a crafted file. |