
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
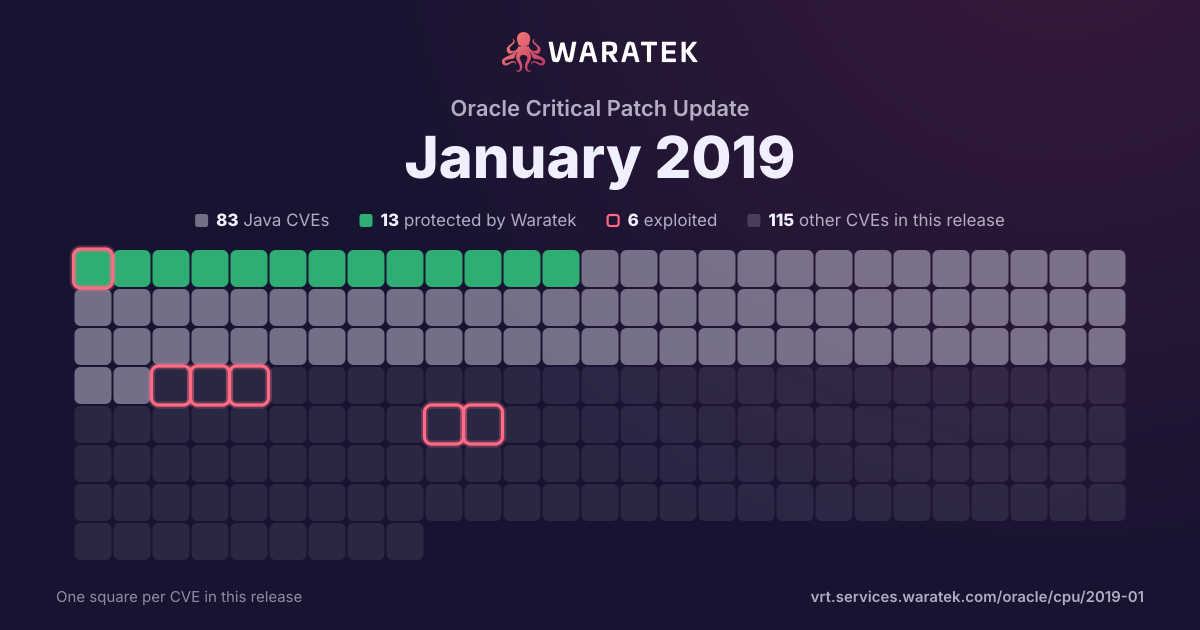
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 7 in Waratek scope · 6 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 2 EPSS ≥ 0.5
10matches
7in Waratek scope70.0%
6protected60.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC10.0%
2EPSS ≥ 0.520.0%
Protected by Waratek
6
60.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
10.0%
Outside Waratek scope
2
20.0%
Not applicable
1
10.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
6
60.0%
partly blocked
0
0.0%
not blocked
4
40.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
10.0%
Proof of concept only
0
0.0%
Forecast only
1
10.0%
No public exploit
8
80.0%
split by
peak 3 / quarter
Q4 162
Protected by Waratek1
Outside Waratek scope1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 170
Q2 172
Protected by Waratek1
No exploit published1
Critical2
blocked by ARMR today1
not blocked1
Working exploit published1
No public exploit1
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 170
Q1 182
Protected by Waratek1
Outside Waratek scope1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q2 183
Protected by Waratek2
Not applicable1
Critical3
blocked by ARMR today2
not blocked1
Forecast only1
No public exploit2
Q4 16Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-8013 | Critical | 2018-05-24 | Protected by Waratek | No public exploit | In Apache Batik 1.x before 1.10, when deserializing subclass of `AbstractDocument`, the class takes a string from the inputStream as the class name which then use it to call the no-arg constructor of the class. Fix was to check the class type before calling newInstance in deserialization. |
| CVE-2018-1000300 | Critical | 2018-05-24 | Not applicable | No public exploit | curl version curl 7.54.1 to and including curl 7.59.0 contains a CWE-122: Heap-based Buffer Overflow vulnerability in denial of service and more that can result in curl might overflow a heap based memory buffer when closing down an FTP connection with very long server command replies.. This vulnerability appears to have been fixed in curl < 7.54.1 and curl >= 7.60.0. |
| CVE-2018-1275 | Critical | 2018-04-11 | Protected by Waratek | Forecast only | Spring Framework, versions 5.0 prior to 5.0.5 and versions 4.3 prior to 4.3.16 and older unsupported versions, allow applications to expose STOMP over WebSocket endpoints with a simple, in-memory STOMP broker through the spring-messaging module. A malicious user (or attacker) can craft a message to the broker that can lead to a remote code execution attack. This CVE addresses the partial fix for CVE-2018-1270 in the 4.3.x branch of the Spring Framework. |
| CVE-2017-15095 | Critical | 2018-02-06 | Protected by Waratek | No public exploit | A deserialization flaw was discovered in the jackson-databind in versions before 2.8.10 and 2.9.1, which could allow an unauthenticated user to perform code execution by sending the maliciously crafted input to the readValue method of the ObjectMapper. This issue extends the previous flaw CVE-2017-7525 by blacklisting more classes that could be used maliciously. |
| CVE-2016-6814 | Critical | 2018-01-18 | Outside Waratek scope | No public exploit | When an application with unsupported Codehaus versions of Groovy from 1.7.0 to 2.4.3, Apache Groovy 2.4.4 to 2.4.7 on classpath uses standard Java serialization mechanisms, e.g. to communicate between servers or to store local data, it was possible for an attacker to bake a special serialized object that will execute code directly when deserialized. All applications which rely on serialization and do not isolate the code which deserializes objects were subject to this vulnerability. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2015-8965 | Critical | 2017-04-06 | No exploit published | No public exploit | Rogue Wave JViews before 8.8 patch 21 and 8.9 before patch 1 allows remote attackers to execute arbitrary Java code that exists in the classpath, such as test code or administration code. The issue exists because the ilog.views.faces.IlvFacesController servlet in jviews-framework-all.jar does not require explicit configuration of servlets that can be called. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2015-1832 | Critical | 2016-10-03 | Outside Waratek scope | No public exploit | XML external entity (XXE) vulnerability in the SqlXmlUtil code in Apache Derby before 10.12.1.1, when a Java Security Manager is not in place, allows context-dependent attackers to read arbitrary files or cause a denial of service (resource consumption) via vectors involving XmlVTI and the XML datatype. |