
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
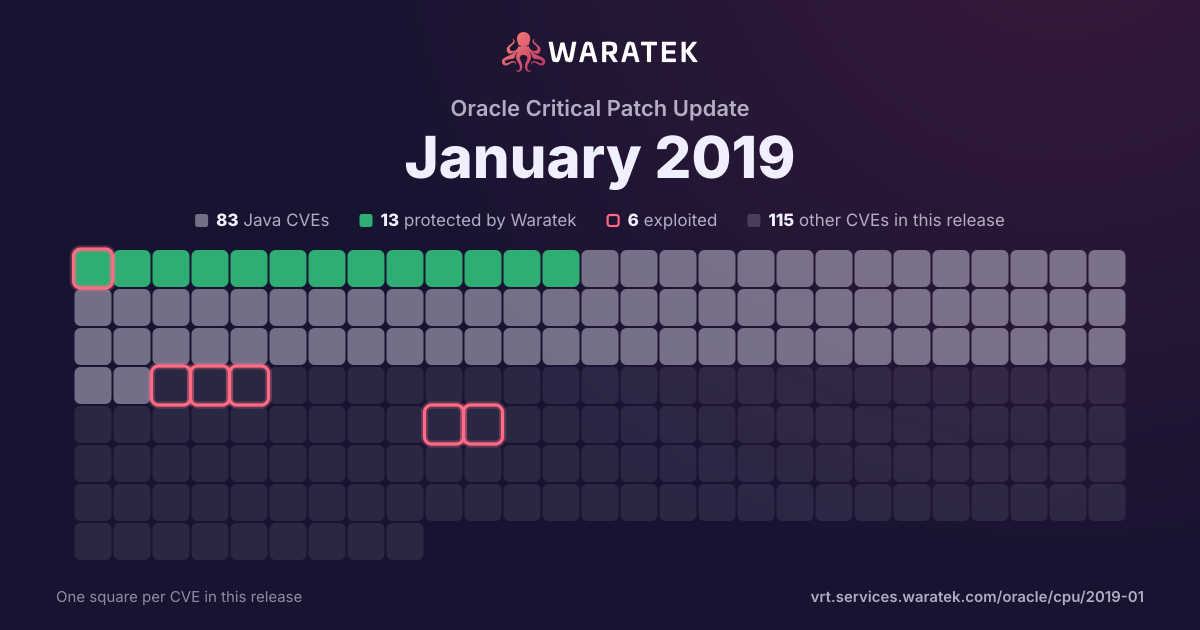
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 3 in Waratek scope · 2 protected · 2 exploited · 1 CISA KEV · 1 public PoC · 3 EPSS ≥ 0.5
7matches
3in Waratek scope42.9%
2protected28.6%
2exploited28.6%
1CISA KEV14.3%
1public PoC14.3%
3EPSS ≥ 0.542.9%
Protected by Waratek
2
28.6%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
14.3%
Outside Waratek scope
1
14.3%
Not applicable
3
42.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
28.6%
partly blocked
0
0.0%
not blocked
5
71.4%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
28.6%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
14.3%
No public exploit
4
57.1%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-11763 | Medium | 2018-09-25 | Outside Waratek scope | Exploited | In Apache HTTP Server 2.4.17 to 2.4.34, by sending continuous, large SETTINGS frames a client can occupy a connection, server thread and CPU time without any connection timeout coming to effect. This affects only HTTP/2 connections. A possible mitigation is to not enable the h2 protocol. |
| CVE-2018-11775 | High | 2018-09-10 | No exploit published | No public exploit | TLS hostname verification when using the Apache ActiveMQ Client before 5.15.6 was missing which could make the client vulnerable to a MITM attack between a Java application using the ActiveMQ client and the ActiveMQ server. This is now enabled by default. |
| CVE-2018-11776 | High | 2018-08-22 | Protected by Waratek | Exploited | Apache Struts versions 2.3 to 2.3.34 and 2.5 to 2.5.16 suffer from possible Remote Code Execution when alwaysSelectFullNamespace is true (either by user or a plugin like Convention Plugin) and then: results are used with no namespace and in same time, its upper package have no or wildcard namespace and similar to results, same possibility when using url tag which doesn't have value and action set and in same time, its upper package have no or wildcard namespace. |
| CVE-2018-1000632 | High | 2018-08-20 | Protected by Waratek | No public exploit | dom4j version prior to version 2.1.1 contains a CWE-91: XML Injection vulnerability in Class: Element. Methods: addElement, addAttribute that can result in an attacker tampering with XML documents through XML injection. This attack appear to be exploitable via an attacker specifying attributes or elements in the XML document. This vulnerability appears to have been fixed in 2.1.1 or later. |
| CVE-2018-3646 | Medium | 2018-08-14 | Not applicable | No public exploit | Systems with microprocessors utilizing speculative execution and address translations may allow unauthorized disclosure of information residing in the L1 data cache to an attacker with local user access with guest OS privilege via a terminal page fault and a side-channel analysis. |
| CVE-2018-5390 | High | 2018-08-06 | Not applicable | Forecast only | Linux kernel versions 4.9+ can be forced to make very expensive calls to tcp_collapse_ofo_queue() and tcp_prune_ofo_queue() for every incoming packet which can lead to a denial of service. |
| CVE-2016-9583 | High | 2018-08-01 | Not applicable | No public exploit | An out-of-bounds heap read vulnerability was found in the jpc_pi_nextpcrl() function of jasper before 2.0.6 when processing crafted input. |