
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
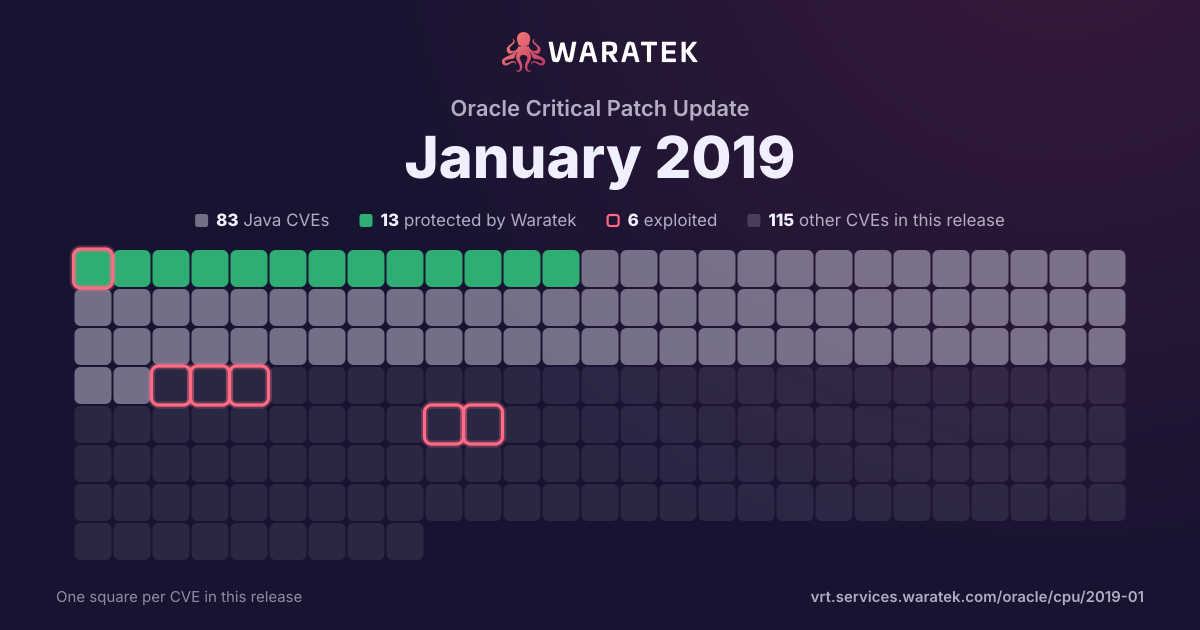
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 2 in Waratek scope · 2 protected · 1 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
6matches
2in Waratek scope33.3%
2protected33.3%
1exploited16.7%
0CISA KEV0.0%
1public PoC16.7%
1EPSS ≥ 0.516.7%
Protected by Waratek
2
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
4
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
33.3%
partly blocked
0
0.0%
not blocked
4
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
16.7%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
83.3%
split by
peak 3 / month
Jul 17Aug 17Sep 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-14735 | Medium | 2017-09-25 | Protected by Waratek | No public exploit | OWASP AntiSamy before 1.5.7 allows XSS via HTML5 entities, as demonstrated by use of : to construct a javascript: URL. |
| CVE-2017-9798 | High | 2017-09-18 | Not applicable | Exploited | Apache httpd allows remote attackers to read secret data from process memory if the Limit directive can be set in a user's .htaccess file, or if httpd.conf has certain misconfigurations, aka Optionsbleed. This affects the Apache HTTP Server through 2.2.34 and 2.4.x through 2.4.27. The attacker sends an unauthenticated OPTIONS HTTP request when attempting to read secret data. This is a use-after-free issue and thus secret data is not always sent, and the specific data depends on many factors including configuration. Exploitation with .htaccess can be blocked with a patch to the ap_limit_section function in server/core.c. |
| CVE-2017-14229 | High | 2017-09-09 | Not applicable | No public exploit | There is an infinite loop in the jpc_dec_tileinit function in jpc/jpc_dec.c of Jasper 2.0.13. It will lead to a remote denial of service attack. |
| CVE-2017-13745 | High | 2017-08-29 | Not applicable | No public exploit | There is a reachable assertion abort in the function jpc_dec_process_sot() in jpc/jpc_dec.c in JasPer 2.0.12 that will lead to a remote denial of service attack by triggering an unexpected jpc_ppmstabtostreams return value, a different vulnerability than CVE-2018-9154. |
| CVE-2017-0379 | High | 2017-08-29 | Not applicable | No public exploit | Libgcrypt before 1.8.1 does not properly consider Curve25519 side-channel attacks, which makes it easier for attackers to discover a secret key, related to cipher/ecc.c and mpi/ec.c. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |