
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
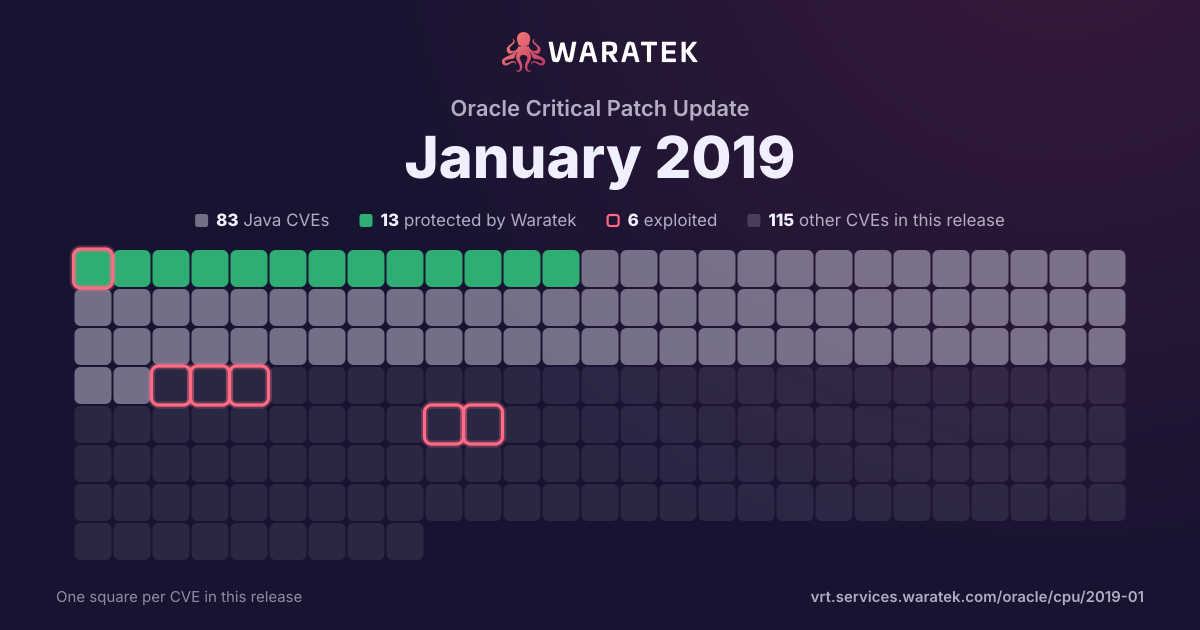
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 1 in Waratek scope · 1 protected · 3 exploited · 0 CISA KEV · 3 EPSS ≥ 0.5
Protected by Waratek
1
25.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
2
50.0%
Not applicable
1
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
25.0%
partly blocked
0
0.0%
not blocked
3
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
75.0%
Working exploit published
1
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Apr 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
May 170
Jun 170
Jul 170
Aug 170
Sep 171
Not applicable1
High1
not blocked1
Exploited1
Oct 170
Nov 170
Dec 170
Jan 181
Outside Waratek scope1
Medium1
not blocked1
Exploited1
Feb 180
Mar 180
Apr 180
May 181
Outside Waratek scope1
Medium1
not blocked1
Exploited1
May 17Jul 17Sep 17Nov 17Jan 18Mar 18May 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-3639 | Medium | 2018-05-22 | Outside Waratek scope | Exploited | Systems with microprocessors utilizing speculative execution and speculative execution of memory reads before the addresses of all prior memory writes are known may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis, aka Speculative Store Bypass (SSB), Variant 4. |
| CVE-2015-9251 | Medium | 2018-01-18 | Outside Waratek scope | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |
| CVE-2017-9798 | High | 2017-09-18 | Not applicable | Exploited | Apache httpd allows remote attackers to read secret data from process memory if the Limit directive can be set in a user's .htaccess file, or if httpd.conf has certain misconfigurations, aka Optionsbleed. This affects the Apache HTTP Server through 2.2.34 and 2.4.x through 2.4.27. The attacker sends an unauthenticated OPTIONS HTTP request when attempting to read secret data. This is a use-after-free issue and thus secret data is not always sent, and the specific data depends on many factors including configuration. Exploitation with .htaccess can be blocked with a patch to the ap_limit_section function in server/core.c. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |