
Oracle Critical Patch Update July 2018
Released July 2018 · Oracle's advisory ↗ · ← Critical Patch Update, April 2018 · Critical Patch Update, October 2018 →
247 CVEs in this release, one square each
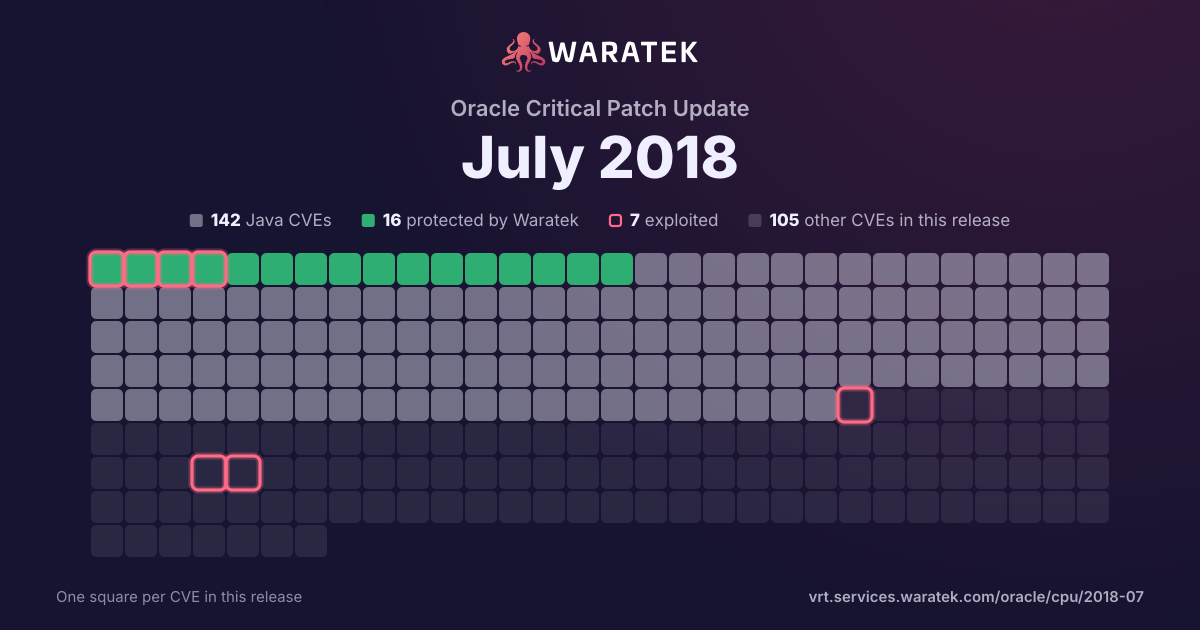
By status
16Protected by Waratek126No exploit published41Outside Waratek scope64Not applicable
7Exploited, marked by the ring
No exploit published. For 125 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
8matches
0in Waratek scope0.0%
0protected0.0%
1exploited12.5%
0CISA KEV0.0%
2public PoC25.0%
1EPSS ≥ 0.512.5%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
8
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
8
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
12.5%
Working exploit published
1
12.5%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
6
75.0%
split by
peak 2 / quarter
Q1 151
Not applicable1
Medium1
not blocked1
Exploited1
Q2 150
Q3 151
Not applicable1
High1
not blocked1
No public exploit1
Q4 150
Q1 160
Q2 162
Not applicable2
Critical1
High1
not blocked2
No public exploit2
Q3 161
Not applicable1
High1
not blocked1
No public exploit1
Q4 160
Q1 172
Not applicable2
High1
Medium1
not blocked2
Working exploit published1
No public exploit1
Q2 171
Not applicable1
High1
not blocked1
No public exploit1
Q1 15Q2 15Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5662 | High | 2017-04-18 | Not applicable | No public exploit | In Apache Batik before 1.9, files lying on the filesystem of the server which uses batik can be revealed to arbitrary users who send maliciously formed SVG files. The file types that can be shown depend on the user context in which the exploitable application is running. If the user is root a full compromise of the server - including confidential or sensitive files - would be possible. XXE can also be used to attack the availability of the server via denial of service as the references within a xml document can trivially trigger an amplification attack. |
| CVE-2017-6074 | High | 2017-02-18 | Not applicable | Working exploit published | The dccp_rcv_state_process function in net/dccp/input.c in the Linux kernel through 4.9.11 mishandles DCCP_PKT_REQUEST packet data structures in the LISTEN state, which allows local users to obtain root privileges or cause a denial of service (double free) via an application that makes an IPV6_RECVPKTINFO setsockopt system call. |
| CVE-2016-4055 | Medium | 2017-01-23 | Not applicable | No public exploit | The duration function in the moment package before 2.11.2 for Node.js allows remote attackers to cause a denial of service (CPU consumption) via a long string, aka a "regular expression Denial of Service (ReDoS)." |
| CVE-2016-3506 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the JDBC component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2; the Oracle Retail Xstore Point of Service 5.5, 6.0, 6.5, 7.0, 7.1, 15.0, and 16.0; the Oracle Retail Warehouse Management System 14.04, 14.1.3, and 15.0.1; the Oracle Retail Workforce Management 1.60.7, and 1.64.0; the Oracle Retail Clearance Optimization Engine 13.4; the Oracle Retail Markdown Optimization 13.4 and 14.0; and Oracle Retail Merchandising System 16.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-2099 | Critical | 2016-05-13 | Not applicable | No public exploit | Use-after-free vulnerability in validators/DTD/DTDScanner.cpp in Apache Xerces C++ 3.1.3 and earlier allows context-dependent attackers to have unspecified impact via an invalid character in an XML document. |
| CVE-2016-2176 | High | 2016-05-05 | Not applicable | No public exploit | The X509_NAME_oneline function in crypto/x509/x509_obj.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to obtain sensitive information from process stack memory or cause a denial of service (buffer over-read) via crafted EBCDIC ASN.1 data. |
| CVE-2015-5600 | High | 2015-08-03 | Not applicable | No public exploit | The kbdint_next_device function in auth2-chall.c in sshd in OpenSSH through 6.9 does not properly restrict the processing of keyboard-interactive devices within a single connection, which makes it easier for remote attackers to conduct brute-force attacks or cause a denial of service (CPU consumption) via a long and duplicative list in the ssh -oKbdInteractiveDevices option, as demonstrated by a modified client that provides a different password for each pam element on this list. |
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |