
Oracle Critical Patch Update July 2018
Released July 2018 · Oracle's advisory ↗ · ← Critical Patch Update, April 2018 · Critical Patch Update, October 2018 →
247 CVEs in this release, one square each
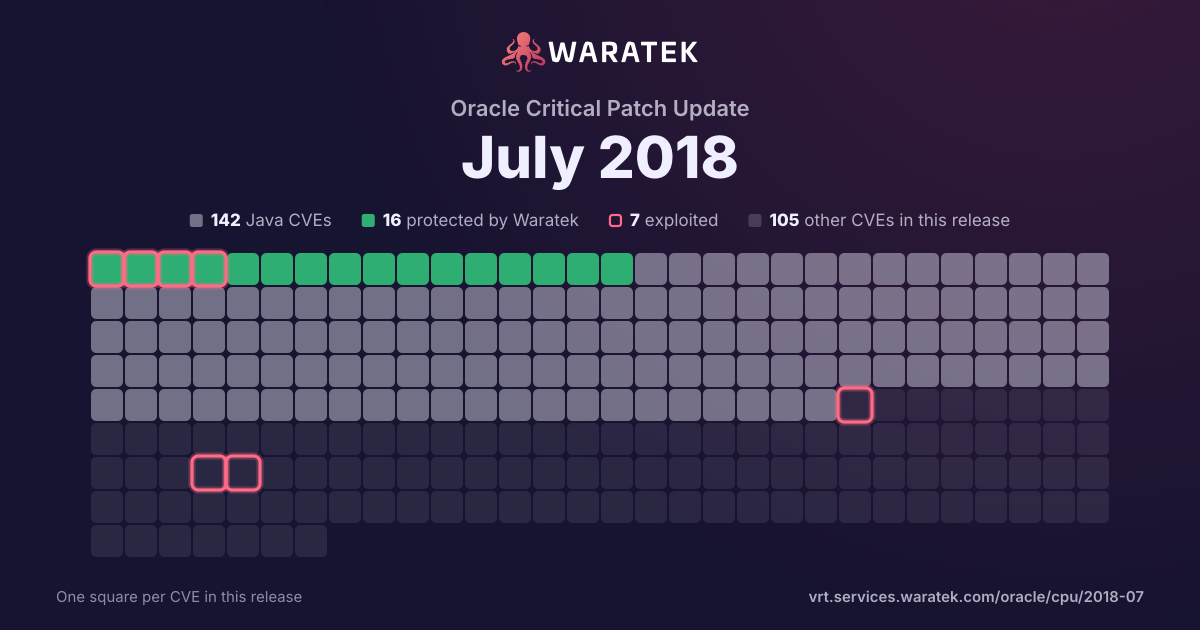
By status
16Protected by Waratek126No exploit published41Outside Waratek scope64Not applicable
7Exploited, marked by the ring
No exploit published. For 125 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 2 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 1 EPSS ≥ 0.5
3matches
2in Waratek scope66.7%
2protected66.7%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
1EPSS ≥ 0.533.3%
Protected by Waratek
2
66.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
66.7%
partly blocked
0
0.0%
not blocked
1
33.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
33.3%
No public exploit
2
66.7%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-8013 | Critical | 2018-05-24 | Protected by Waratek | No public exploit | In Apache Batik 1.x before 1.10, when deserializing subclass of `AbstractDocument`, the class takes a string from the inputStream as the class name which then use it to call the no-arg constructor of the class. Fix was to check the class type before calling newInstance in deserialization. |
| CVE-2018-1000300 | Critical | 2018-05-24 | Not applicable | No public exploit | curl version curl 7.54.1 to and including curl 7.59.0 contains a CWE-122: Heap-based Buffer Overflow vulnerability in denial of service and more that can result in curl might overflow a heap based memory buffer when closing down an FTP connection with very long server command replies.. This vulnerability appears to have been fixed in curl < 7.54.1 and curl >= 7.60.0. |
| CVE-2018-1275 | Critical | 2018-04-11 | Protected by Waratek | Forecast only | Spring Framework, versions 5.0 prior to 5.0.5 and versions 4.3 prior to 4.3.16 and older unsupported versions, allow applications to expose STOMP over WebSocket endpoints with a simple, in-memory STOMP broker through the spring-messaging module. A malicious user (or attacker) can craft a message to the broker that can lead to a remote code execution attack. This CVE addresses the partial fix for CVE-2018-1270 in the 4.3.x branch of the Spring Framework. |