
Oracle Critical Patch Update July 2018
Released July 2018 · Oracle's advisory ↗ · ← Critical Patch Update, April 2018 · Critical Patch Update, October 2018 →
247 CVEs in this release, one square each
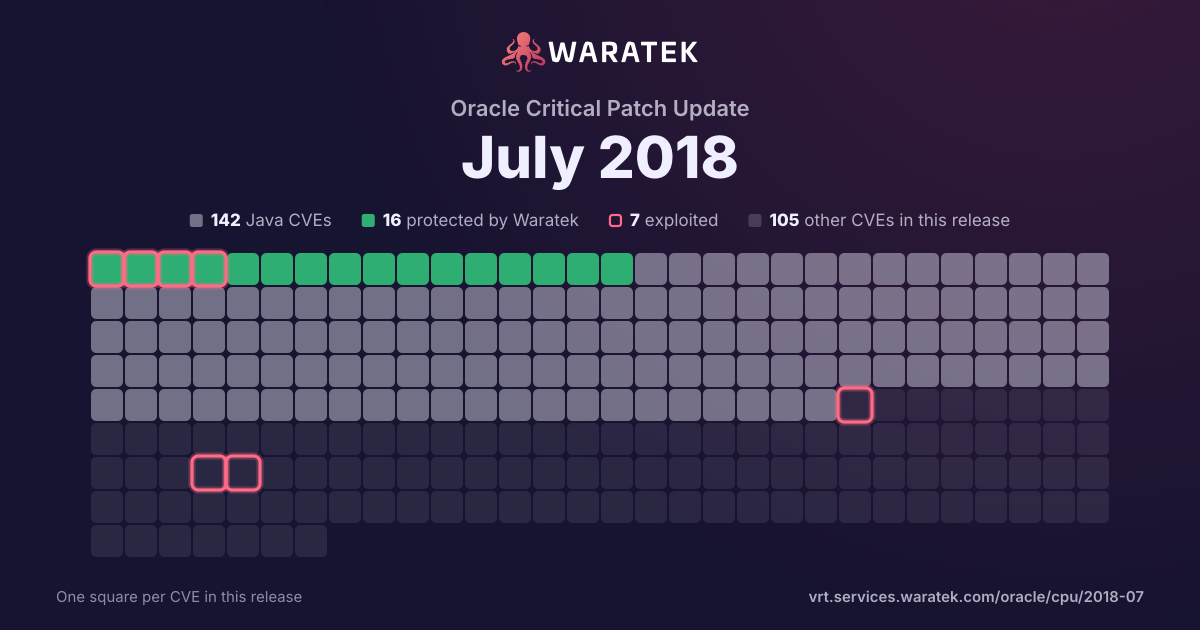
By status
18Protected by Waratek2Mitigation candidate132No exploit published7Outside Waratek scope88Not applicable
7Exploited, marked by the ring
No exploit published. For 127 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 1 protected · 1 exploited · 1 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
2
28.6%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
5
71.4%
blocked by ARMR today
1
14.3%
partly blocked
1
14.3%
not blocked
5
71.4%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
14.3%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
6
85.7%
split by
peak 5 / month
Apr 171
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
May 170
Jun 170
Jul 170
Aug 170
Sep 170
Oct 171
Protected by Waratek1
High1
partly blocked1
Exploited1
Nov 170
Dec 170
Jan 180
Feb 180
Mar 180
Apr 180
May 180
Jun 180
Jul 185
No exploit published5
High5
not blocked5
No public exploit5
May 17Jul 17Sep 17Nov 17Jan 18Mar 18May 18Jul 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-3051 | High | 2018-07-18 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.3.0, 14.0.0 and 14.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Enterprise Limits and Collateral Management. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data as well as unauthorized access to critical data or complete access to all Oracle FLEXCUBE Enterprise Limits and Collateral Management accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2018-3050 | High | 2018-07-18 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Corporate Lending component of Oracle Financial Services Applications (subcomponent: Core module). Supported versions that are affected are 12.3.0, 12.4.0, 12.5.0, 14.0.0 and 14.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Banking Corporate Lending. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Banking Corporate Lending accessible data as well as unauthorized access to critical data or complete access to all Oracle Banking Corporate Lending accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2018-3035 | High | 2018-07-18 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Investor Servicing component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 12.0.4, 12.1.0, 12.3.0 and 12.4.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Investor Servicing. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Investor Servicing accessible data as well as unauthorized access to critical data or complete access to all Oracle FLEXCUBE Investor Servicing accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2018-3027 | High | 2018-07-18 | No exploit published | No public exploit | Vulnerability in the Oracle Banking Payments component of Oracle Financial Services Applications (subcomponent: Payments Core). Supported versions that are affected are 12.2.0, 12.3.0, 12.4.0, 12.5.0 and 14.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Banking Payments. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Banking Payments accessible data as well as unauthorized access to critical data or complete access to all Oracle Banking Payments accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2018-3015 | High | 2018-07-18 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Universal Banking component of Oracle Financial Services Applications (subcomponent: Infrastructure). Supported versions that are affected are 11.3.0, 11.4.0, 12.0.1, 12.0.2, 12.0.3, 12.1.0, 12.2.0, 12.3.0, 12.4.0, 14.0.0 and 14.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Universal Banking. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Universal Banking accessible data as well as unauthorized access to critical data or complete access to all Oracle FLEXCUBE Universal Banking accessible data. CVSS 3.0 Base Score 8.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:N). |
| CVE-2017-12617 | High | 2017-10-04 | Protected by Waratek | Exploited | When running Apache Tomcat versions 9.0.0.M1 to 9.0.0, 8.5.0 to 8.5.22, 8.0.0.RC1 to 8.0.46 and 7.0.0 to 7.0.81 with HTTP PUTs enabled (e.g. via setting the readonly initialisation parameter of the Default servlet to false) it was possible to upload a JSP file to the server via a specially crafted request. This JSP could then be requested and any code it contained would be executed by the server. |
| CVE-2017-5662 | High | 2017-04-18 | Protected by Waratek | No public exploit | In Apache Batik before 1.9, files lying on the filesystem of the server which uses batik can be revealed to arbitrary users who send maliciously formed SVG files. The file types that can be shown depend on the user context in which the exploitable application is running. If the user is root a full compromise of the server - including confidential or sensitive files - would be possible. XXE can also be used to attack the availability of the server via denial of service as the references within a xml document can trivially trigger an amplification attack. |