
Oracle Critical Patch Update April 2018
Released April 2018 · Oracle's advisory ↗ · ← Critical Patch Update, January 2018 · Critical Patch Update, July 2018 →
165 CVEs in this release, one square each
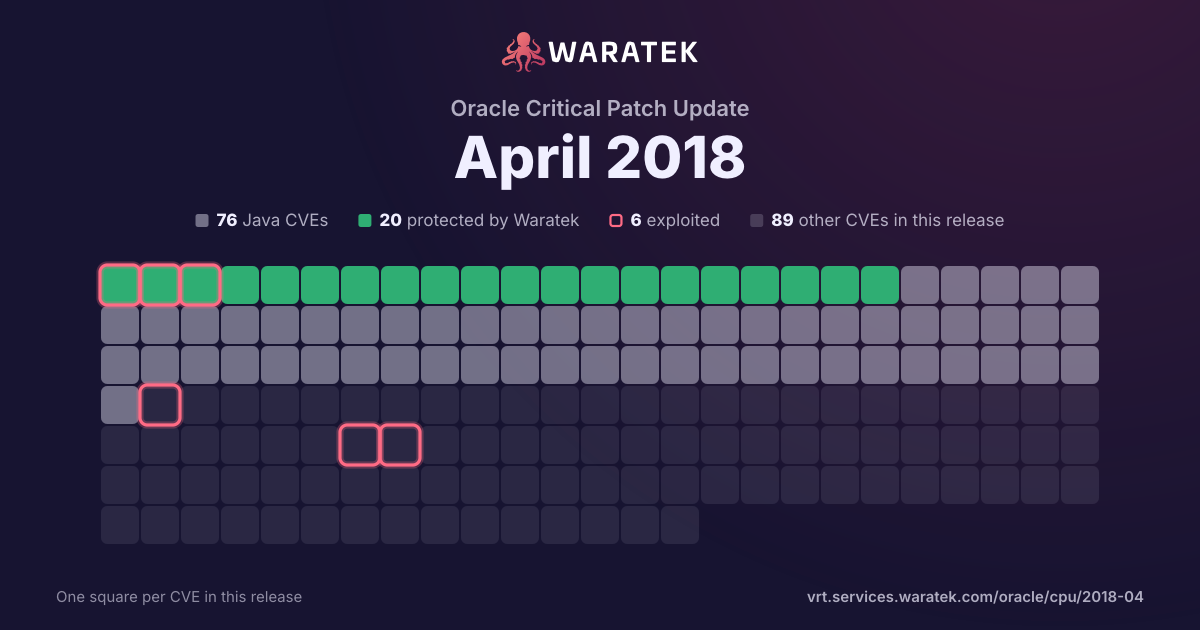
By status
20Protected by Waratek2Mitigation candidate54No exploit published30Outside Waratek scope59Not applicable
6Exploited, marked by the ring
No exploit published. For 52 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 1 in Waratek scope · 0 protected · 1 exploited · 1 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
2matches
1in Waratek scope50.0%
0protected0.0%
1exploited50.0%
1CISA KEV50.0%
1public PoC50.0%
1EPSS ≥ 0.550.0%
Protected by Waratek
1
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
1
50.0%
not blocked
1
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
50.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
50.0%
split by
peak 2 / month
Oct 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-13082 | High | 2017-10-17 | Not applicable | No public exploit | Wi-Fi Protected Access (WPA and WPA2) that supports IEEE 802.11r allows reinstallation of the Pairwise Transient Key (PTK) Temporal Key (TK) during the fast BSS transmission (FT) handshake, allowing an attacker within radio range to replay, decrypt, or spoof frames. |
| CVE-2017-12617 | High | 2017-10-04 | Protected by Waratek | Exploited | When running Apache Tomcat versions 9.0.0.M1 to 9.0.0, 8.5.0 to 8.5.22, 8.0.0.RC1 to 8.0.46 and 7.0.0 to 7.0.81 with HTTP PUTs enabled (e.g. via setting the readonly initialisation parameter of the Default servlet to false) it was possible to upload a JSP file to the server via a specially crafted request. This JSP could then be requested and any code it contained would be executed by the server. |