
Oracle Critical Patch Update April 2018
Released April 2018 · Oracle's advisory ↗ · ← Critical Patch Update, January 2018 · Critical Patch Update, July 2018 →
165 CVEs in this release, one square each
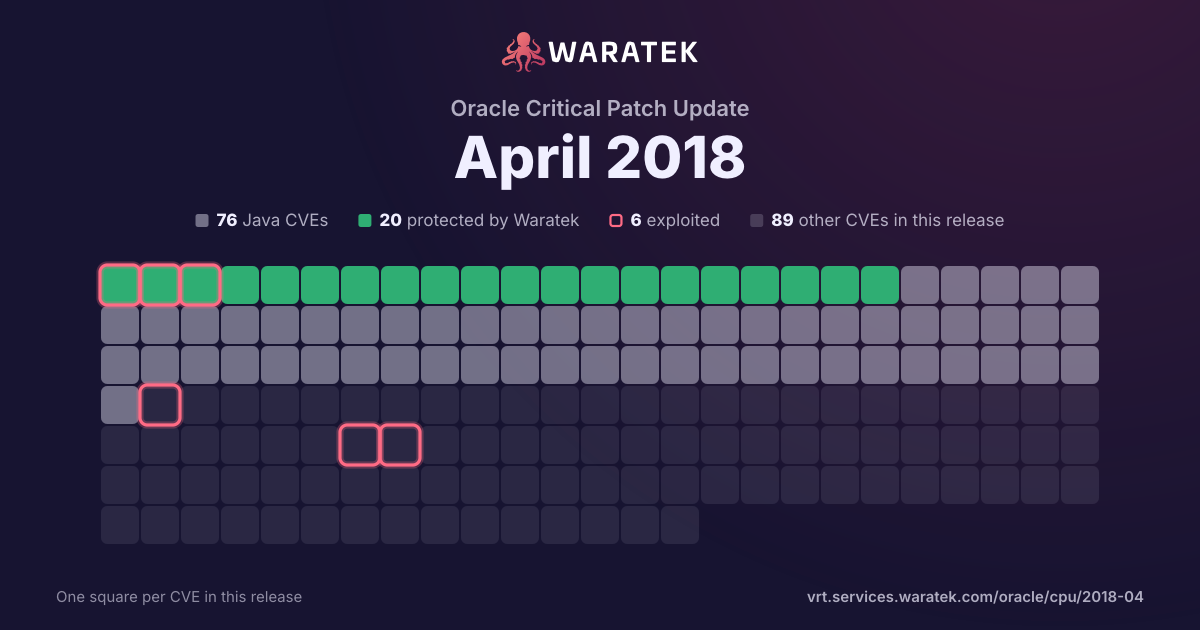
By status
22Protected by Waratek2Mitigation candidate59No exploit published6Outside Waratek scope76Not applicable
6Exploited, marked by the ring
No exploit published. For 54 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 0 protected · 1 exploited · 1 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
1
20.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
4
80.0%
blocked by ARMR today
0
0.0%
partly blocked
1
20.0%
not blocked
4
80.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
20.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
80.0%
split by
peak 3 / month
Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17Dec 17Jan 18Feb 18Mar 18Apr 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-2876 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Integration Bus component of Oracle Retail Applications (subcomponent: RIB Kernal(Apache Commons Collections)). The supported version that is affected is 13.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Integration Bus. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Retail Integration Bus, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Retail Integration Bus accessible data as well as unauthorized read access to a subset of Oracle Retail Integration Bus accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Integration Bus. CVSS 3.0 Base Score 7.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:L). |
| CVE-2018-2862 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Point-of-Service component of Oracle Retail Applications (subcomponent: User Interface). Supported versions that are affected are 13.3.8, 13.4.9, 14.0.4 and 14.1.3. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Retail Point-of-Service. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Point-of-Service accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Point-of-Service accessible data. CVSS 3.0 Base Score 7.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2018-2840 | High | 2018-04-19 | No exploit published | No public exploit | Vulnerability in the Oracle Retail Xstore Point of Service component of Oracle Retail Applications (subcomponent: Xstore Office). Supported versions that are affected are 6.5.11, 7.0.6, 7.1.6, 15.0.1 and 16.0.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Retail Xstore Point of Service. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Retail Xstore Point of Service accessible data as well as unauthorized update, insert or delete access to some of Oracle Retail Xstore Point of Service accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Retail Xstore Point of Service. CVSS 3.0 Base Score 7.6 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:L/A:L). |
| CVE-2017-12617 | High | 2017-10-04 | Protected by Waratek | Exploited | When running Apache Tomcat versions 9.0.0.M1 to 9.0.0, 8.5.0 to 8.5.22, 8.0.0.RC1 to 8.0.46 and 7.0.0 to 7.0.81 with HTTP PUTs enabled (e.g. via setting the readonly initialisation parameter of the Default servlet to false) it was possible to upload a JSP file to the server via a specially crafted request. This JSP could then be requested and any code it contained would be executed by the server. |
| CVE-2017-5664 | High | 2017-06-06 | No exploit published | No public exploit | The error page mechanism of the Java Servlet Specification requires that, when an error occurs and an error page is configured for the error that occurred, the original request and response are forwarded to the error page. This means that the request is presented to the error page with the original HTTP method. If the error page is a static file, expected behaviour is to serve content of the file as if processing a GET request, regardless of the actual HTTP method. The Default Servlet in Apache Tomcat 9.0.0.M1 to 9.0.0.M20, 8.5.0 to 8.5.14, 8.0.0.RC1 to 8.0.43 and 7.0.0 to 7.0.77 did not do this. Depending on the original request this could lead to unexpected and undesirable results for static error pages including, if the DefaultServlet is configured to permit writes, the replacement or removal of the custom error page. Notes for other user provided error pages: (1) Unless explicitly coded otherwise, JSPs ignore the HTTP method. JSPs used as error pages must must ensure that they handle any error dispatch as a GET request, regardless of the actual method. (2) By default, the response generated by a Servlet does depend on the HTTP method. Custom Servlets used as error pages must ensure that they handle any error dispatch as a GET request, regardless of the actual method. |