
Oracle Critical Patch Update January 2018
Released January 2018 · Oracle's advisory ↗ · ← Critical Patch Update, October 2017 · Critical Patch Update, April 2018 →
197 CVEs in this release, one square each
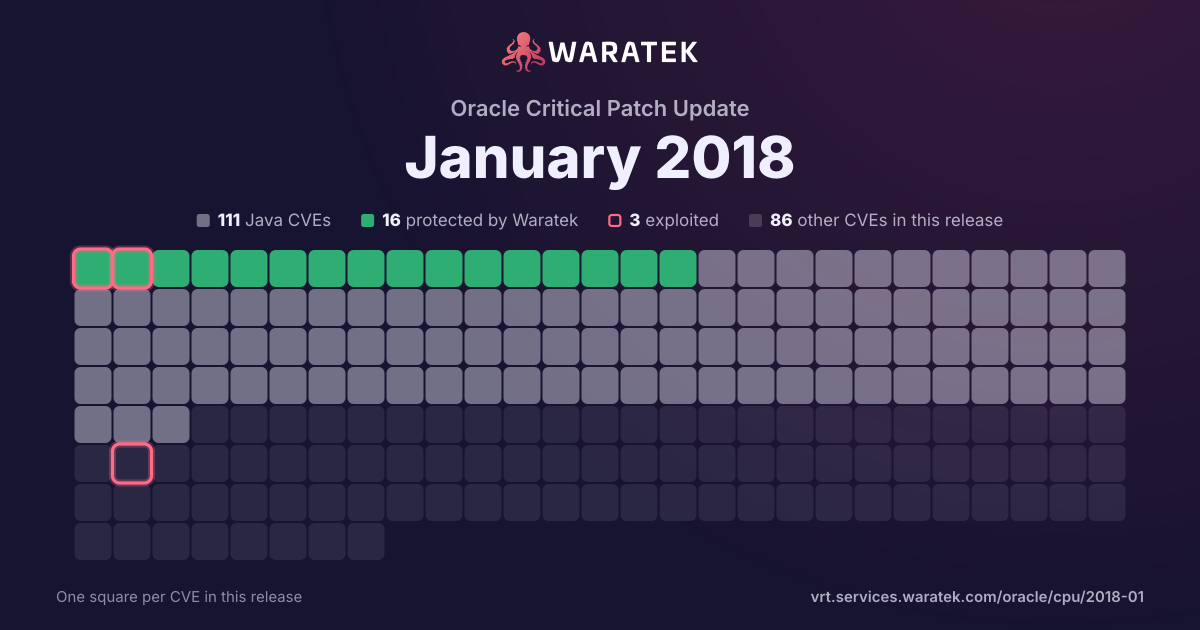
By status
16Protected by Waratek1Mitigation candidate94No exploit published25Outside Waratek scope61Not applicable
3Exploited, marked by the ring
No exploit published. For 94 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 3 public PoC · 2 EPSS ≥ 0.5
8matches
0in Waratek scope0.0%
0protected0.0%
1exploited12.5%
0CISA KEV0.0%
3public PoC37.5%
2EPSS ≥ 0.525.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
8
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
8
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
12.5%
Working exploit published
2
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
62.5%
split by
peak 3 / quarter
Q1 161
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 161
Not applicable1
Medium1
not blocked1
Working exploit published1
Q3 161
Not applicable1
High1
not blocked1
No public exploit1
Q4 160
Q1 170
Q2 173
Not applicable3
Critical1
Medium2
not blocked3
No public exploit3
Q3 172
Not applicable2
High2
not blocked2
Exploited1
Working exploit published1
Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-9798 | High | 2017-09-18 | Not applicable | Exploited | Apache httpd allows remote attackers to read secret data from process memory if the Limit directive can be set in a user's .htaccess file, or if httpd.conf has certain misconfigurations, aka Optionsbleed. This affects the Apache HTTP Server through 2.2.34 and 2.4.x through 2.4.27. The attacker sends an unauthenticated OPTIONS HTTP request when attempting to read secret data. This is a use-after-free issue and thus secret data is not always sent, and the specific data depends on many factors including configuration. Exploitation with .htaccess can be blocked with a patch to the ap_limit_section function in server/core.c. |
| CVE-2017-0781 | High | 2017-09-14 | Not applicable | Working exploit published | A remote code execution vulnerability in the Android system (bluetooth). Product: Android. Versions: 4.4.4, 5.0.2, 5.1.1, 6.0, 6.0.1, 7.0, 7.1.1, 7.1.2, 8.0. Android ID: A-63146105. |
| CVE-2017-9072 | Medium | 2017-05-18 | Not applicable | No public exploit | Two CalendarXP products have XSS in common parts of HTML files. CalendarXP FlatCalendarXP through 9.9.290 has XSS in iflateng.htm and nflateng.htm. CalendarXP PopCalendarXP through 9.8.308 has XSS in ipopeng.htm and npopeng.htm. |
| CVE-2017-5461 | Critical | 2017-05-11 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.21.4, 3.22.x through 3.28.x before 3.28.4, 3.29.x before 3.29.5, and 3.30.x before 3.30.1 allows remote attackers to cause a denial of service (out-of-bounds write) or possibly have unspecified other impact by leveraging incorrect base64 operations. |
| CVE-2017-3732 | Medium | 2017-05-04 | Not applicable | No public exploit | There is a carry propagating bug in the x86_64 Montgomery squaring procedure in OpenSSL 1.0.2 before 1.0.2k and 1.1.0 before 1.1.0d. No EC algorithms are affected. Analysis suggests that attacks against RSA and DSA as a result of this defect would be very difficult to perform and are not believed likely. Attacks against DH are considered just feasible (although very difficult) because most of the work necessary to deduce information about a private key may be performed offline. The amount of resources required for such an attack would be very significant and likely only accessible to a limited number of attackers. An attacker would additionally need online access to an unpatched system using the target private key in a scenario with persistent DH parameters and a private key that is shared between multiple clients. For example this can occur by default in OpenSSL DHE based SSL/TLS ciphersuites. Note: This issue is very similar to CVE-2015-3193 but must be treated as a separate problem. |
| CVE-2016-2179 | High | 2016-09-16 | Not applicable | No public exploit | The DTLS implementation in OpenSSL before 1.1.0 does not properly restrict the lifetime of queue entries associated with unused out-of-order messages, which allows remote attackers to cause a denial of service (memory consumption) by maintaining many crafted DTLS sessions simultaneously, related to d1_lib.c, statem_dtls.c, statem_lib.c, and statem_srvr.c. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-0704 | Medium | 2016-03-02 | Not applicable | No public exploit | An oracle protection mechanism in the get_client_master_key function in s2_srvr.c in the SSLv2 implementation in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a overwrites incorrect MASTER-KEY bytes during use of export cipher suites, which makes it easier for remote attackers to decrypt TLS ciphertext data by leveraging a Bleichenbacher RSA padding oracle, a related issue to CVE-2016-0800. |