
WaratekVRT Sign in

Oracle Critical Patch Update January 2018

Released January 2018 · Oracle's advisory ↗ · ← Critical Patch Update, October 2017 · Critical Patch Update, April 2018 →

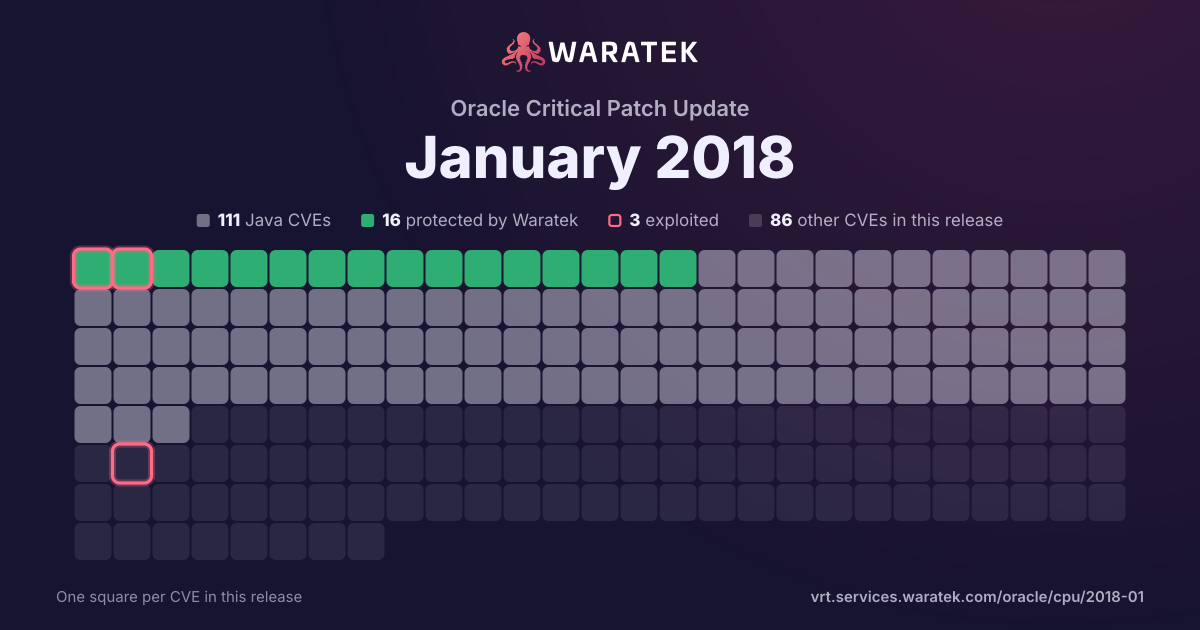
197 CVEs in this release, one square each
Protected by Waratek, exploitedProtected by Waratek, exploitedProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekProtected by WaratekMitigation candidateNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedNo exploit publishedOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeOutside Waratek scopeNot applicable, exploitedNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicableNot applicable
Share this chart Oracle Critical Patch Update January 2018, one square per CVE: 111 Java CVEs, 16 protected by Waratek, 3 exploited, 86 other CVEs in this release.

Download the image

By status

No exploit published. For 94 of them, Oracle's security advisory is the source of public detail.

Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.

Reset
More filters
Columns
Including CVEs outside Waratek scope✕
Overview 2 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC
2matches 0in Waratek scope0.0% 0protected0.0% 0exploited0.0% 0CISA KEV0.0% 0public PoC0.0%
Protected by Waratek 0 0.0% Rule in development 0 0.0% Mitigation candidate 0 0.0% No exploit published 0 0.0% Outside Waratek scope 1 50.0% Not applicable 1 50.0% Withdrawn CVE 0 0.0%
Critical 0 0.0% High 0 0.0% Medium 2 100.0% Low 0 0.0% None 0 0.0% Unknown 0 0.0%
blocked by ARMR today 0 0.0% partly blocked 0 0.0% not blocked 2 100.0% not established 0 0.0% unrecorded 0 0.0%
Exploited 0 0.0% Working exploit published 0 0.0% Proof of concept only 0 0.0% Forecast only 2 100.0% No public exploit 0 0.0%
split by peak 1 / quarter
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17
2 matches Sign in to download these CVEs as CSV or JSON, or to follow them in a feed.
CVE Severity Published▾ Status Exploitation Description
CVE-2017-3737 Medium 2017-12-07 Not applicable Forecast only OpenSSL 1.0.2 (starting from version 1.0.2b) introduced an "error state" mechanism. The intent was that if a fatal error occurred during a handshake then OpenSSL would move into the error state and would immediately fail if you attempted to continue the handshake. This works as designed for the explicit handshake functions (SSL_do_handshake(), SSL_accept() and SSL_connect()), however due to a bug it does not work correctly if SSL_read() or SSL_write() is called directly. In that scenario, if the handshake fails then a fatal error will be returned in the initial function call. If SSL_read()/SSL_write() is subsequently called by the application for the same SSL object then it will succeed and the data is passed without being decrypted/encrypted directly from the SSL/TLS record layer. In order to exploit this issue an application bug would have to be present that resulted in a call to SSL_read()/SSL_write() being issued after having already received a fatal error. OpenSSL version 1.0.2b-1.0.2m are affected. Fixed in OpenSSL 1.0.2n. OpenSSL 1.1.0 is not affected.
CVE-2013-2566 Medium 2013-03-15 Outside Waratek scope Forecast only The RC4 algorithm, as used in the TLS protocol and SSL protocol, has many single-byte biases, which makes it easier for remote attackers to conduct plaintext-recovery attacks via statistical analysis of ciphertext in a large number of sessions that use the same plaintext.