
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
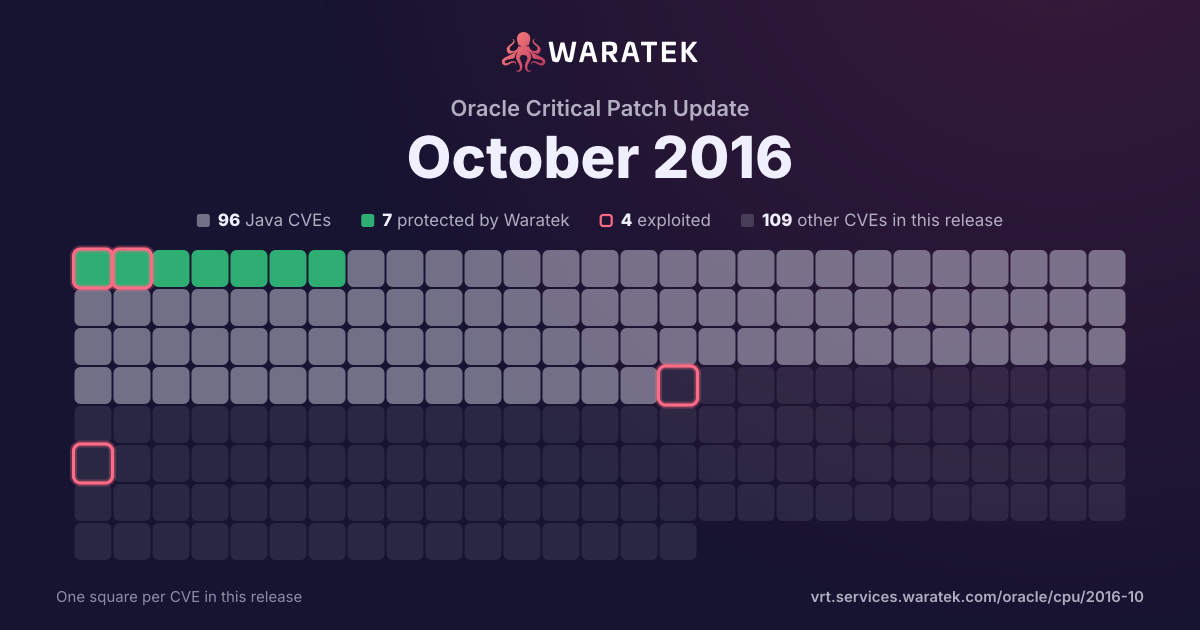
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
6matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC16.7%
1EPSS ≥ 0.516.7%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
5
83.3%
Not applicable
1
16.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
16.7%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
83.3%
split by
peak 6 / month
Jan 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2015-0411 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier, and 5.6.21 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Server : Security : Encryption. |
| CVE-2015-0409 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.21 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2015-0382 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier and 5.6.21 and earlier allows remote attackers to affect availability via unknown vectors related to Server : Replication, a different vulnerability than CVE-2015-0381. |
| CVE-2015-0381 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier and 5.6.21 and earlier allows remote attackers to affect availability via unknown vectors related to Server : Replication, a different vulnerability than CVE-2015-0382. |
| CVE-2014-3571 | Medium | 2015-01-09 | Not applicable | No public exploit | OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via a crafted DTLS message that is processed with a different read operation for the handshake header than for the handshake body, related to the dtls1_get_record function in d1_pkt.c and the ssl3_read_n function in s3_pkt.c. |