
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
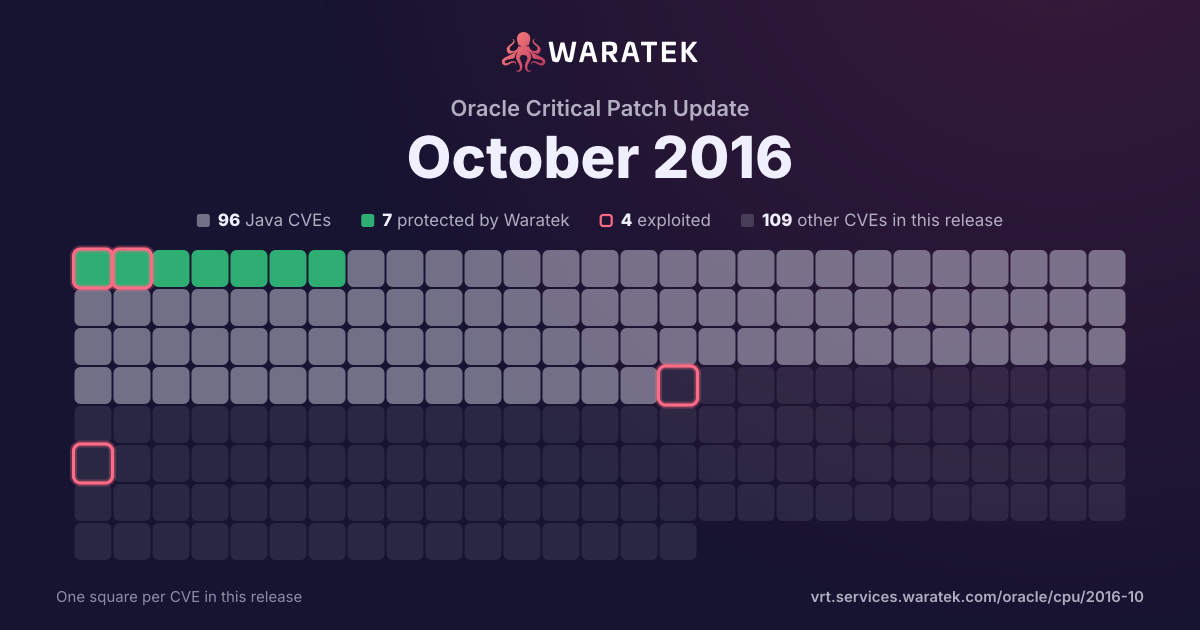
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 in Waratek scope · 1 protected · 1 exploited · 0 CISA KEV · 1 EPSS ≥ 0.5
Protected by Waratek
1
25.0%
Rule in development
0
0.0%
Mitigation candidate
1
25.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
0
0.0%
Withdrawn CVE
2
50.0%
blocked by ARMR today
1
25.0%
partly blocked
0
0.0%
not blocked
3
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
25.0%
Working exploit published
3
75.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / month
Nov 16Jan 17Mar 17May 17Jul 17Sep 17Nov 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-5617 | Unknown | 2016-10-25 | Withdrawn CVE | Working exploit published | Rejected reason: DO NOT USE THIS CANDIDATE NUMBER. ConsultIDs: CVE-2016-6664. Reason: This candidate is a reservation duplicate of CVE-2016-6664. Notes: All CVE users should reference CVE-2016-6664 instead of this candidate. All references and descriptions in this candidate have been removed to prevent accidental usage |
| CVE-2016-5616 | Unknown | 2016-10-25 | Withdrawn CVE | Working exploit published | Rejected reason: DO NOT USE THIS CANDIDATE NUMBER. ConsultIDs: CVE-2016-6663. Reason: This candidate is a reservation duplicate of CVE-2016-6663. Notes: All CVE users should reference CVE-2016-6663 instead of this candidate. All references and descriptions in this candidate have been removed to prevent accidental usage |
| CVE-2016-3473 | High | 2016-10-25 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality via unknown vectors. |