
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
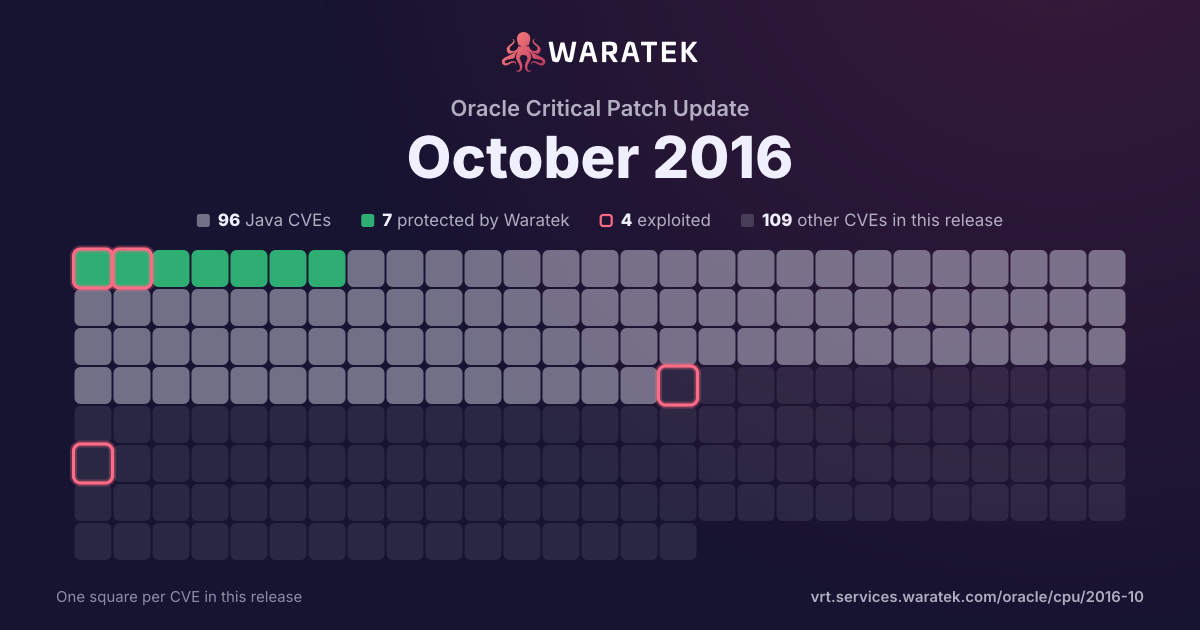
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 202 matches · 95 in Waratek scope · 6 protected · 3 exploited · 1 CISA KEV · 10 public PoC · 9 EPSS ≥ 0.5
202matches
95in Waratek scope47.0%
6protected3.0%
3exploited1.5%
1CISA KEV0.5%
10public PoC5.0%
9EPSS ≥ 0.54.5%
Protected by Waratek
6
3.0%
Rule in development
0
0.0%
Mitigation candidate
2
1.0%
No exploit published
87
43.1%
Outside Waratek scope
39
19.3%
Not applicable
66
32.7%
Withdrawn CVE
2
1.0%
blocked by ARMR today
6
3.0%
partly blocked
0
0.0%
not blocked
196
97.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
1.5%
Working exploit published
7
3.5%
Proof of concept only
0
0.0%
Forecast only
2
1.0%
No public exploit
190
94.1%
split by
peak 158 / quarter
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 131
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 144
Protected by Waratek1
No exploit published1
Outside Waratek scope2
Medium4
blocked by ARMR today1
not blocked3
No public exploit4
Q2 146
Protected by Waratek2
Mitigation candidate1
No exploit published2
Outside Waratek scope1
High2
Medium4
blocked by ARMR today2
not blocked4
Exploited1
Working exploit published1
No public exploit4
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 142
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
No public exploit2
Q1 159
Outside Waratek scope6
Not applicable3
High3
Medium6
not blocked9
Working exploit published1
No public exploit8
Q2 155
Outside Waratek scope4
Not applicable1
Medium5
not blocked5
No public exploit5
Q3 152
Outside Waratek scope2
Critical1
Medium1
not blocked2
Working exploit published1
No public exploit1
Q4 152
Outside Waratek scope2
Medium2
not blocked2
No public exploit2
Q1 163
Outside Waratek scope3
High2
Medium1
not blocked3
No public exploit3
Q2 163
Protected by Waratek1
Not applicable2
High2
Medium1
blocked by ARMR today1
not blocked2
Exploited1
Working exploit published1
No public exploit1
Q3 165
Protected by Waratek1
Outside Waratek scope1
Not applicable3
Critical1
High4
blocked by ARMR today1
not blocked4
Exploited1
Forecast only1
No public exploit3
Q4 16158
Protected by Waratek1
Mitigation candidate1
No exploit published83
Outside Waratek scope15
Not applicable56
Withdrawn CVE2
Critical10
High45
Medium85
Low16
Unknown2
blocked by ARMR today1
not blocked157
Working exploit published3
No public exploit155
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-2067 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/authenticator/FormAuthenticator.java in the form authentication feature in Apache Tomcat 6.0.21 through 6.0.36 and 7.x before 7.0.33 does not properly handle the relationships between authentication requirements and sessions, which allows remote attackers to inject a request into a session by sending this request during completion of the login form, a variant of a session fixation attack. |
| CVE-2013-2566 | Medium | 2013-03-15 | Outside Waratek scope | Forecast only | The RC4 algorithm, as used in the TLS protocol and SSL protocol, has many single-byte biases, which makes it easier for remote attackers to conduct plaintext-recovery attacks via statistical analysis of ciphertext in a large number of sessions that use the same plaintext. |