
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
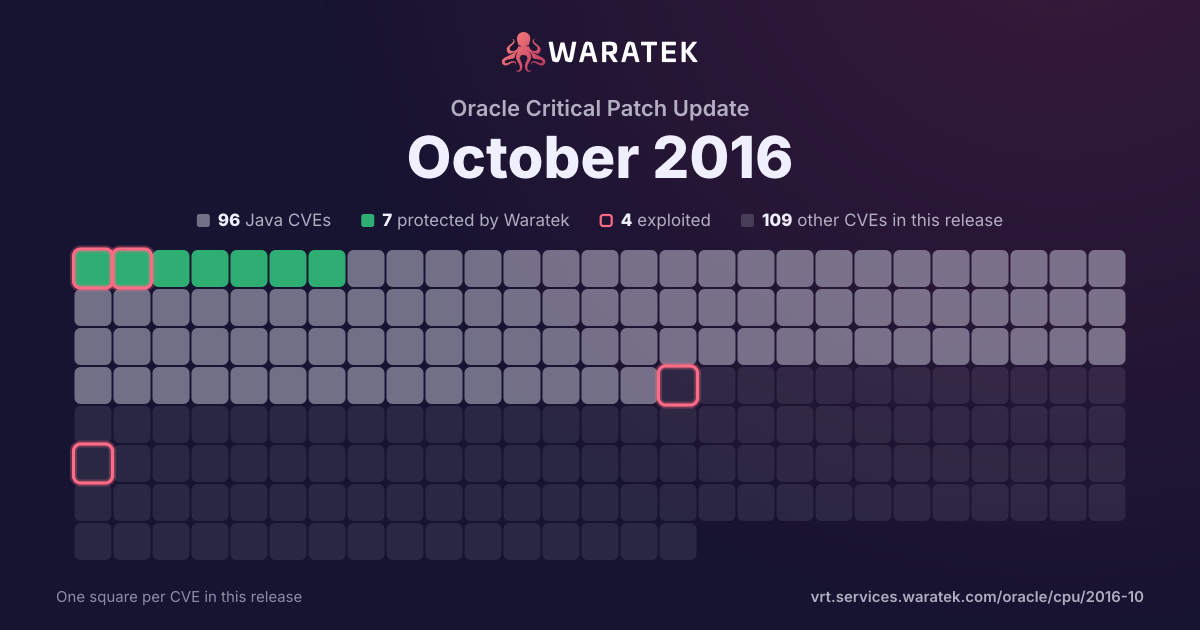
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 6 in Waratek scope · 3 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
6in Waratek scope66.7%
3protected33.3%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
3
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
3
33.3%
Outside Waratek scope
3
33.3%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
33.3%
partly blocked
0
0.0%
not blocked
6
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 4 / month
Jun 131
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Jul 130
Aug 130
Sep 130
Oct 130
Nov 130
Dec 130
Jan 140
Feb 143
Protected by Waratek1
No exploit published1
Outside Waratek scope1
Medium3
blocked by ARMR today1
not blocked2
No public exploit3
Mar 141
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Apr 140
May 144
Protected by Waratek2
No exploit published2
Medium4
blocked by ARMR today2
not blocked2
No public exploit4
Jun 13Jul 13Aug 13Sep 13Oct 13Nov 13Dec 13Jan 14Feb 14Mar 14Apr 14May 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0119 | Medium | 2014-05-31 | Protected by Waratek | No public exploit | Apache Tomcat before 6.0.40, 7.x before 7.0.54, and 8.x before 8.0.6 does not properly constrain the class loader that accesses the XML parser used with an XSLT stylesheet, which allows remote attackers to (1) read arbitrary files via a crafted web application that provides an XML external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue, or (2) read files associated with different web applications on a single Tomcat instance via a crafted web application. |
| CVE-2014-0099 | Medium | 2014-05-31 | No exploit published | No public exploit | Integer overflow in java/org/apache/tomcat/util/buf/Ascii.java in Apache Tomcat before 6.0.40, 7.x before 7.0.53, and 8.x before 8.0.4, when operated behind a reverse proxy, allows remote attackers to conduct HTTP request smuggling attacks via a crafted Content-Length HTTP header. |
| CVE-2014-0096 | Medium | 2014-05-31 | Protected by Waratek | No public exploit | java/org/apache/catalina/servlets/DefaultServlet.java in the default servlet in Apache Tomcat before 6.0.40, 7.x before 7.0.53, and 8.x before 8.0.4 does not properly restrict XSLT stylesheets, which allows remote attackers to bypass security-manager restrictions and read arbitrary files via a crafted web application that provides an XML external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue. |
| CVE-2014-0075 | Medium | 2014-05-31 | No exploit published | No public exploit | Integer overflow in the parseChunkHeader function in java/org/apache/coyote/http11/filters/ChunkedInputFilter.java in Apache Tomcat before 6.0.40, 7.x before 7.0.53, and 8.x before 8.0.4 allows remote attackers to cause a denial of service (resource consumption) via a malformed chunk size in chunked transfer coding of a request during the streaming of data. |
| CVE-2014-2532 | Medium | 2014-03-18 | Outside Waratek scope | No public exploit | sshd in OpenSSH before 6.6 does not properly support wildcards on AcceptEnv lines in sshd_config, which allows remote attackers to bypass intended environment restrictions by using a substring located before a wildcard character. |
| CVE-2013-4590 | Medium | 2014-02-26 | Protected by Waratek | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.50, and 8.x before 8.0.0-RC10 allows attackers to obtain "Tomcat internals" information by leveraging the presence of an untrusted web application with a context.xml, web.xml, *.jspx, *.tagx, or *.tld XML document containing an external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue. |
| CVE-2013-4322 | Medium | 2014-02-26 | No exploit published | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.50, and 8.x before 8.0.0-RC10 processes chunked transfer coding without properly handling (1) a large total amount of chunked data or (2) whitespace characters in an HTTP header value within a trailer field, which allows remote attackers to cause a denial of service by streaming data. NOTE: this vulnerability exists because of an incomplete fix for CVE-2012-3544. |
| CVE-2013-4286 | Medium | 2014-02-26 | Outside Waratek scope | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |
| CVE-2013-2067 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/authenticator/FormAuthenticator.java in the form authentication feature in Apache Tomcat 6.0.21 through 6.0.36 and 7.x before 7.0.33 does not properly handle the relationships between authentication requirements and sessions, which allows remote attackers to inject a request into a session by sending this request during completion of the login form, a variant of a session fixation attack. |