
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
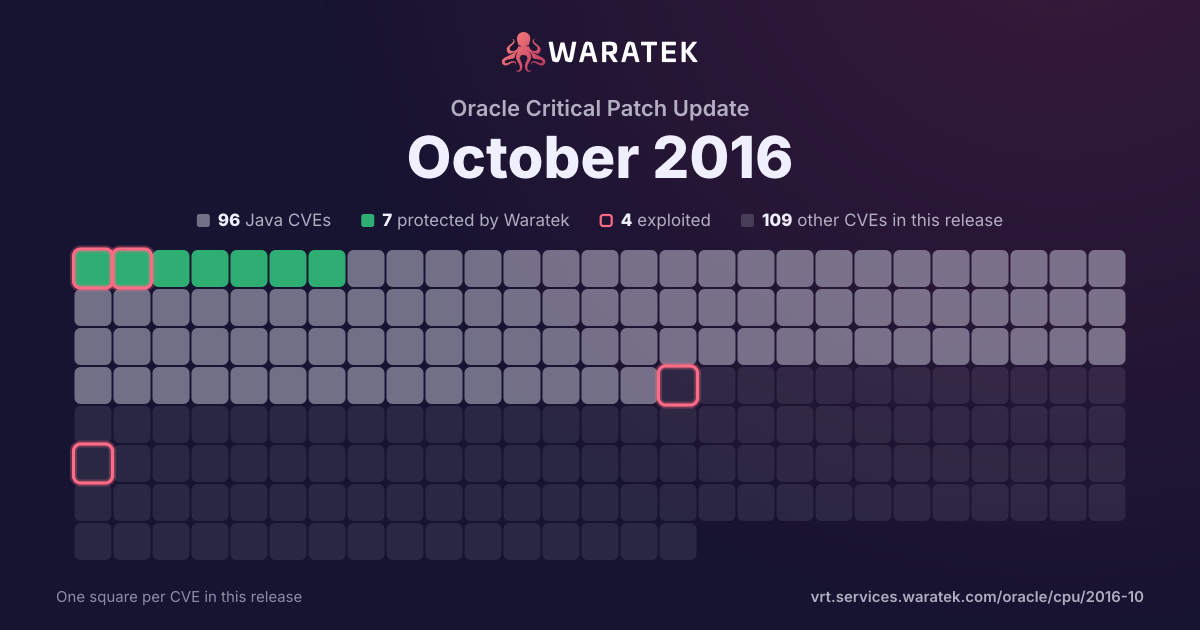
By status
7Protected by Waratek2Mitigation candidate104No exploit published15Outside Waratek scope75Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 16 matches · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
6.2%
No exploit published
15
93.8%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
16
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
6.2%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
15
93.8%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-8281 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-5536. |
| CVE-2016-5618 | Low | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.2.0.0, 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality via vectors related to Code Generation Engine. |
| CVE-2016-5602 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality via vectors related to Code Generation Engine. |
| CVE-2016-5601 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows local users to affect confidentiality and integrity via vectors related to CIE Related Components. |
| CVE-2016-5536 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-8281. |
| CVE-2016-5535 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5531 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS-WebServices. |
| CVE-2016-5519 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Java Server Faces. |
| CVE-2016-5511 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 12.2.1.0.0, 12.2.1.1.0, and 12.2.1.2.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2016-5506 | Low | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Manager component in Oracle Fusion Middleware allows local users to affect confidentiality and integrity via vectors related to App Server. |
| CVE-2016-5500 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to Viewer. |
| CVE-2016-5495 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to EUL Code & Schema. |
| CVE-2016-5488 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0 and 12.1.3.0 allows remote attackers to affect availability via vectors related to Web Container, a different vulnerability than CVE-2016-3445. |
| CVE-2016-3551 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Services component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.3.0.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JAXWS Web Services Stack. |
| CVE-2016-3505 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to JavaServer Faces. |
| CVE-2016-3473 | High | 2016-10-25 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality via unknown vectors. |