
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
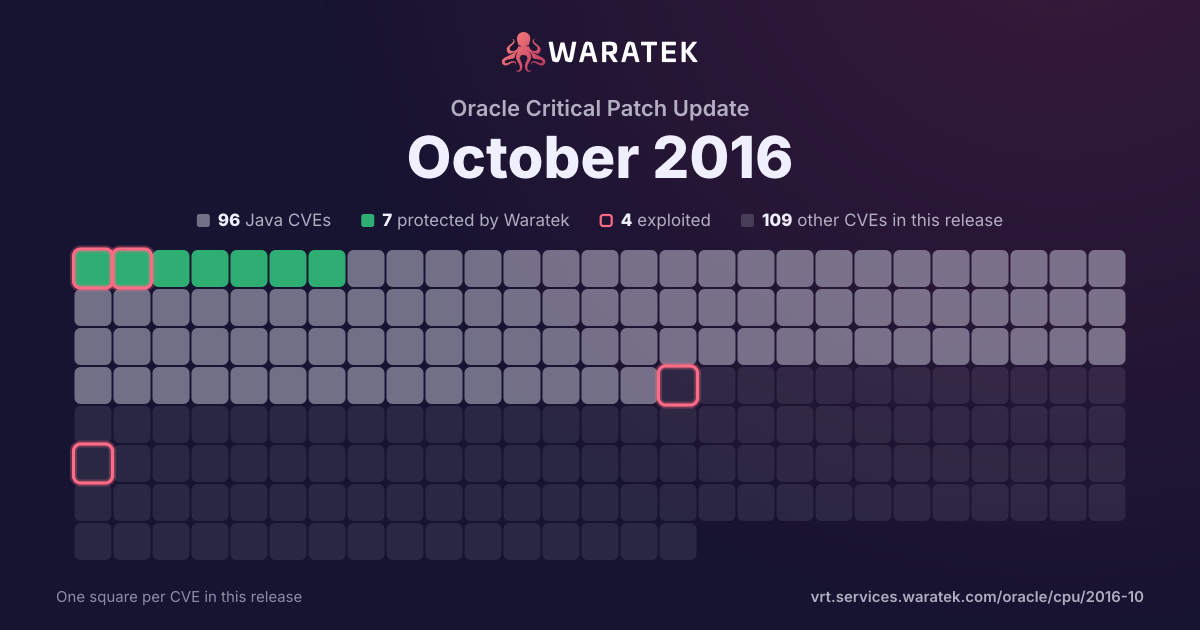
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 68 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
68matches
0in Waratek scope0.0%
0protected0.0%
1exploited1.5%
0CISA KEV0.0%
2public PoC2.9%
3EPSS ≥ 0.54.4%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
68
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
68
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
1.5%
Working exploit published
1
1.5%
Proof of concept only
0
0.0%
Forecast only
1
1.5%
No public exploit
65
95.6%
split by
peak 57 / quarter
Q4 141
Not applicable1
Medium1
not blocked1
No public exploit1
Q1 153
Not applicable3
High1
Medium2
not blocked3
No public exploit3
Q2 151
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 150
Q4 150
Q1 160
Q2 162
Not applicable2
High1
Medium1
not blocked2
Working exploit published1
No public exploit1
Q3 163
Not applicable3
Critical1
High2
not blocked3
Exploited1
Forecast only1
No public exploit1
Q4 1657
Not applicable57
Critical2
High11
Medium35
Low9
not blocked57
No public exploit57
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q4 14Q1 15Q2 15Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-1881 | High | 2017-02-15 | Not applicable | No public exploit | The kernel in FreeBSD 9.3, 10.1, and 10.2 allows local users to cause a denial of service (crash) or potentially gain privilege via a crafted Linux compatibility layer setgroups system call. |
| CVE-2016-7440 | Medium | 2016-12-13 | Not applicable | No public exploit | The C software implementation of AES Encryption and Decryption in wolfSSL (formerly CyaSSL) before 3.9.10 makes it easier for local users to discover AES keys by leveraging cache-bank timing differences. |
| CVE-2016-8290 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-5633. |
| CVE-2016-8289 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows local users to affect integrity and availability via vectors related to Server: InnoDB. |
| CVE-2016-8288 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.30 and earlier and 5.7.12 and earlier allows remote authenticated users to affect integrity via vectors related to Server: InnoDB Plugin. |
| CVE-2016-8287 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Replication. |
| CVE-2016-8286 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows remote authenticated users to affect confidentiality via vectors related to Server: Security: Privileges. |
| CVE-2016-8284 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows local users to affect availability via vectors related to Server: Replication. |
| CVE-2016-8283 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Types. |
| CVE-2016-5635 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Security: Audit. |
| CVE-2016-5634 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to RBR. |
| CVE-2016-5633 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-8290. |
| CVE-2016-5632 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-5631 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Memcached. |
| CVE-2016-5630 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5629 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Federated. |
| CVE-2016-5628 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: DML. |
| CVE-2016-5627 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5626 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to GIS. |
| CVE-2016-5625 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Packaging. |
| CVE-2016-5624 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5615 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Lynx. |
| CVE-2016-5613 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5608. |
| CVE-2016-5612 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.50 and earlier, 5.6.31 and earlier, and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5611 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality via vectors related to Core. |
| CVE-2016-5610 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core. |
| CVE-2016-5609 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5608 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5613. |
| CVE-2016-5606 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect integrity and availability via vectors related to Kernel Zones. |
| CVE-2016-5605 | Critical | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.1.4 in Oracle Virtualization allows remote attackers to affect confidentiality and integrity via vectors related to VRDE. |
| CVE-2016-5598 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Connector component 2.1.3 and earlier and 2.0.4 and earlier in Oracle MySQL allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Connector/Python. |
| CVE-2016-5588 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, and CVE-2016-5579. |
| CVE-2016-5584 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.52 and earlier, 5.6.33 and earlier, and 5.7.15 and earlier allows remote administrators to affect confidentiality via vectors related to Server: Security: Encryption. |
| CVE-2016-5580 | Critical | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Secure Global Desktop component in Oracle Virtualization 4.7 and 5.2 allows remote authenticated users to affect confidentiality and availability via vectors through Web Services. |
| CVE-2016-5579 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, and CVE-2016-5588. |
| CVE-2016-5578 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5577 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5576 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Kernel Zones. |
| CVE-2016-5574 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5577, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5566 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-5561 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect availability via vectors related to IKE. |
| CVE-2016-5559 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect integrity via vectors related to Kernel. |
| CVE-2016-5558 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5553 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect availability via unknown vectors. |
| CVE-2016-5544 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect confidentiality, integrity, and availability via vectors related to Kernel/X86. |
| CVE-2016-5538 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core, a different vulnerability than CVE-2016-5501. |
| CVE-2016-5525 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.3 allows local users to affect integrity via vectors related to Cluster check files. |
| CVE-2016-5508 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 4.3 allows local users to affect confidentiality via vectors related to Cluster Geo. |
| CVE-2016-5507 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.32 and earlier and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5503 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality, integrity, and availability via vectors related to Core Services. |
| CVE-2016-5501 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core, a different vulnerability than CVE-2016-5538. |
| CVE-2016-5492 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality and integrity via vectors related to SMB Users. |
| CVE-2016-5487 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5486 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality via vectors related to Core Services. |
| CVE-2016-5481 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows remote attackers to affect confidentiality via vectors related to Core Services. |
| CVE-2016-5480 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect integrity via vectors related to Bash. |
| CVE-2016-3495 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-3492 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-6304 | High | 2016-09-26 | Not applicable | Forecast only | Multiple memory leaks in t1_lib.c in OpenSSL before 1.0.1u, 1.0.2 before 1.0.2i, and 1.1.0 before 1.1.0a allow remote attackers to cause a denial of service (memory consumption) via large OCSP Status Request extensions. |
| CVE-2016-6662 | Critical | 2016-09-20 | Not applicable | Exploited | Oracle MySQL through 5.5.52, 5.6.x through 5.6.33, and 5.7.x through 5.7.15; MariaDB before 5.5.51, 10.0.x before 10.0.27, and 10.1.x before 10.1.17; and Percona Server before 5.5.51-38.1, 5.6.x before 5.6.32-78.0, and 5.7.x before 5.7.14-7 allow local users to create arbitrary configurations and bypass certain protection mechanisms by setting general_log_file to a my.cnf configuration. NOTE: this can be leveraged to execute arbitrary code with root privileges by setting malloc_lib. NOTE: the affected MySQL version information is from Oracle's October 2016 CPU. Oracle has not commented on third-party claims that the issue was silently patched in MySQL 5.5.52, 5.6.33, and 5.7.15. |
| CVE-2016-4979 | High | 2016-07-06 | Not applicable | No public exploit | The Apache HTTP Server 2.4.18 through 2.4.20, when mod_http2 and mod_ssl are enabled, does not properly recognize the "SSLVerifyClient require" directive for HTTP/2 request authorization, which allows remote attackers to bypass intended access restrictions by leveraging the ability to send multiple requests over a single connection and aborting a renegotiation. |
| CVE-2016-2176 | High | 2016-05-05 | Not applicable | No public exploit | The X509_NAME_oneline function in crypto/x509/x509_obj.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to obtain sensitive information from process stack memory or cause a denial of service (buffer over-read) via crafted EBCDIC ASN.1 data. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |
| CVE-2015-1351 | High | 2015-03-30 | Not applicable | No public exploit | Use-after-free vulnerability in the _zend_shared_memdup function in zend_shared_alloc.c in the OPcache extension in PHP through 5.6.7 allows remote attackers to cause a denial of service or possibly have unspecified other impact via unknown vectors. |
| CVE-2015-0286 | Medium | 2015-03-19 | Not applicable | No public exploit | The ASN1_TYPE_cmp function in crypto/asn1/a_type.c in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a does not properly perform boolean-type comparisons, which allows remote attackers to cause a denial of service (invalid read operation and application crash) via a crafted X.509 certificate to an endpoint that uses the certificate-verification feature. |
| CVE-2014-3571 | Medium | 2015-01-09 | Not applicable | No public exploit | OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via a crafted DTLS message that is processed with a different read operation for the handshake header than for the handshake body, related to the dtls1_get_record function in d1_pkt.c and the ssl3_read_n function in s3_pkt.c. |
| CVE-2014-9296 | Medium | 2014-12-20 | Not applicable | No public exploit | The receive function in ntp_proto.c in ntpd in NTP before 4.2.8 continues to execute after detecting a certain authentication error, which might allow remote attackers to trigger an unintended association change via crafted packets. |