
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
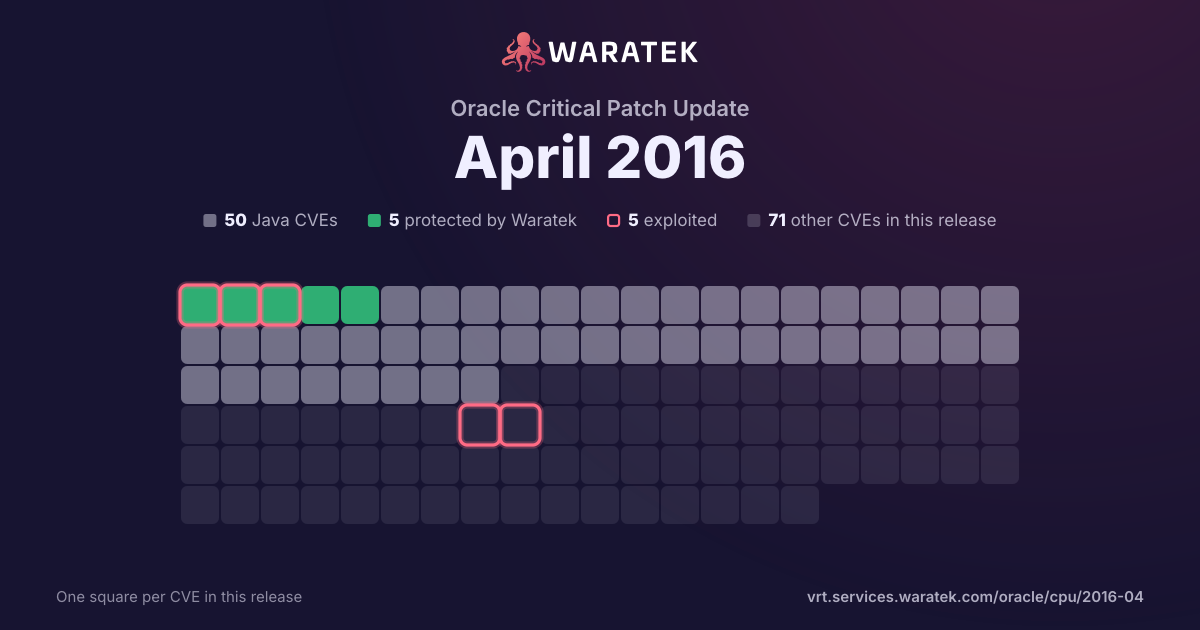
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 2 EPSS ≥ 0.5
5matches
1in Waratek scope20.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC20.0%
2EPSS ≥ 0.540.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
20.0%
Outside Waratek scope
3
60.0%
Not applicable
1
20.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
5
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
1
20.0%
No public exploit
3
60.0%
split by
peak 2 / quarter
Q4 111
No exploit published1
Medium1
not blocked1
No public exploit1
Q1 120
Q2 120
Q3 120
Q4 120
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 130
Q3 130
Q4 130
Q1 141
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q2 140
Q3 140
Q4 140
Q1 150
Q2 150
Q3 152
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
Working exploit published1
No public exploit1
Q1 12Q3 12Q1 13Q3 13Q1 14Q3 14Q1 15Q3 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-3238 | Medium | 2015-08-24 | Not applicable | No public exploit | The _unix_run_helper_binary function in the pam_unix module in Linux-PAM (aka pam) before 1.2.1, when unable to directly access passwords, allows local users to enumerate usernames or cause a denial of service (hang) via a large password. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2014-2532 | Medium | 2014-03-18 | Outside Waratek scope | No public exploit | sshd in OpenSSH before 6.6 does not properly support wildcards on AcceptEnv lines in sshd_config, which allows remote attackers to bypass intended environment restrictions by using a substring located before a wildcard character. |
| CVE-2013-2566 | Medium | 2013-03-15 | Outside Waratek scope | Forecast only | The RC4 algorithm, as used in the TLS protocol and SSL protocol, has many single-byte biases, which makes it easier for remote attackers to conduct plaintext-recovery attacks via statistical analysis of ciphertext in a large number of sessions that use the same plaintext. |
| CVE-2011-4461 | Medium | 2011-12-30 | No exploit published | No public exploit | Jetty 8.1.0.RC2 and earlier computes hash values for form parameters without restricting the ability to trigger hash collisions predictably, which allows remote attackers to cause a denial of service (CPU consumption) by sending many crafted parameters. |