
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
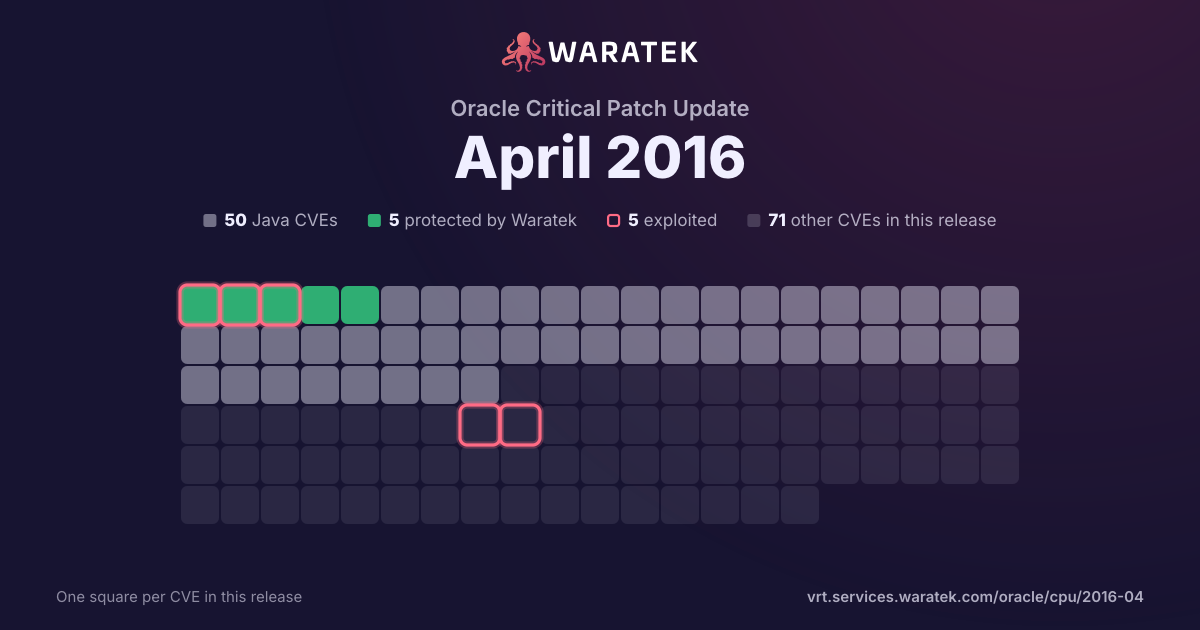
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 17 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
17matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC11.8%
2EPSS ≥ 0.511.8%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
17
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
17
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
5.9%
Proof of concept only
1
5.9%
Forecast only
0
0.0%
No public exploit
15
88.2%
split by
peak 11 / month
May 151
Outside Waratek scope1
Low1
not blocked1
Proof of concept only1
Jun 150
Jul 151
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Aug 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Sep 150
Oct 150
Nov 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Dec 151
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Jan 160
Feb 161
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Mar 160
Apr 1611
Outside Waratek scope11
Critical4
High2
Medium2
Low3
not blocked11
No public exploit11
May 15Jun 15Jul 15Aug 15Sep 15Oct 15Nov 15Dec 15Jan 16Feb 16Mar 16Apr 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3461 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the MySQL Enterprise Monitor component in Oracle MySQL 3.0.25 and earlier and 3.1.2 and earlier allows remote administrators to affect confidentiality, integrity, and availability via vectors related to Monitoring: Server. |
| CVE-2016-3454 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3449 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Deployment. |
| CVE-2016-3443 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to 2D. NOTE: the previous information is from the April 2016 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to obtain sensitive information via crafted font data, which triggers an out-of-bounds read. |
| CVE-2016-3426 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2016-3422 | Medium | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect availability via vectors related to 2D. |
| CVE-2016-0691 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect integrity via unknown vectors, a different vulnerability than CVE-2016-0690. |
| CVE-2016-0690 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect integrity via unknown vectors, a different vulnerability than CVE-2016-0691. |
| CVE-2016-0687 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to the Hotspot sub-component. |
| CVE-2016-0686 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Serialization. |
| CVE-2016-0677 | Medium | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 12.1.0.1 and 12.1.0.2 allows remote attackers to affect availability via unknown vectors. |
| CVE-2015-3197 | Medium | 2016-02-15 | Outside Waratek scope | No public exploit | ssl/s2_srvr.c in OpenSSL 1.0.1 before 1.0.1r and 1.0.2 before 1.0.2f does not prevent use of disabled ciphers, which makes it easier for man-in-the-middle attackers to defeat cryptographic protection mechanisms by performing computations on SSLv2 traffic, related to the get_client_master_key and get_client_hello functions. |
| CVE-2015-3195 | Medium | 2015-12-06 | Outside Waratek scope | No public exploit | The ASN1_TFLG_COMBINE implementation in crypto/asn1/tasn_dec.c in OpenSSL before 0.9.8zh, 1.0.0 before 1.0.0t, 1.0.1 before 1.0.1q, and 1.0.2 before 1.0.2e mishandles errors caused by malformed X509_ATTRIBUTE data, which allows remote attackers to obtain sensitive information from process memory by triggering a decoding failure in a PKCS#7 or CMS application. |
| CVE-2015-7182 | Critical | 2015-11-05 | Outside Waratek scope | No public exploit | Heap-based buffer overflow in the ASN.1 decoder in Mozilla Network Security Services (NSS) before 3.19.2.1 and 3.20.x before 3.20.1, as used in Firefox before 42.0 and Firefox ESR 38.x before 38.4 and other products, allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted OCTET STRING data. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2015-4000 | Low | 2015-05-21 | Outside Waratek scope | Proof of concept only | The TLS protocol 1.2 and earlier, when a DHE_EXPORT ciphersuite is enabled on a server but not on a client, does not properly convey a DHE_EXPORT choice, which allows man-in-the-middle attackers to conduct cipher-downgrade attacks by rewriting a ClientHello with DHE replaced by DHE_EXPORT and then rewriting a ServerHello with DHE_EXPORT replaced by DHE, aka the "Logjam" issue. |