
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
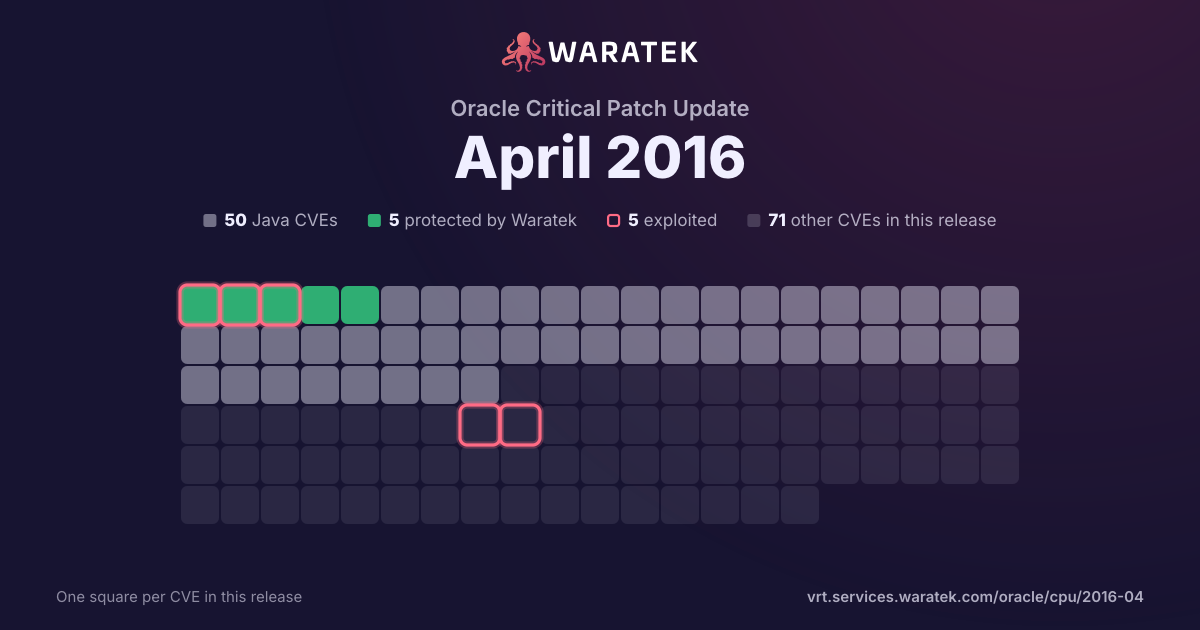
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 22 matches · 8 in Waratek scope · 0 protected · 2 exploited · 0 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
22matches
8in Waratek scope36.4%
0protected0.0%
2exploited9.1%
0CISA KEV0.0%
2public PoC9.1%
3EPSS ≥ 0.513.6%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
8
36.4%
Outside Waratek scope
2
9.1%
Not applicable
12
54.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
22
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
9.1%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
4.5%
No public exploit
19
86.4%
split by
peak 17 / quarter
Q3 131
Not applicable1
High1
not blocked1
Exploited1
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 150
Q2 151
Not applicable1
High1
not blocked1
Forecast only1
Q3 150
Q4 152
Not applicable2
High2
not blocked2
No public exploit2
Q1 161
Not applicable1
High1
not blocked1
Exploited1
Q2 1617
No exploit published8
Outside Waratek scope2
Not applicable7
High17
not blocked17
No public exploit17
Q3 13Q4 13Q1 14Q2 14Q3 14Q4 14Q1 15Q2 15Q3 15Q4 15Q1 16Q2 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3461 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the MySQL Enterprise Monitor component in Oracle MySQL 3.0.25 and earlier and 3.1.2 and earlier allows remote administrators to affect confidentiality, integrity, and availability via vectors related to Monitoring: Server. |
| CVE-2016-3456 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Complex Maintenance, Repair, and Overhaul component in Oracle Supply Chain Products Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Dialog Box. |
| CVE-2016-3455 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters. |
| CVE-2016-3449 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Deployment. |
| CVE-2016-3441 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect confidentiality, integrity, and availability via vectors related to Filesystem. |
| CVE-2016-3439 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Wireless component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Call Phone Number Page. |
| CVE-2016-3438 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Configurator component in Oracle Supply Chain Products Suite 12.0.6, 12.1, and 12.2 allows remote attackers to affect confidentiality and integrity via vectors related to JRAD Heartbeat. NOTE: the previous information is from the April 2016 CPU. Oracle has not commented on third-party claims that that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via three unspecified parameters in an unknown JSP file. |
| CVE-2016-3437 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Wireless component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Person Address Page. |
| CVE-2016-3436 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Tasks. |
| CVE-2016-3421 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Activity Guide. |
| CVE-2016-3418 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0692, and CVE-2016-0694. |
| CVE-2016-0694 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0692, and CVE-2016-3418. |
| CVE-2016-0692 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0689 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0692, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0682 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0689, CVE-2016-0692, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0681 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle OLAP component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unspecified vectors. |
| CVE-2016-0679 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect integrity and availability via vectors related to PIA Grids. |
| CVE-2015-7547 | High | 2016-02-18 | Not applicable | Exploited | Multiple stack-based buffer overflows in the (1) send_dg and (2) send_vc functions in the libresolv library in the GNU C Library (aka glibc or libc6) before 2.23 allow remote attackers to cause a denial of service (crash) or possibly execute arbitrary code via a crafted DNS response that triggers a call to the getaddrinfo function with the AF_UNSPEC or AF_INET6 address family, related to performing "dual A/AAAA DNS queries" and the libnss_dns.so.2 NSS module. |
| CVE-2015-3194 | High | 2015-12-06 | Not applicable | No public exploit | crypto/rsa/rsa_ameth.c in OpenSSL 1.0.1 before 1.0.1q and 1.0.2 before 1.0.2e allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via an RSA PSS ASN.1 signature that lacks a mask generation function parameter. |
| CVE-2015-7236 | High | 2015-10-01 | Not applicable | No public exploit | Use-after-free vulnerability in xprt_set_caller in rpcb_svc_com.c in rpcbind 0.2.1 and earlier allows remote attackers to cause a denial of service (daemon crash) via crafted packets, involving a PMAP_CALLIT code. |
| CVE-2015-1789 | High | 2015-06-12 | Not applicable | Forecast only | The X509_cmp_time function in crypto/x509/x509_vfy.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b allows remote attackers to cause a denial of service (out-of-bounds read and application crash) via a crafted length field in ASN1_TIME data, as demonstrated by an attack against a server that supports client authentication with a custom verification callback. |
| CVE-2013-4786 | High | 2013-07-08 | Not applicable | Exploited | The IPMI 2.0 specification supports RMCP+ Authenticated Key-Exchange Protocol (RAKP) authentication, which allows remote attackers to obtain password hashes and conduct offline password guessing attacks by obtaining the HMAC from a RAKP message 2 response from a BMC. |