
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
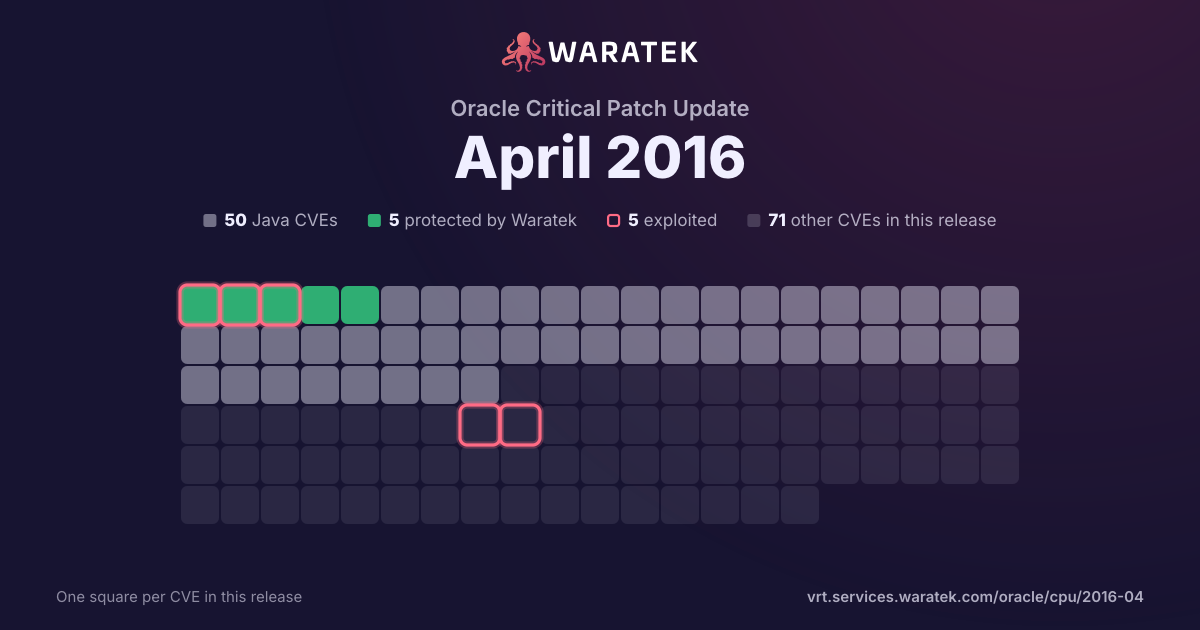
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 105 matches · 48 in Waratek scope · 4 protected · 4 exploited · 1 CISA KEV · 3 public PoC · 4 EPSS ≥ 0.5
105matches
48in Waratek scope45.7%
4protected3.8%
4exploited3.8%
1CISA KEV1.0%
3public PoC2.9%
4EPSS ≥ 0.53.8%
Protected by Waratek
4
3.8%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
44
41.9%
Outside Waratek scope
12
11.4%
Not applicable
45
42.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
3.8%
partly blocked
0
0.0%
not blocked
101
96.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
3.8%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
101
96.2%
split by
peak 101 / quarter
Q1 163
Outside Waratek scope1
Not applicable2
Critical1
High1
Medium1
not blocked3
Exploited1
No public exploit2
Q2 16101
Protected by Waratek3
No exploit published44
Outside Waratek scope11
Not applicable43
Critical10
High17
Medium66
Low8
blocked by ARMR today3
not blocked98
Exploited2
No public exploit99
Q3 160
Q4 160
Q1 170
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-0408 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 through 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to the Activity Guide sub-component. |
| CVE-2016-0407 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality via vectors related to Fusion HR Talent Integration. |
| CVE-2016-0705 | Critical | 2016-03-03 | Not applicable | No public exploit | Double free vulnerability in the dsa_priv_decode function in crypto/dsa/dsa_ameth.c in OpenSSL 1.0.1 before 1.0.1s and 1.0.2 before 1.0.2g allows remote attackers to cause a denial of service (memory corruption) or possibly have unspecified other impact via a malformed DSA private key. |
| CVE-2015-7547 | High | 2016-02-18 | Not applicable | Exploited | Multiple stack-based buffer overflows in the (1) send_dg and (2) send_vc functions in the libresolv library in the GNU C Library (aka glibc or libc6) before 2.23 allow remote attackers to cause a denial of service (crash) or possibly execute arbitrary code via a crafted DNS response that triggers a call to the getaddrinfo function with the AF_UNSPEC or AF_INET6 address family, related to performing "dual A/AAAA DNS queries" and the libnss_dns.so.2 NSS module. |
| CVE-2015-3197 | Medium | 2016-02-15 | Outside Waratek scope | No public exploit | ssl/s2_srvr.c in OpenSSL 1.0.1 before 1.0.1r and 1.0.2 before 1.0.2f does not prevent use of disabled ciphers, which makes it easier for man-in-the-middle attackers to defeat cryptographic protection mechanisms by performing computations on SSLv2 traffic, related to the get_client_master_key and get_client_hello functions. |