
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
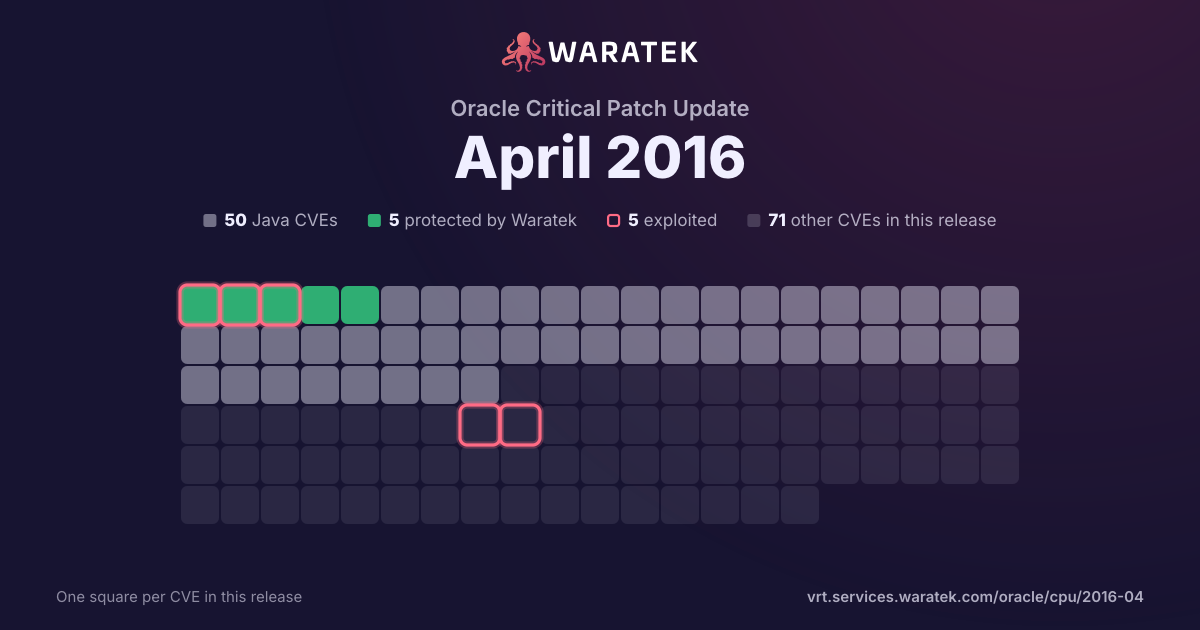
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 102 matches · 48 in Waratek scope · 4 protected · 3 exploited · 1 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
102matches
48in Waratek scope47.1%
4protected3.9%
3exploited2.9%
1CISA KEV1.0%
2public PoC2.0%
3EPSS ≥ 0.52.9%
Protected by Waratek
4
3.9%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
44
43.1%
Outside Waratek scope
11
10.8%
Not applicable
43
42.2%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
3.9%
partly blocked
0
0.0%
not blocked
98
96.1%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
2.9%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
99
97.1%
split by
peak 101 / quarter
Q2 16101
Protected by Waratek3
No exploit published44
Outside Waratek scope11
Not applicable43
Critical10
High17
Medium66
Low8
blocked by ARMR today3
not blocked98
Exploited2
No public exploit99
Q3 160
Q4 160
Q1 170
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-3466 | Critical | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Field Service component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Wireless. |
| CVE-2016-3465 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect availability via vectors related to ZFS. |
| CVE-2016-3464 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Direct Banking component in Oracle Financial Services Software 12.0.3 allows remote authenticated users to affect confidentiality via vectors related to Accounts. |
| CVE-2016-3463 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Direct Banking component in Oracle Financial Services Software 12.0.3 allows remote attackers to affect confidentiality and integrity via vectors related to Pre-Login. |
| CVE-2016-3462 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Network Configuration Service. |
| CVE-2016-3461 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the MySQL Enterprise Monitor component in Oracle MySQL 3.0.25 and earlier and 3.1.2 and earlier allows remote administrators to affect confidentiality, integrity, and availability via vectors related to Monitoring: Server. |
| CVE-2016-3460 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to ePerformance. |
| CVE-2016-3457 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM ePerformance component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to Security. |
| CVE-2016-3456 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Complex Maintenance, Repair, and Overhaul component in Oracle Supply Chain Products Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Dialog Box. |
| CVE-2016-3455 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters. |
| CVE-2016-3454 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3449 | High | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Deployment. |
| CVE-2016-3447 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to OAF Core. |
| CVE-2016-3443 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to 2D. NOTE: the previous information is from the April 2016 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to obtain sensitive information via crafted font data, which triggers an out-of-bounds read. |
| CVE-2016-3442 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to Portal. |
| CVE-2016-3441 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect confidentiality, integrity, and availability via vectors related to Filesystem. |
| CVE-2016-3439 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Wireless component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Call Phone Number Page. |
| CVE-2016-3438 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Configurator component in Oracle Supply Chain Products Suite 12.0.6, 12.1, and 12.2 allows remote attackers to affect confidentiality and integrity via vectors related to JRAD Heartbeat. NOTE: the previous information is from the April 2016 CPU. Oracle has not commented on third-party claims that that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via three unspecified parameters in an unknown JSP file. |
| CVE-2016-3437 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Wireless component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Person Address Page. |
| CVE-2016-3436 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Tasks. |
| CVE-2016-3435 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect availability via vectors related to PIA Core Technology. |
| CVE-2016-3434 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect integrity via vectors related to Logout. |
| CVE-2016-3431 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.1.1, 9.3.1.2, 9.3.2, and 9.3.3 allows remote authenticated users to affect confidentiality and integrity via vectors related to Security, a different vulnerability than CVE-2016-3420. |
| CVE-2016-3429 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Xstore Point of Service component in Oracle Retail Applications 5.0, 5.5, 6.0, 6.5, 7.0, and 7.1 allows remote authenticated users to affect confidentiality and integrity via vectors related to Xstore Services. |
| CVE-2016-3428 | Low | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect availability via vectors related to Engineering Communication Interface. |
| CVE-2016-3427 | Critical | 2016-04-21 | Protected by Waratek | Exploited | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77; Java SE Embedded 8u77; and JRockit R28.3.9 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JMX. |
| CVE-2016-3426 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2016-3425 | Medium | 2016-04-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77; Java SE Embedded 8u77; and JRockit R28.3.9 allows remote attackers to affect availability via vectors related to JAXP. |
| CVE-2016-3423 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to Rich Text Editor, a different vulnerability than CVE-2016-0698. |
| CVE-2016-3422 | Medium | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect availability via vectors related to 2D. |
| CVE-2016-3421 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Activity Guide. |
| CVE-2016-3420 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.1.1, 9.3.1.2, 9.3.2, and 9.3.3 allows remote authenticated users to affect confidentiality and integrity via vectors related to Security, a different vulnerability than CVE-2016-3431. |
| CVE-2016-3419 | Low | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect availability via vectors related to Filesystem. |
| CVE-2016-3418 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0692, and CVE-2016-0694. |
| CVE-2016-3417 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to PIA Search Functionality. |
| CVE-2016-3416 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, 12.1.3, and 12.2.1 allows remote attackers to affect confidentiality and integrity via vectors related to Console. |
| CVE-2016-0700 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Console, a different vulnerability than CVE-2016-0675. |
| CVE-2016-0699 | Critical | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Direct Banking component in Oracle Financial Services Software 12.0.2 and 12.0.3 allows remote attackers to affect confidentiality and integrity via vectors related to the Login sub-component. |
| CVE-2016-0698 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to Rich Text Editor, a different vulnerability than CVE-2016-3423. |
| CVE-2016-0697 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-0696 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6 allows remote attackers to affect confidentiality and integrity via vectors related to Console. |
| CVE-2016-0695 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77; Java SE Embedded 8u77; and JRockit R28.3.9 allows remote attackers to affect confidentiality via vectors related to Security. |
| CVE-2016-0694 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0692, and CVE-2016-3418. |
| CVE-2016-0693 | Critical | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to the PAM LDAP module. |
| CVE-2016-0692 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0689, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0691 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect integrity via unknown vectors, a different vulnerability than CVE-2016-0690. |
| CVE-2016-0690 | Low | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect integrity via unknown vectors, a different vulnerability than CVE-2016-0691. |
| CVE-2016-0689 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0682, CVE-2016-0692, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0688 | Low | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, and 12.1.3 allows remote attackers to affect integrity via vectors related to Core Components. |
| CVE-2016-0687 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to the Hotspot sub-component. |
| CVE-2016-0686 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Serialization. |
| CVE-2016-0685 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to File Processing. |
| CVE-2016-0684 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail MICROS ARS POS component in Oracle Retail Applications 1.5 allows remote authenticated users to affect confidentiality via vectors related to POS. |
| CVE-2016-0683 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to Search Framework. |
| CVE-2016-0682 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the DataStore component in Oracle Berkeley DB 11.2.5.0.32, 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, 12.1.6.0.35, and 12.1.6.1.26 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0689, CVE-2016-0692, CVE-2016-0694, and CVE-2016-3418. |
| CVE-2016-0681 | High | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle OLAP component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unspecified vectors. |
| CVE-2016-0680 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to Services Procurement. |
| CVE-2016-0679 | High | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote authenticated users to affect integrity and availability via vectors related to PIA Grids. |
| CVE-2016-0678 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 5.0.18 allows local users to affect confidentiality, integrity, and availability via vectors related to Core. |
| CVE-2016-0677 | Medium | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 12.1.0.1 and 12.1.0.2 allows remote attackers to affect availability via unknown vectors. |
| CVE-2016-0676 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect availability via vectors related to the kernel. |
| CVE-2016-0675 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Console, a different vulnerability than CVE-2016-0700. |
| CVE-2016-0674 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Common Components component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows local users to affect confidentiality and integrity via vectors related to Email. |
| CVE-2016-0673 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to UIF Open UI. |
| CVE-2016-0672 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Direct Banking component in Oracle Financial Services Software 12.0.2 and 12.0.3 allows remote attackers to affect confidentiality and integrity via vectors related to Pre-Login. |
| CVE-2016-0671 | Low | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 12.1.2.0 allows remote attackers to affect confidentiality via vectors related to OSSL Module. |
| CVE-2016-0669 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect integrity and availability via vectors related to Fwflash. |
| CVE-2016-0668 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.28 and earlier and 5.7.10 and earlier and MariaDB 10.0.x before 10.0.24 and 10.1.x before 10.1.12 allows local users to affect availability via vectors related to InnoDB. |
| CVE-2016-0667 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows local users to affect availability via vectors related to Locking. |
| CVE-2016-0666 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows local users to affect availability via vectors related to Security: Privileges. |
| CVE-2016-0665 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.28 and earlier and 5.7.10 and earlier allows local users to affect availability via vectors related to Security: Encryption. |
| CVE-2016-0663 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to Performance Schema. |
| CVE-2016-0662 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows local users to affect availability via vectors related to Partition. |
| CVE-2016-0661 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.28 and earlier and 5.7.10 and earlier allows local users to affect availability via vectors related to Options. |
| CVE-2016-0659 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows local users to affect availability via vectors related to Optimizer. |
| CVE-2016-0658 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to Optimizer. |
| CVE-2016-0657 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.11 and earlier allows local users to affect confidentiality via vectors related to JSON. |
| CVE-2016-0656 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to InnoDB, a different vulnerability than CVE-2016-0654. |
| CVE-2016-0655 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.29 and earlier and 5.7.11 and earlier and MariaDB 10.0.x before 10.0.25 and 10.1.x before 10.1.14 allows local users to affect availability via vectors related to InnoDB. |
| CVE-2016-0654 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to InnoDB, a different vulnerability than CVE-2016-0656. |
| CVE-2016-0653 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to FTS. |
| CVE-2016-0652 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.10 and earlier allows local users to affect availability via vectors related to DML. |
| CVE-2016-0651 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.46 and earlier allows local users to affect availability via vectors related to Optimizer. |
| CVE-2016-0650 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect availability via vectors related to Replication. |
| CVE-2016-0649 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect availability via vectors related to PS. |
| CVE-2016-0648 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows local users to affect availability via vectors related to PS. |
| CVE-2016-0647 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows local users to affect availability via vectors related to FTS. |
| CVE-2016-0646 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect availability via vectors related to DML. |
| CVE-2016-0644 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect availability via vectors related to DDL. |
| CVE-2016-0643 | Low | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows local users to affect confidentiality via vectors related to DML. |
| CVE-2016-0642 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier allows local users to affect integrity and availability via vectors related to Federated. |
| CVE-2016-0641 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect confidentiality and availability via vectors related to MyISAM. |
| CVE-2016-0640 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.47 and earlier, 5.6.28 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.48, 10.0.x before 10.0.24, and 10.1.x before 10.1.12 allows local users to affect integrity and availability via vectors related to DML. |
| CVE-2016-0639 | Critical | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.29 and earlier and 5.7.11 and earlier allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Pluggable Authentication. |
| CVE-2016-0638 | Critical | 2016-04-21 | Protected by Waratek | Exploited | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, 12.1.3, and 12.2.1 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Java Messaging Service. |
| CVE-2016-0623 | Medium | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect integrity via vectors related to the Automated Installer sub-component. |
| CVE-2016-0479 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality and integrity via vectors related to Analytics Scorecard. |
| CVE-2016-0469 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail MICROS C2 component in Oracle Retail Applications 9.89.0.0 allows local users to affect confidentiality via vectors related to POS. |
| CVE-2016-0468 | Medium | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to Analytics Web General. |