
Oracle Critical Patch Update April 2016
Released April 2016 · Oracle's advisory ↗ · ← Critical Patch Update, January 2016 · Critical Patch Update, July 2016 →
121 CVEs in this release, one square each
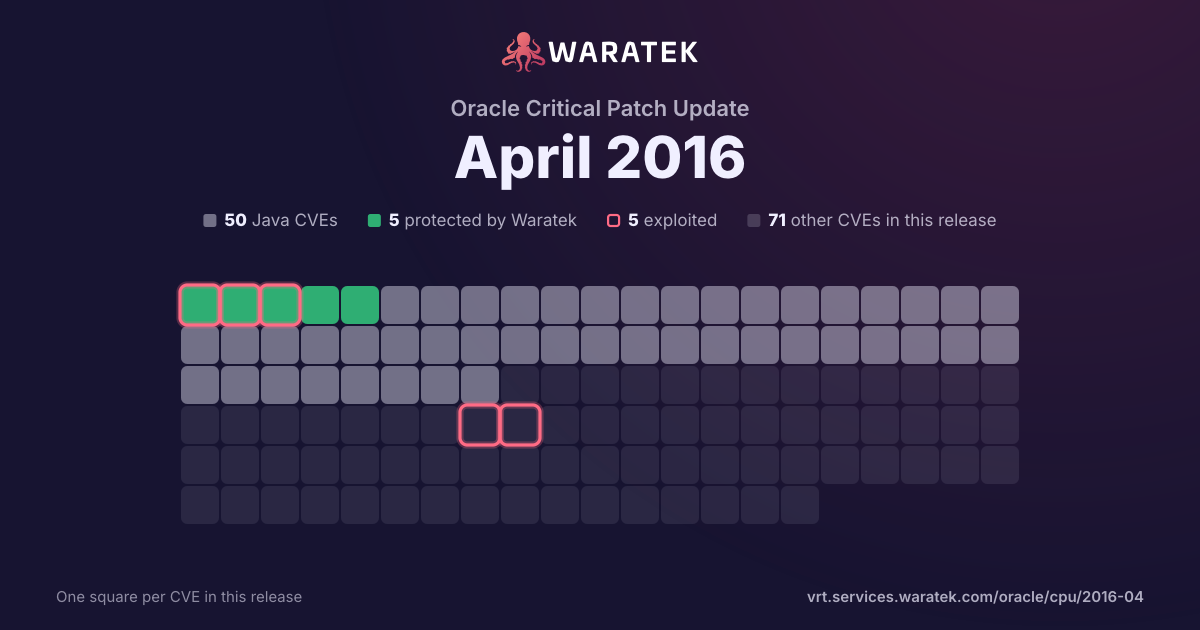
By status
5Protected by Waratek45No exploit published20Outside Waratek scope51Not applicable
5Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 14 matches · 5 in Waratek scope · 3 protected · 3 exploited · 1 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
14matches
5in Waratek scope35.7%
3protected21.4%
3exploited21.4%
1CISA KEV7.1%
2public PoC14.3%
3EPSS ≥ 0.521.4%
Protected by Waratek
3
21.4%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
14.3%
Outside Waratek scope
6
42.9%
Not applicable
3
21.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
21.4%
partly blocked
0
0.0%
not blocked
11
78.6%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
21.4%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
11
78.6%
split by
peak 10 / quarter
Q3 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q1 161
Not applicable1
Critical1
not blocked1
No public exploit1
Q2 1610
Protected by Waratek2
No exploit published2
Outside Waratek scope4
Not applicable2
Critical10
blocked by ARMR today2
not blocked8
Exploited2
No public exploit8
Q3 160
Q4 160
Q1 170
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-3466 | Critical | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Field Service component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Wireless. |
| CVE-2016-3454 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3443 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to 2D. NOTE: the previous information is from the April 2016 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to obtain sensitive information via crafted font data, which triggers an out-of-bounds read. |
| CVE-2016-3427 | Critical | 2016-04-21 | Protected by Waratek | Exploited | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77; Java SE Embedded 8u77; and JRockit R28.3.9 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JMX. |
| CVE-2016-0699 | Critical | 2016-04-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Direct Banking component in Oracle Financial Services Software 12.0.2 and 12.0.3 allows remote attackers to affect confidentiality and integrity via vectors related to the Login sub-component. |
| CVE-2016-0693 | Critical | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to the PAM LDAP module. |
| CVE-2016-0687 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to the Hotspot sub-component. |
| CVE-2016-0686 | Critical | 2016-04-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u113, 7u99, and 8u77 and Java SE Embedded 8u77 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Serialization. |
| CVE-2016-0639 | Critical | 2016-04-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.29 and earlier and 5.7.11 and earlier allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Pluggable Authentication. |
| CVE-2016-0638 | Critical | 2016-04-21 | Protected by Waratek | Exploited | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, 12.1.3, and 12.2.1 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Java Messaging Service. |
| CVE-2016-0705 | Critical | 2016-03-03 | Not applicable | No public exploit | Double free vulnerability in the dsa_priv_decode function in crypto/dsa/dsa_ameth.c in OpenSSL 1.0.1 before 1.0.1s and 1.0.2 before 1.0.2g allows remote attackers to cause a denial of service (memory corruption) or possibly have unspecified other impact via a malformed DSA private key. |
| CVE-2015-7182 | Critical | 2015-11-05 | Outside Waratek scope | No public exploit | Heap-based buffer overflow in the ASN.1 decoder in Mozilla Network Security Services (NSS) before 3.19.2.1 and 3.20.x before 3.20.1, as used in Firefox before 42.0 and Firefox ESR 38.x before 38.4 and other products, allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted OCTET STRING data. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |