
Oracle Critical Patch Update January 2016
Released January 2016 · Oracle's advisory ↗ · ← Critical Patch Update, October 2015 · Critical Patch Update, April 2016 →
237 CVEs in this release, one square each
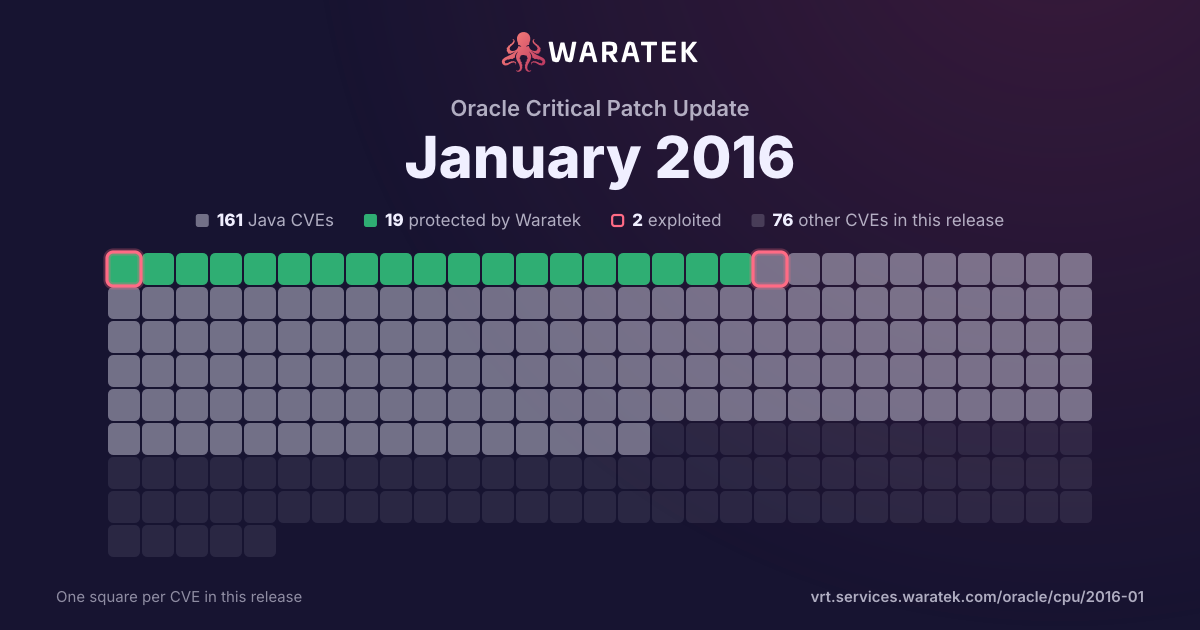
By status
19Protected by Waratek3Mitigation candidate139No exploit published14Outside Waratek scope62Not applicable
2Exploited, marked by the ring
No exploit published. For 137 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 13 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
13matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
13
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
13
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
7.7%
Forecast only
0
0.0%
No public exploit
12
92.3%
split by
peak 9 / quarter
Q4 13Q1 14Q2 14Q3 14Q4 14Q1 15Q2 15Q3 15Q4 15Q1 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-6015 | High | 2016-01-22 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-4808, CVE-2015-6013, CVE-2015-6014, and CVE-2016-0432. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this issue is a stack-based buffer overflow in Oracle Outside In 8.5.2 and earlier, which allows remote attackers to execute arbitrary code via a crafted Paradox DB file. |
| CVE-2015-6014 | High | 2016-01-22 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-4808, CVE-2015-6013, CVE-2015-6015, and CVE-2016-0432. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this issue is a stack-based buffer overflow in Oracle Outside In 8.5.2 and earlier, which allows remote attackers to execute arbitrary code via a crafted DOC file. |
| CVE-2015-6013 | High | 2016-01-22 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-4808, CVE-2015-6014, CVE-2015-6015, and CVE-2016-0432. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this issue is a stack-based buffer overflow in Oracle Outside In 8.5.2 and earlier, which allows remote attackers to execute arbitrary code via a crafted WK4 file. |
| CVE-2016-0546 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.46 and earlier, 5.6.27 and earlier, and 5.7.9 and MariaDB before 5.5.47, 10.0.x before 10.0.23, and 10.1.x before 10.1.10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Client. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that these are multiple buffer overflows in the mysqlshow tool that allow remote database servers to have unspecified impact via a long table or database name. |
| CVE-2016-0452 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle GoldenGate component in Oracle GoldenGate 11.2 and 12.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0451. |
| CVE-2016-0451 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle GoldenGate component in Oracle GoldenGate 11.2 and 12.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0452. |
| CVE-2016-0440 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect availability via vectors related to NFSv4. |
| CVE-2016-0414 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Solaris Kernel Zones, a different vulnerability than CVE-2016-0418. |
| CVE-2016-0403 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect availability via vectors related to SMB Utilities. |
| CVE-2015-8370 | High | 2015-12-16 | Not applicable | Proof of concept only | Multiple integer underflows in Grub2 1.98 through 2.02 allow physically proximate attackers to bypass authentication, obtain sensitive information, or cause a denial of service (disk corruption) via backspace characters in the (1) grub_username_get function in grub-core/normal/auth.c or the (2) grub_password_get function in lib/crypto.c, which trigger an "Off-by-two" or "Out of bounds overwrite" memory error. |
| CVE-2015-8126 | High | 2015-11-13 | Not applicable | No public exploit | Multiple buffer overflows in the (1) png_set_PLTE and (2) png_get_PLTE functions in libpng before 1.0.64, 1.1.x and 1.2.x before 1.2.54, 1.3.x and 1.4.x before 1.4.17, 1.5.x before 1.5.24, and 1.6.x before 1.6.19 allow remote attackers to cause a denial of service (application crash) or possibly have unspecified other impact via a small bit-depth value in an IHDR (aka image header) chunk in a PNG image. |
| CVE-2015-7183 | High | 2015-11-05 | Not applicable | No public exploit | Integer overflow in the PL_ARENA_ALLOCATE implementation in Netscape Portable Runtime (NSPR) in Mozilla Network Security Services (NSS) before 3.19.2.1 and 3.20.x before 3.20.1, as used in Firefox before 42.0 and Firefox ESR 38.x before 38.4 and other products, allows remote attackers to execute arbitrary code or cause a denial of service (memory corruption and application crash) via unspecified vectors. |
| CVE-2013-1741 | High | 2013-11-18 | Not applicable | No public exploit | Integer overflow in Mozilla Network Security Services (NSS) 3.15 before 3.15.3 allows remote attackers to cause a denial of service or possibly have unspecified other impact via a large size value. |