
Oracle Critical Patch Update January 2016
Released January 2016 · Oracle's advisory ↗ · ← Critical Patch Update, October 2015 · Critical Patch Update, April 2016 →
237 CVEs in this release, one square each
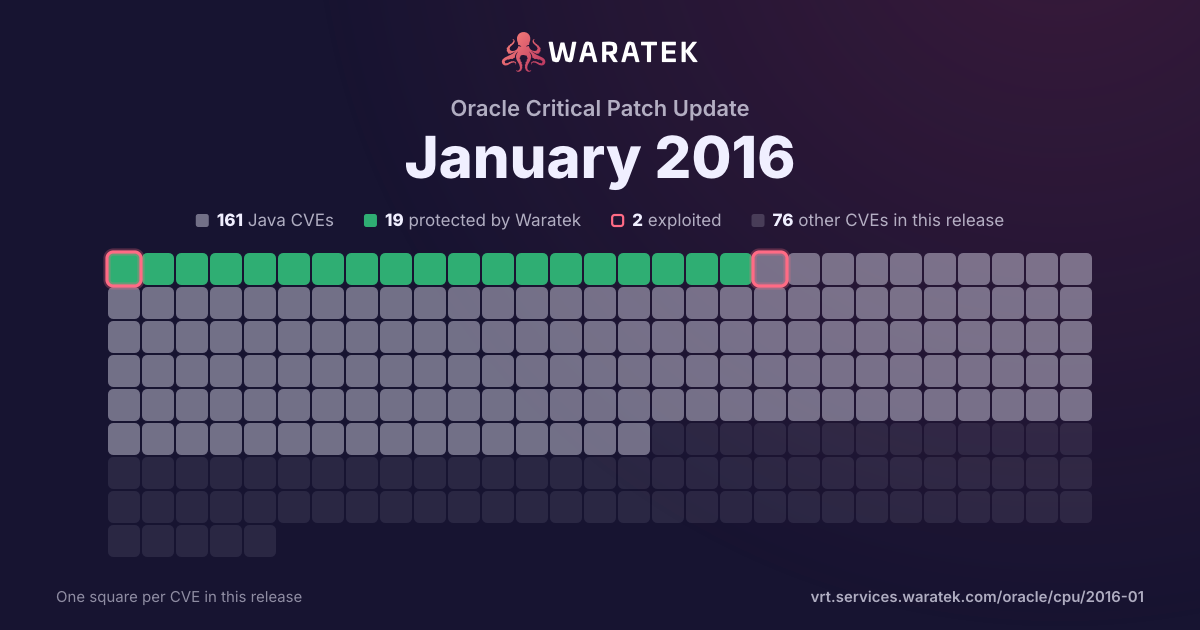
By status
19Protected by Waratek3Mitigation candidate139No exploit published14Outside Waratek scope62Not applicable
2Exploited, marked by the ring
No exploit published. For 137 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 220 matches · 158 in Waratek scope · 17 protected · 2 exploited · 0 CISA KEV · 2 public PoC · 5 EPSS ≥ 0.5
220matches
158in Waratek scope71.8%
17protected7.7%
2exploited0.9%
0CISA KEV0.0%
2public PoC0.9%
5EPSS ≥ 0.52.3%
Protected by Waratek
17
7.7%
Rule in development
0
0.0%
Mitigation candidate
2
0.9%
No exploit published
139
63.2%
Outside Waratek scope
10
4.5%
Not applicable
52
23.6%
Withdrawn CVE
0
0.0%
blocked by ARMR today
17
7.7%
partly blocked
0
0.0%
not blocked
202
91.8%
not established
1
0.5%
unrecorded
0
0.0%
Exploited
2
0.9%
Working exploit published
2
0.9%
Proof of concept only
0
0.0%
Forecast only
3
1.4%
No public exploit
213
96.8%
split by
peak 220 / month
Jan 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-0412 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM eProcurement component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect integrity via unknown vectors related to Manage Requisition Status. |
| CVE-2016-0411 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1 and 11.2.0.4 allows local users to affect confidentiality, integrity, and availability via vectors related to Agent Next Gen. |
| CVE-2016-0409 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Global Payroll Switzerland component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality via vectors related to Security. |
| CVE-2016-0406 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect integrity and availability via vectors related to Libc. |
| CVE-2016-0405 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4 allows local users to affect confidentiality via vectors related to Cluster Manageability and Serviceability. |
| CVE-2016-0404 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Federation component in Oracle Fusion Middleware 11.1.2.2 allows remote attackers to affect integrity via vectors related to Admin. |
| CVE-2016-0403 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect availability via vectors related to SMB Utilities. |
| CVE-2016-0402 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE and Java SE Embedded components in Oracle Java SE 6u105, 7u91, and 8u66 and Java SE Embedded 8u65 allows remote attackers to affect integrity via unknown vectors related to Networking. |
| CVE-2016-0401 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle BI Publisher component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect integrity via unknown vectors related to Scheduler, a different vulnerability than CVE-2016-0429. |
| CVE-2015-4926 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.1, and 12.2 allows remote attackers to affect integrity via vectors related to UIX. |
| CVE-2015-4925 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Workspace Manager component in Oracle Database Server 11.2.0.4 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-4924 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.1.1, 9.3.1.2, 9.3.2, and 9.3.3 allows remote authenticated users to affect integrity via vectors related to Security. |
| CVE-2015-4923 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XML Developer's Kit for C component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2015-4922 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via vectors related to Boot. |
| CVE-2015-4921 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2015-4920 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect integrity via vectors related to NDMP Backup Service. |
| CVE-2015-4919 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Monitoring and Diagnostics SEC. |
| CVE-2015-4885 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 12.1.0.4 allows remote attackers to affect confidentiality via vectors related to Agent Next Gen. |
| CVE-2015-4808 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via vectors related to Outside In Filters, a different vulnerability than CVE-2015-6013, CVE-2015-6014, CVE-2015-6015, and CVE-2016-0432. |
| CVE-2015-7575 | Medium | 2016-01-09 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.20.2, as used in Mozilla Firefox before 43.0.2 and Firefox ESR 38.x before 38.5.2, does not reject MD5 signatures in Server Key Exchange messages in TLS 1.2 Handshake Protocol traffic, which makes it easier for man-in-the-middle attackers to spoof servers by triggering a collision. |