
Oracle Critical Patch Update January 2016
Released January 2016 · Oracle's advisory ↗ · ← Critical Patch Update, October 2015 · Critical Patch Update, April 2016 →
237 CVEs in this release, one square each
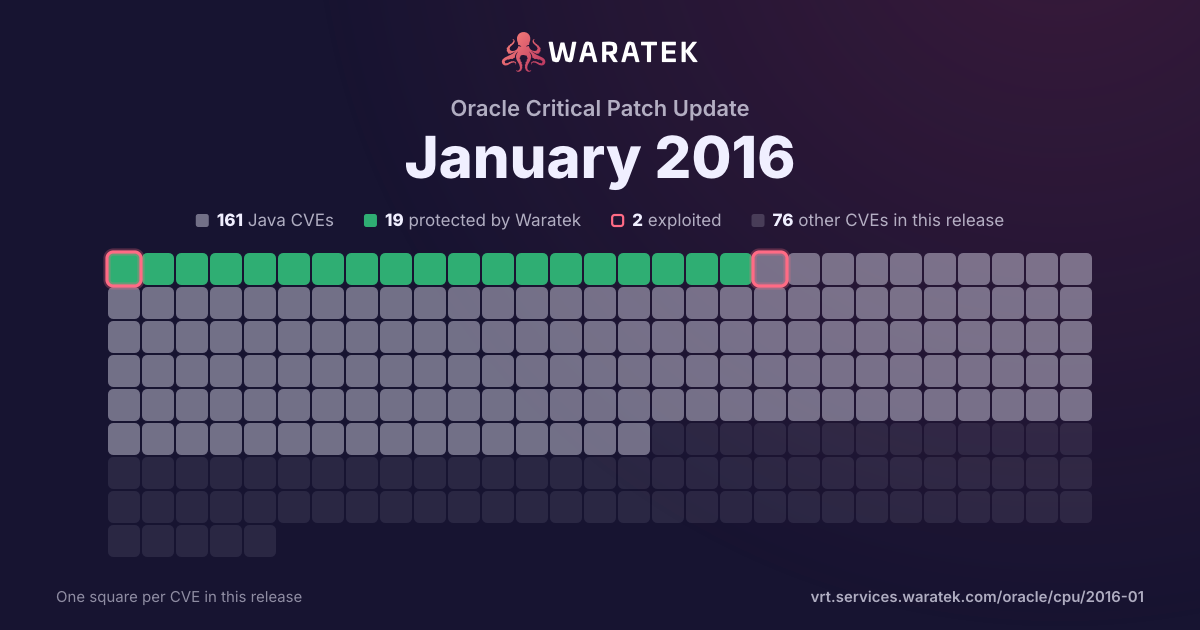
By status
19Protected by Waratek3Mitigation candidate139No exploit published14Outside Waratek scope62Not applicable
2Exploited, marked by the ring
No exploit published. For 137 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 223 matches · 152 in Waratek scope · 13 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
223matches
152in Waratek scope68.2%
13protected5.8%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
13
5.8%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
139
62.3%
Outside Waratek scope
11
4.9%
Not applicable
60
26.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
13
5.8%
partly blocked
0
0.0%
not blocked
210
94.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
223
100.0%
split by
peak 213 / quarter
Q4 131
Not applicable1
High1
not blocked1
No public exploit1
Q1 140
Q2 141
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q3 140
Q4 141
Not applicable1
Medium1
not blocked1
No public exploit1
Q1 151
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 151
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 150
Q4 155
Outside Waratek scope1
Not applicable4
Critical1
High2
Medium2
not blocked5
No public exploit5
Q1 16213
Protected by Waratek12
No exploit published139
Outside Waratek scope10
Not applicable52
High22
Medium156
Low35
blocked by ARMR today12
not blocked201
No public exploit213
Q4 13Q1 14Q2 14Q3 14Q4 14Q1 15Q2 15Q3 15Q4 15Q1 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-0514 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality and integrity via vectors related to BIS Common Components, a different vulnerability than CVE-2016-0515. |
| CVE-2016-0513 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect integrity via vectors related to BIS Common Components. |
| CVE-2016-0512 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Human Resources component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Self Service - Common Modules. |
| CVE-2016-0511 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle E-Business Intelligence component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Common Components, a different vulnerability than CVE-2016-0547, CVE-2016-0548, and CVE-2016-0549. |
| CVE-2016-0510 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle E-Business Intelligence component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Business Views Catalog. |
| CVE-2016-0509 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Internet Expenses component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect integrity via unknown vectors related to AP Web Utilities. |
| CVE-2016-0508 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iLearning component in Oracle iLearning 6.0 and 6.1 allows remote attackers to affect integrity via unknown vectors related to Learner Administration. |
| CVE-2016-0507 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iReceivables component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect integrity via unknown vectors related to AR Web Utilities, a different vulnerability than CVE-2016-0519. |
| CVE-2016-0506 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Order Management System Cloud Service component in Oracle Retail Applications 3.5, 4.5, 4.7, 5.0, and 15.0 allows remote attackers to affect confidentiality via unknown vectors related to Order Entry. |
| CVE-2016-0505 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.46 and earlier, 5.6.27 and earlier, and 5.7.9 and MariaDB before 5.5.47, 10.0.x before 10.0.23, and 10.1.x before 10.1.10 allows remote authenticated users to affect availability via unknown vectors related to Options. |
| CVE-2016-0504 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.27 and earlier and 5.7.9 allows remote authenticated users to affect availability via vectors related to DML, a different vulnerability than CVE-2016-0503. |
| CVE-2016-0503 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.27 and earlier and 5.7.9 allows remote authenticated users to affect availability via vectors related to DML, a different vulnerability than CVE-2016-0504. |
| CVE-2016-0502 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.31 and earlier and 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2016-0501 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop component in Oracle Virtualization 5.2 allows remote attackers to affect availability via vectors related to SGD Core. |
| CVE-2016-0500 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Order Broker Cloud Service component in Oracle Retail Applications 4.0 and 4.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to System Administration. |
| CVE-2016-0499 | High | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-4794. |
| CVE-2016-0498 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.2.2, 6.1.3.0, and 6.2.0.0 allows local users to affect confidentiality via unknown vectors related to Install. |
| CVE-2016-0497 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.2.2, 6.1.3.0, and 6.2.0.0 allows remote attackers to affect integrity via unknown vectors related to Web Client. |
| CVE-2016-0496 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the MICROS CWDirect component in Oracle Retail Applications 12.5, 13.0, 14.0, 15.0, 16.0, 17.0, and 18.0 allows remote attackers to affect confidentiality via unknown vectors related to Order Entry. |
| CVE-2016-0495 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 4.3.36 and 5.0.14 allows remote attackers to affect availability via unknown vectors related to Core. |
| CVE-2016-0494 | High | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE and Java SE Embedded components in Oracle Java SE 6u105, 7u91, and 8u66 and Java SE Embedded 8u65 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2016-0493 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect integrity and availability via unknown vectors related to Kernel Cryptography. |
| CVE-2016-0490 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0487. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the UploadServlet servlet, which allows remote attackers to upload and execute arbitrary files via directory traversal sequences in a filename header. |
| CVE-2016-0486 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0480, CVE-2016-0481, CVE-2016-0482, and CVE-2016-0485. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the exportFileName parameter. |
| CVE-2016-0485 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0480, CVE-2016-0481, CVE-2016-0482, and CVE-2016-0486. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the reportName parameter. |
| CVE-2016-0484 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the scriptPath parameter. |
| CVE-2016-0483 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 6u105, 7u91, and 8u66; Java SE Embedded 8u65; and JRockit R28.3.8 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to AWT. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a heap-based buffer overflow in the readImage function, which allows remote attackers to execute arbitrary code via crafted image data. |
| CVE-2016-0482 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0480, CVE-2016-0481, CVE-2016-0485, and CVE-2016-0486. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the file parameter. |
| CVE-2016-0481 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0480, CVE-2016-0482, CVE-2016-0485, and CVE-2016-0486. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the scheduleReportName parameter. |
| CVE-2016-0480 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Test Manager for Web Apps, a different vulnerability than CVE-2016-0481, CVE-2016-0482, CVE-2016-0485, and CVE-2016-0486. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the TMAPReportImage parameter. |
| CVE-2016-0478 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Load Testing for Web Apps, a different vulnerability than CVE-2016-0476 and CVE-2016-0477. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the scriptName parameter. |
| CVE-2016-0477 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Load Testing for Web Apps, a different vulnerability than CVE-2016-0476 and CVE-2016-0478. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the (1) repository, (2) workspace, or (3) scenario parameter. |
| CVE-2016-0476 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Application Testing Suite component in Oracle Enterprise Manager Grid Control 12.4.0.2 and 12.5.0.2 allows remote attackers to affect confidentiality via unknown vectors related to Load Testing for Web Apps, a different vulnerability than CVE-2016-0477 and CVE-2016-0478. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this is a directory traversal vulnerability in the DownloadServlet servlet, which allows remote attackers to read arbitrary files via directory traversal sequences in the reportName parameter. |
| CVE-2016-0475 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Java SE, Java SE Embedded, and JRockit components in Oracle Java SE 8u66; Java SE Embedded 8u65; and JRockit R28.3.8 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Libraries. |
| CVE-2016-0474 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect integrity via vectors related to PIA Core Technology. |
| CVE-2016-0473 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect integrity via unknown vectors related to Fluid Core. |
| CVE-2016-0472 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XDB - XML Database component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality and availability via unknown vectors. |
| CVE-2016-0471 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote attackers to affect confidentiality via unknown vectors related to Multichannel Framework. |
| CVE-2016-0470 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle BI Publisher component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to BI Publisher Security. |
| CVE-2016-0467 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Security component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2016-0466 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Java SE, Java SE Embedded, and JRockit components in Oracle Java SE 6u105, 7u91, and 8u66; Java SE Embedded 8u65; and JRockit R28.3.8 allows remote attackers to affect availability via vectors related to JAXP. |
| CVE-2016-0465 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4 allows local users to affect availability via unknown vectors related to Resource Group Manager. |
| CVE-2016-0464 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6, 12.1.2, and 12.1.3 allows remote attackers to affect integrity via vectors related to WLS-Console. |
| CVE-2016-0463 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53, 8.54, and 8.55 allows remote attackers to affect confidentiality via unknown vectors related to Portal. |
| CVE-2016-0462 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote authenticated users to affect confidentiality via unknown vectors related to Multichannel Framework, a different vulnerability than CVE-2015-2650. |
| CVE-2016-0461 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XDB - XML Database component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2016-0460 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.55 allows remote attackers to affect integrity via unknown vectors related to Fluid Homepage and NavBar. |
| CVE-2016-0459 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote authenticated users to affect integrity via unknown vectors related to Popup Windows. |
| CVE-2016-0458 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via vectors related to Kernel DAX. |
| CVE-2016-0456 | Medium | 2016-01-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Application Mgmt Pack for E-Business Suite component in Oracle E-Business Suite 12.1 and 12.2 allows remote attackers to affect confidentiality via vectors related to REST Framework, a different vulnerability than CVE-2016-0457. NOTE: the previous information is from the January 2016 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to read arbitrary files, cause a denial of service, conduct server-side request forgery (SSRF) attacks, or conduct SMB Relay attacks via a crafted DTD in an XML request to OA_HTML/copxmllcmservicecontroller.js. |
| CVE-2016-0455 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality and availability via unknown vectors related to Agent Next Gen. |
| CVE-2016-0454 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Mobile Application Servlet component in Oracle E-Business Suite 12.1 and 12.2 allows local users to affect confidentiality via vectors related to MWA Server Manager. |
| CVE-2016-0453 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.1.2 allows remote attackers to affect integrity via unknown vectors related to Embedded Server. |
| CVE-2016-0452 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle GoldenGate component in Oracle GoldenGate 11.2 and 12.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0451. |
| CVE-2016-0451 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle GoldenGate component in Oracle GoldenGate 11.2 and 12.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-0452. |
| CVE-2016-0450 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle GoldenGate component in Oracle GoldenGate 11.2 and 12.1.2 allows remote attackers to affect availability via unknown vectors. |
| CVE-2016-0449 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Agent Next Gen, a different vulnerability than CVE-2016-0444 and CVE-2016-0447. |
| CVE-2016-0448 | Medium | 2016-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE and Java SE Embedded components in Oracle Java SE 6u105, 7u91, and 8u66, and Java SE Embedded 8u65 allows remote authenticated users to affect confidentiality via vectors related to JMX. |
| CVE-2016-0447 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Agent Next Gen, a different vulnerability than CVE-2016-0444 and CVE-2016-0449. |
| CVE-2016-0446 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality via unknown vectors related to Agent Next Gen. |
| CVE-2016-0445 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Agent Next Gen. |
| CVE-2016-0444 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Agent Next Gen, a different vulnerability than CVE-2016-0447 and CVE-2016-0449. |
| CVE-2016-0443 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 12.1.0.4, and 12.1.0.5 allows remote attackers to affect confidentiality via unknown vectors related to Agent Next Gen. |
| CVE-2016-0442 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 12.1.0.4 and 12.1.0.5 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Loader Service. |
| CVE-2016-0441 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.1.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Embedded Server. |
| CVE-2016-0440 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect availability via vectors related to NFSv4. |
| CVE-2016-0439 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Web Cache component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect confidentiality via vectors related to SSL support, a different vulnerability than CVE-2016-0430. |
| CVE-2016-0438 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Point-of-Service component in Oracle Retail Applications 13.4, 14.0, and 14.1 allows local users to affect confidentiality via vectors related to Mobile POS, a different vulnerability than CVE-2016-0434, CVE-2016-0436, and CVE-2016-0437. |
| CVE-2016-0437 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Point-of-Service component in Oracle Retail Applications 13.4, 14.0, and 14.1 allows local users to affect confidentiality via vectors related to Mobile POS, a different vulnerability than CVE-2016-0434, CVE-2016-0436, and CVE-2016-0438. |
| CVE-2016-0436 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Point-of-Service component in Oracle Retail Applications 13.4, 14.0, and 14.1 allows local users to affect confidentiality via vectors related to Mobile POS, a different vulnerability than CVE-2016-0434, CVE-2016-0437, and CVE-2016-0438. |
| CVE-2016-0435 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Point-of-Service component in Oracle Retail Applications 13.4, 14.0, and 14.1 allows local users to affect confidentiality and integrity via vectors related to Mobile POS. |
| CVE-2016-0434 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Point-of-Service component in Oracle Retail Applications 13.4, 14.0, and 14.1 allows local users to affect confidentiality via vectors related to Mobile POS, a different vulnerability than CVE-2016-0436, CVE-2016-0437, and CVE-2016-0438. |
| CVE-2016-0433 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Web Cache component in Oracle Fusion Middleware 11.1.1.9.0 allows remote attackers to affect confidentiality via vectors related to SSL support. |
| CVE-2016-0432 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-4808, CVE-2015-6013, CVE-2015-6014, and CVE-2015-6015. |
| CVE-2016-0431 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via unknown vectors related to Solaris Kernel Zones, a different vulnerability than CVE-2016-0419. |
| CVE-2016-0430 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Web Cache component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect confidentiality via vectors related to SSL support, a different vulnerability than CVE-2016-0439. |
| CVE-2016-0429 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle BI Publisher component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.9.0 allows remote attackers to affect integrity via unknown vectors related to Scheduler, a different vulnerability than CVE-2016-0401. |
| CVE-2016-0428 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via unknown vectors related to Verified Boot. |
| CVE-2016-0427 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 11.2.0.4, 12.1.0.4, and 12.1.0.5 allows remote authenticated users to affect confidentiality via unknown vectors related to UI Framework. |
| CVE-2016-0426 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect confidentiality and availability via unknown vectors related to Solaris Kernel Zones. |
| CVE-2016-0425 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Monitoring and Diagnostics. |
| CVE-2016-0424 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect availability via vectors related to Enterprise Infrastructure SEC, a different vulnerability than CVE-2016-0422. |
| CVE-2016-0423 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Enterprise Infrastructure SEC. |
| CVE-2016-0422 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect availability via vectors related to Enterprise Infrastructure SEC, a different vulnerability than CVE-2016-0424. |
| CVE-2016-0421 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect availability via vectors related to Monitoring and Diagnostics SEC. |
| CVE-2016-0420 | High | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1 and 9.2 allows remote attackers to affect availability via unknown vectors related to Monitoring and Diagnostics. |
| CVE-2016-0419 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via unknown vectors related to Solaris Kernel Zones, a different vulnerability than CVE-2016-0431. |
| CVE-2016-0418 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Solaris Kernel Zones, a different vulnerability than CVE-2016-0414. |
| CVE-2016-0417 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.2 allows local users to affect confidentiality, integrity, and availability via vectors related to HA for MySQL. |
| CVE-2016-0416 | Medium | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect integrity via unknown vectors related to System Archive Utility. |
| CVE-2016-0415 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1, 12.1.0.4, and 12.1.0.5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to UI Framework. |
| CVE-2016-0414 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Solaris Kernel Zones, a different vulnerability than CVE-2016-0418. |
| CVE-2016-0413 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Federation component in Oracle Fusion Middleware 11.1.1.7 allows remote authenticated users to affect integrity via vectors related to Federation protocol support. |
| CVE-2016-0412 | Low | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM eProcurement component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect integrity via unknown vectors related to Manage Requisition Status. |
| CVE-2016-0411 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 11.1.0.1 and 11.2.0.4 allows local users to affect confidentiality, integrity, and availability via vectors related to Agent Next Gen. |
| CVE-2016-0409 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Global Payroll Switzerland component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality via vectors related to Security. |
| CVE-2016-0406 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect integrity and availability via vectors related to Libc. |
| CVE-2016-0405 | Low | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4 allows local users to affect confidentiality via vectors related to Cluster Manageability and Serviceability. |
| CVE-2016-0404 | Medium | 2016-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Federation component in Oracle Fusion Middleware 11.1.2.2 allows remote attackers to affect integrity via vectors related to Admin. |
| CVE-2016-0403 | High | 2016-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows remote attackers to affect availability via vectors related to SMB Utilities. |