
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
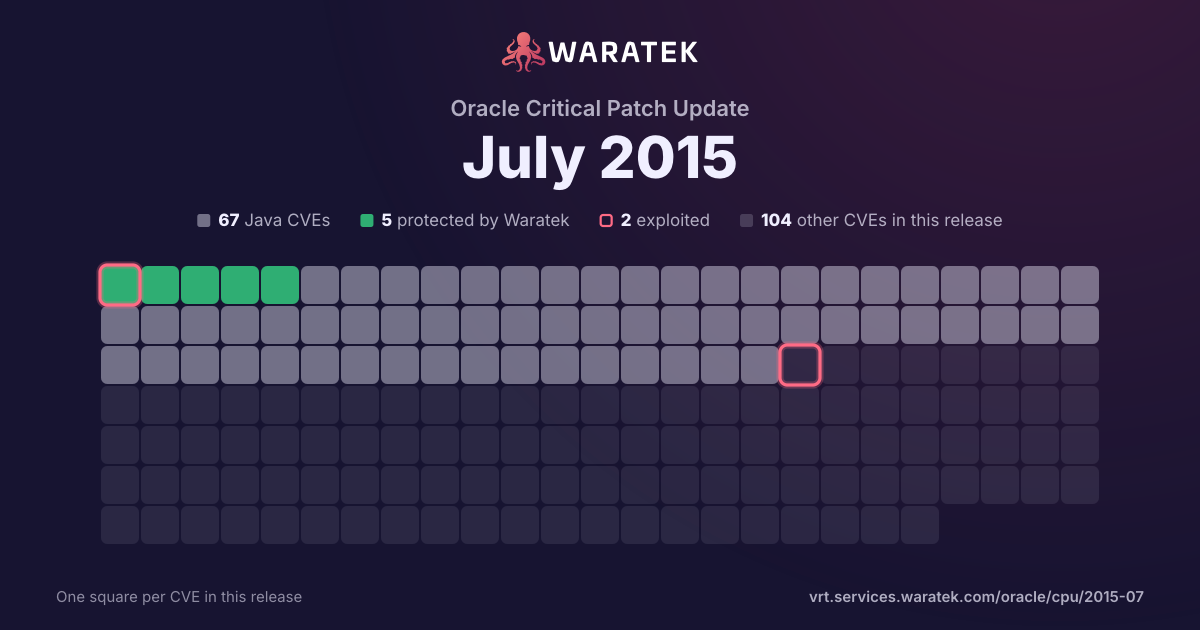
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 18 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
18matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
18
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
18
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
18
100.0%
split by
peak 16 / month
Dec 14Jan 15Feb 15Mar 15Apr 15May 15Jun 15Jul 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4755 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 12.1.0.2 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2015-4740 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Partitioning component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-4729 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Deployment. |
| CVE-2015-2664 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2015-2655 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 4.2.3.00.08 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2015-2637 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JavaFX 2.2.80; and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via unknown vectors related to 2D. |
| CVE-2015-2632 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45 allows remote attackers to affect confidentiality via unknown vectors related to 2D. |
| CVE-2015-2621 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33, allows remote attackers to affect confidentiality via vectors related to JMX. |
| CVE-2015-2620 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.43 and earlier and 5.6.23 and earlier allows remote authenticated users to affect confidentiality via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-2619 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45, JavaFX 2.2.80, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via unknown vectors related to 2D. |
| CVE-2015-2613 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2015-2599 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Scheduler component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2015-2596 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 allows remote attackers to affect integrity via unknown vectors related to Hotspot. |
| CVE-2015-2595 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle OLAP component in Oracle Database Server 12.1.0.1 and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-2586 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 4.2.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2015-0468 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-0227 | Medium | 2015-02-16 | Outside Waratek scope | No public exploit | java/org/apache/coyote/http11/filters/ChunkedInputFilter.java in Apache Tomcat 6.x before 6.0.42, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle attempts to continue reading data after an error has occurred, which allows remote attackers to conduct HTTP request smuggling attacks or cause a denial of service (resource consumption) by streaming data with malformed chunked transfer coding. |
| CVE-2014-7809 | Medium | 2014-12-10 | Outside Waratek scope | No public exploit | Apache Struts 2.0.0 through 2.3.x before 2.3.20 uses predictable <s:token/> values, which allows remote attackers to bypass the CSRF protection mechanism. |