
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
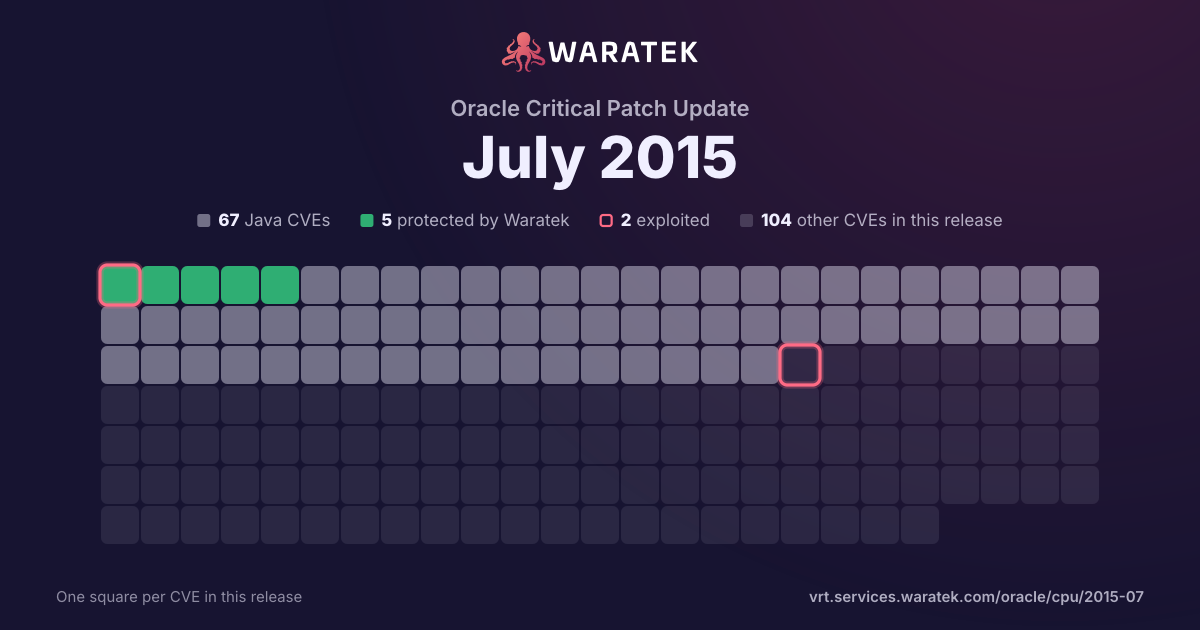
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
10matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC10.0%
1EPSS ≥ 0.510.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
10
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
10
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
10.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
90.0%
split by
peak 9 / month
Jan 15Feb 15Mar 15Apr 15May 15Jun 15Jul 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4760 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2015-4736 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2015-4733 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to RMI. |
| CVE-2015-4732 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2015-2590. |
| CVE-2015-4731 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; Java SE Embedded 7u75; and Java SE Embedded 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JMX. |
| CVE-2015-2638 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JavaFX 2.2.80; and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2015-2629 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-0457. |
| CVE-2015-2628 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to CORBA. |
| CVE-2015-2597 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Install. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |