
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
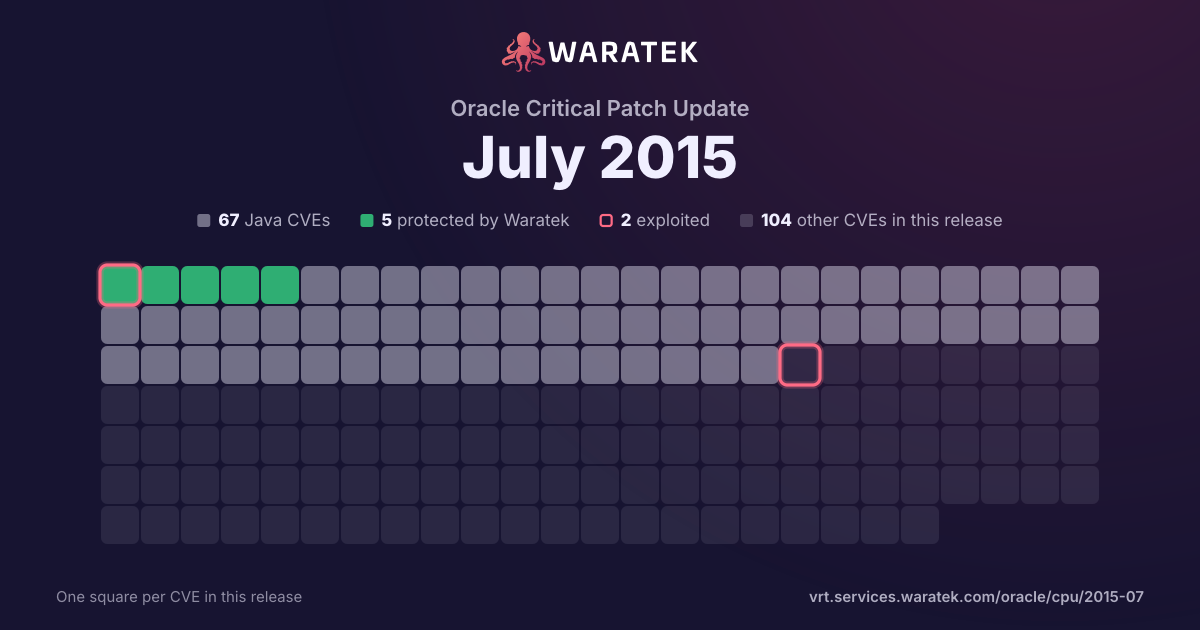
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 32 matches · 12 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
32matches
12in Waratek scope37.5%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC3.1%
1EPSS ≥ 0.53.1%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
12
37.5%
Outside Waratek scope
5
15.6%
Not applicable
15
46.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
32
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
3.1%
Forecast only
0
0.0%
No public exploit
31
96.9%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4788 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Data Store component in Oracle Berkeley DB 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, and 12.1.6.0.35 allows local users to affect integrity and availability via unknown vectors, a different vulnerability than CVE-2015-4774 and CVE-2015-4779. |
| CVE-2015-4779 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Data Store component in Oracle Berkeley DB 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, and 12.1.6.0.35 allows local users to affect integrity and availability via unknown vectors, a different vulnerability than CVE-2015-4774 and CVE-2015-4788. |
| CVE-2015-4774 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Data Store component in Oracle Berkeley DB 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, and 12.1.6.0.35 allows local users to affect integrity and availability via unknown vectors, a different vulnerability than CVE-2015-4779 and CVE-2015-4788. |
| CVE-2015-4771 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via vectors related to RBR. |
| CVE-2015-4769 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Security : Firewall, a different vulnerability than CVE-2015-4767. |
| CVE-2015-4767 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Security : Firewall, a different vulnerability than CVE-2015-4769. |
| CVE-2015-4765 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via vectors related to OAM Dashboard. |
| CVE-2015-4763 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Security. |
| CVE-2015-4761 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Memcached. |
| CVE-2015-4757 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.42 and earlier and 5.6.23 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Optimizer. |
| CVE-2015-4753 | Low | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Support Tools component in Oracle Database Server 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality via unknown vectors. |
| CVE-2015-4744 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2; and the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect integrity via unknown vectors related to Java Server Faces. |
| CVE-2015-4741 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Dialog popup. |
| CVE-2015-4739 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2 allows remote authenticated users to affect integrity via unknown vectors related to Help screens. |
| CVE-2015-4737 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.43 and earlier, and 5.6.23 and earlier, allows remote authenticated users to affect confidentiality via unknown vectors related to Server : Pluggable Auth. |
| CVE-2015-2662 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect availability via vectors related to DHCP Server. |
| CVE-2015-2661 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows local users to affect availability via unknown vectors related to Client. |
| CVE-2015-2660 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 allows remote authenticated users to affect confidentiality and integrity via vectors related to Oracle Agile PLM Framework. |
| CVE-2015-2651 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.2 allows local users to affect availability via vectors related to Kernel Zones virtualized NIC driver. |
| CVE-2015-2649 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1, 8.22, and 15.0 allows remote authenticated users to affect confidentiality via vectors related to UIF Open UI. |
| CVE-2015-2645 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2015-2641 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-2639 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect integrity via unknown vectors related to Server : Security : Firewall. |
| CVE-2015-2627 | Low | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45 allows remote attackers to affect confidentiality via unknown vectors related to installation. |
| CVE-2015-2625 | Low | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JRockit R28.3.6; and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via vectors related to JSSE. |
| CVE-2015-2618 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Input validation. |
| CVE-2015-2600 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Svcs component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-2598 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the mobile app in Oracle Business Intelligence Enterprise Edition in Oracle Fusion Middleware before 11.1.1.7.0 (11.6.39) allows remote authenticated users to affect integrity via unknown vectors related to Mobile - iPad. |
| CVE-2015-2592 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2015-2584. |
| CVE-2015-2585 | Low | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 5.0 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2015-2580 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect availability via vectors related to NFSv4. |
| CVE-2015-4000 | Low | 2015-05-21 | Outside Waratek scope | Proof of concept only | The TLS protocol 1.2 and earlier, when a DHE_EXPORT ciphersuite is enabled on a server but not on a client, does not properly convey a DHE_EXPORT choice, which allows man-in-the-middle attackers to conduct cipher-downgrade attacks by rewriting a ClientHello with DHE replaced by DHE_EXPORT and then rewriting a ServerHello with DHE_EXPORT replaced by DHE, aka the "Logjam" issue. |