
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
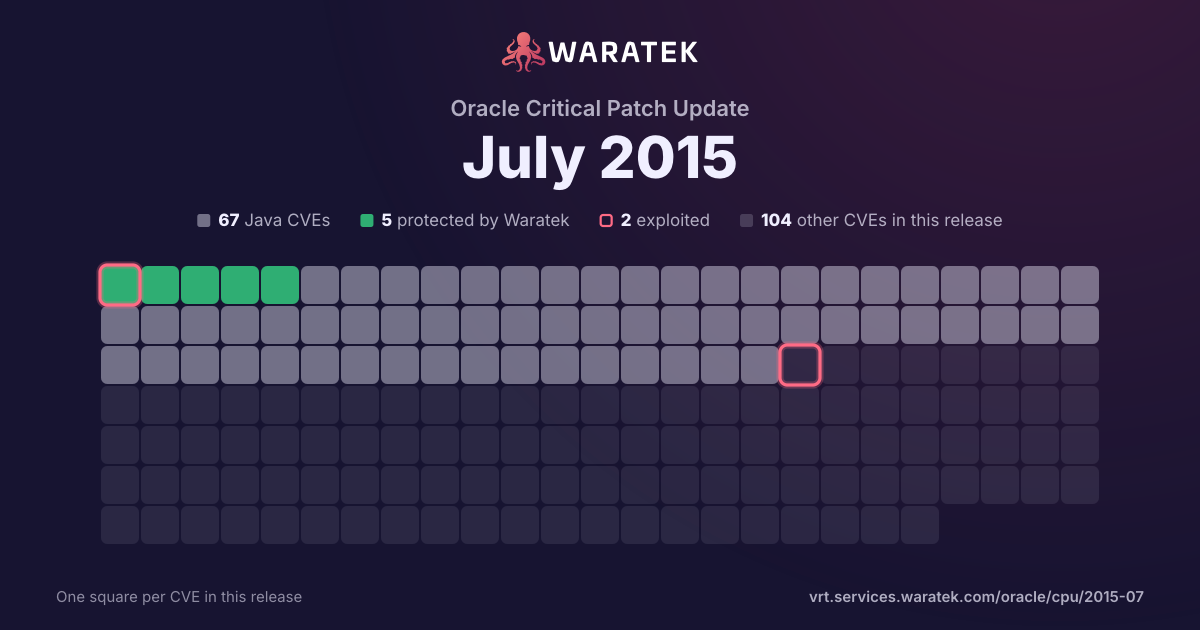
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 2 EPSS ≥ 0.5
6matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC16.7%
2EPSS ≥ 0.533.3%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
16.7%
Not applicable
5
83.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
16.7%
Forecast only
1
16.7%
No public exploit
4
66.7%
split by
peak 2 / quarter
Q4 101
Not applicable1
Low1
not blocked1
No public exploit1
Q1 110
Q2 110
Q3 110
Q4 110
Q1 120
Q2 121
Not applicable1
High1
not blocked1
No public exploit1
Q3 120
Q4 120
Q1 130
Q2 130
Q3 130
Q4 130
Q1 140
Q2 141
Not applicable1
Medium1
not blocked1
Forecast only1
Q3 141
Not applicable1
High1
not blocked1
No public exploit1
Q4 142
Outside Waratek scope1
Not applicable1
High1
Low1
not blocked2
Proof of concept only1
No public exploit1
Q4 10Q2 11Q4 11Q2 12Q4 12Q2 13Q4 13Q2 14Q4 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |
| CVE-2014-3566 | Low | 2014-10-15 | Outside Waratek scope | Proof of concept only | The SSL protocol 3.0, as used in OpenSSL through 1.0.1i and other products, uses nondeterministic CBC padding, which makes it easier for man-in-the-middle attackers to obtain cleartext data via a padding-oracle attack, aka the "POODLE" issue. |
| CVE-2014-1568 | High | 2014-09-25 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.16.2.1, 3.16.x before 3.16.5, and 3.17.x before 3.17.1, as used in Mozilla Firefox before 32.0.3, Mozilla Firefox ESR 24.x before 24.8.1 and 31.x before 31.1.1, Mozilla Thunderbird before 24.8.1 and 31.x before 31.1.2, Mozilla SeaMonkey before 2.29.1, Google Chrome before 37.0.2062.124 on Windows and OS X, and Google Chrome OS before 37.0.2062.120, does not properly parse ASN.1 values in X.509 certificates, which makes it easier for remote attackers to spoof RSA signatures via a crafted certificate, aka a "signature malleability" issue. |
| CVE-2013-5704 | Medium | 2014-04-15 | Not applicable | Forecast only | The mod_headers module in the Apache HTTP Server 2.2.22 allows remote attackers to bypass "RequestHeader unset" directives by placing a header in the trailer portion of data sent with chunked transfer coding. NOTE: the vendor states "this is not a security issue in httpd as such." |
| CVE-2012-0036 | High | 2012-04-13 | Not applicable | No public exploit | curl and libcurl 7.2x before 7.24.0 do not properly consider special characters during extraction of a pathname from a URL, which allows remote attackers to conduct data-injection attacks via a crafted URL, as demonstrated by a CRLF injection attack on the (1) IMAP, (2) POP3, or (3) SMTP protocol. |
| CVE-2010-1324 | Low | 2010-12-02 | Not applicable | No public exploit | MIT Kerberos 5 (aka krb5) 1.7.x and 1.8.x through 1.8.3 does not properly determine the acceptability of checksums, which might allow remote attackers to forge GSS tokens, gain privileges, or have unspecified other impact via (1) an unkeyed checksum, (2) an unkeyed PAC checksum, or (3) a KrbFastArmoredReq checksum based on an RC4 key. |