
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
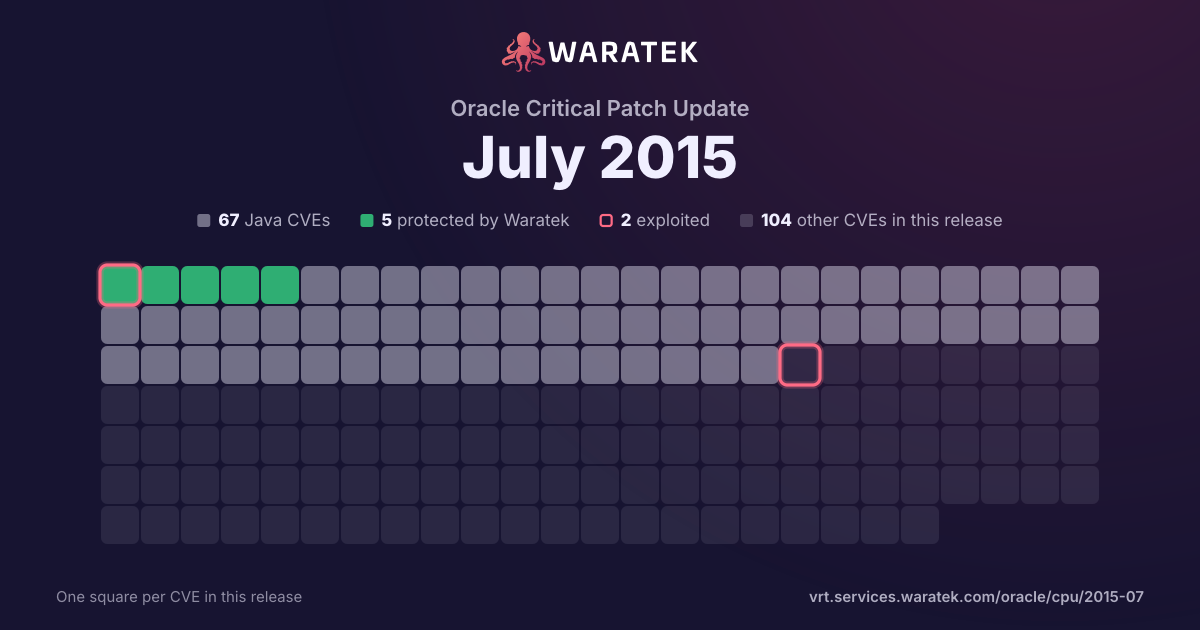
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 2 in Waratek scope · 2 protected · 1 exploited · 1 CISA KEV · 2 EPSS ≥ 0.5
Protected by Waratek
2
66.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
33.3%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
66.7%
partly blocked
0
0.0%
not blocked
1
33.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
33.3%
Working exploit published
0
0.0%
Proof of concept only
2
66.7%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Jul 131
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Aug 130
Sep 130
Oct 131
Protected by Waratek1
High1
blocked by ARMR today1
Proof of concept only1
Nov 130
Dec 130
Jan 140
Feb 140
Mar 140
Apr 140
May 140
Jun 140
Jul 140
Aug 140
Sep 140
Oct 141
Outside Waratek scope1
Low1
not blocked1
Proof of concept only1
Aug 13Oct 13Dec 13Feb 14Apr 14Jun 14Aug 14Oct 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-3566 | Low | 2014-10-15 | Outside Waratek scope | Proof of concept only | The SSL protocol 3.0, as used in OpenSSL through 1.0.1i and other products, uses nondeterministic CBC padding, which makes it easier for man-in-the-middle attackers to obtain cleartext data via a padding-oracle attack, aka the "POODLE" issue. |
| CVE-2013-2186 | High | 2013-10-28 | Protected by Waratek | Proof of concept only | The DiskFileItem class in Apache Commons FileUpload, as used in Red Hat JBoss BRMS 5.3.1; JBoss Portal 4.3 CP07, 5.2.2, and 6.0.0; and Red Hat JBoss Web Server 1.0.2 allows remote attackers to write to arbitrary files via a NULL byte in a file name in a serialized instance. |
| CVE-2013-2251 | Critical | 2013-07-20 | Protected by Waratek | Exploited | Apache Struts 2.0.0 through 2.3.15 allows remote attackers to execute arbitrary OGNL expressions via a parameter with a crafted (1) action:, (2) redirect:, or (3) redirectAction: prefix. |