
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
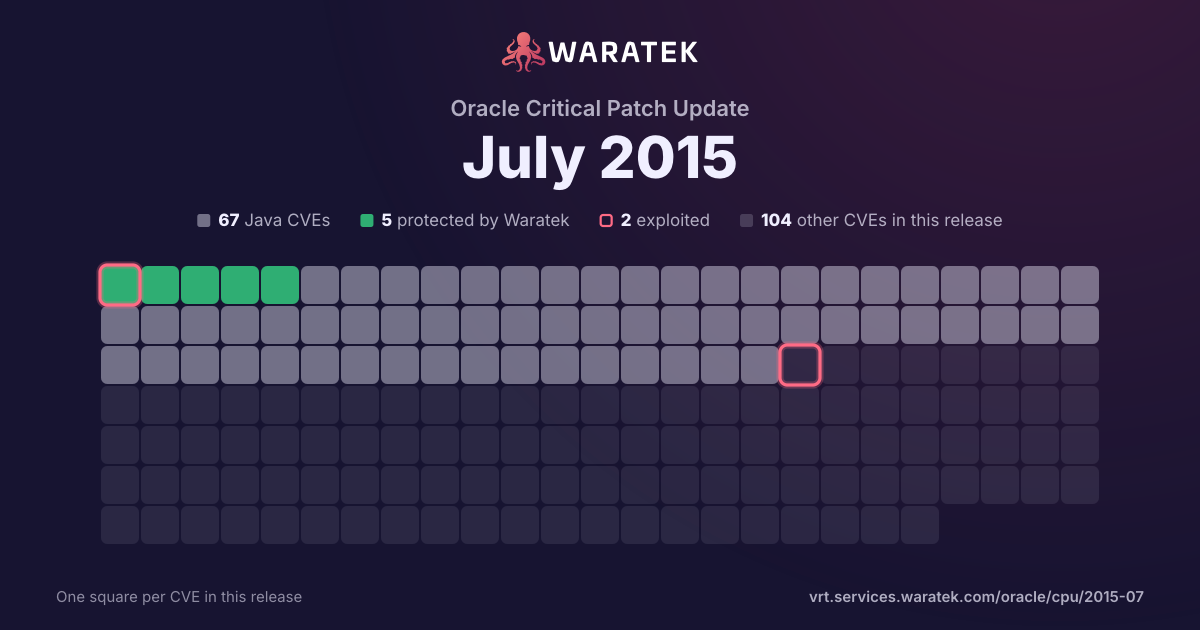
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 163 matches · 65 in Waratek scope · 3 protected · 1 exploited · 1 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
163matches
65in Waratek scope39.9%
3protected1.8%
1exploited0.6%
1CISA KEV0.6%
3public PoC1.8%
3EPSS ≥ 0.51.8%
Protected by Waratek
3
1.8%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
62
38.0%
Outside Waratek scope
35
21.5%
Not applicable
63
38.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
3
1.8%
partly blocked
0
0.0%
not blocked
160
98.2%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 149 / month
Dec 143
Outside Waratek scope1
Not applicable2
High1
Medium2
not blocked3
No public exploit3
Jan 153
Outside Waratek scope1
Not applicable2
High1
Medium2
not blocked3
Working exploit published1
No public exploit2
Feb 152
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
No public exploit2
Mar 152
Not applicable2
High1
Medium1
not blocked2
No public exploit2
Apr 151
Outside Waratek scope1
Low1
not blocked1
Forecast only1
May 152
Outside Waratek scope1
Not applicable1
High1
Low1
not blocked2
Working exploit published1
Proof of concept only1
Jun 151
No exploit published1
High1
not blocked1
No public exploit1
Jul 15149
Protected by Waratek3
No exploit published61
Outside Waratek scope30
Not applicable55
Critical1
High21
Medium96
Low31
blocked by ARMR today3
not blocked146
Exploited1
No public exploit148
Dec 14Jan 15Feb 15Mar 15Apr 15May 15Jun 15Jul 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-2622 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 allows remote attackers to affect integrity via unknown vectors related to Fluid Core. |
| CVE-2015-2621 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33, allows remote attackers to affect confidentiality via vectors related to JMX. |
| CVE-2015-2620 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.43 and earlier and 5.6.23 and earlier allows remote authenticated users to affect confidentiality via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-2619 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45, JavaFX 2.2.80, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via unknown vectors related to 2D. |
| CVE-2015-2618 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Input validation. |
| CVE-2015-2617 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Partition. |
| CVE-2015-2616 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 3.3 and 4.2 allows local users to affect availability via unknown vectors related to DevFS. |
| CVE-2015-2615 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.0.6, 12.1.3, and 12.2.3 allows remote attackers to affect confidentiality via unknown vectors related to Portal. |
| CVE-2015-2614 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.2 allows local users to affect availability via vectors related to NVM Express SSD driver. |
| CVE-2015-2613 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2015-2612 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Svcs component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote attackers to affect confidentiality via vectors related to LDAP Security Adapter. |
| CVE-2015-2611 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.24 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2015-2610 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Popup windows. |
| CVE-2015-2609 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.2 allows local users to affect availability via vectors related to CPU performance counters drivers. |
| CVE-2015-2607 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce Platform 3.0.2, 3.1.1, 3.1.2, 11.0, and 11.1 allows remote attackers to affect confidentiality via unknown vectors related to Content Acquisition System. |
| CVE-2015-2606 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, and CVE-2015-4745. |
| CVE-2015-2605 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2604 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2603 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2602 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2601 | Medium | 2015-07-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, JRockit R28.3.6, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality via vectors related to JCE. |
| CVE-2015-2600 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Svcs component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-2599 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Scheduler component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2015-2598 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the mobile app in Oracle Business Intelligence Enterprise Edition in Oracle Fusion Middleware before 11.1.1.7.0 (11.6.39) allows remote authenticated users to affect integrity via unknown vectors related to Mobile - iPad. |
| CVE-2015-2597 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Install. |
| CVE-2015-2596 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 allows remote attackers to affect integrity via unknown vectors related to Hotspot. |
| CVE-2015-2595 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle OLAP component in Oracle Database Server 12.1.0.1 and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-2594 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 4.0.32, 4.1.40, 4.2.32, and 4.3.30 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core. |
| CVE-2015-2593 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Configuration Service. |
| CVE-2015-2592 | Low | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2015-2584. |
| CVE-2015-2591 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise Portal - Interaction Hub component in Oracle PeopleSoft Products 9.1.00 allows remote authenticated users to affect integrity via unknown vectors related to Enterprise Portal. |
| CVE-2015-2590 | Critical | 2015-07-16 | Outside Waratek scope | Exploited | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2015-4732. |
| CVE-2015-2589 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect availability via vectors related to S10 Branded Zone. |
| CVE-2015-2588 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote attackers to affect integrity via vectors related to PIA Core Technology. |
| CVE-2015-2587 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, and 15.0 allows remote attackers to affect integrity via vectors related to SWSE Server Infrastructure. |
| CVE-2015-2586 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 4.2.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2015-2585 | Low | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server before 5.0 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2015-2584 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2015-2592. |
| CVE-2015-2583 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Data Store component in Oracle Berkeley DB 11.2.5.1.29, 11.2.5.2.42, 11.2.5.3.28, and 12.1.6.0.35 allows local users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-2624, CVE-2015-2626, CVE-2015-2640, CVE-2015-2654, CVE-2015-2656, CVE-2015-4754, CVE-2015-4764, CVE-2015-4775, CVE-2015-4776, CVE-2015-4777, CVE-2015-4778, CVE-2015-4780, CVE-2015-4781, CVE-2015-4782, CVE-2015-4783, CVE-2015-4784, CVE-2015-4785, CVE-2015-4786, CVE-2015-4787, CVE-2015-4789, and CVE-2015-4790. |
| CVE-2015-2582 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.43 and earlier and 5.6.24 and earlier allows remote authenticated users to affect availability via vectors related to GIS. |
| CVE-2015-2581 | Medium | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop component in Oracle Virtualization 5.1 and 5.2 allows remote attackers to affect confidentiality and availability via unknown vectors related to JServer. |
| CVE-2015-2580 | Low | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect availability via vectors related to NFSv4. |
| CVE-2015-1926 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.8.0 and 11.1.1.9.0, and the Oracle Applications Framework component in Oracle E-Business Suite 12.2.3 and 12.2.4, allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Portal. |
| CVE-2015-0468 | Medium | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-0467 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Talent Acquisition Manager component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2015-0446 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0445 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0444 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-0443 | Medium | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-2636, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2014-0230 | High | 2015-06-07 | No exploit published | No public exploit | Apache Tomcat 6.x before 6.0.44, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle cases where an HTTP response occurs before finishing the reading of an entire request body, which allows remote attackers to cause a denial of service (thread consumption) via a series of aborted upload attempts. |
| CVE-2015-4000 | Low | 2015-05-21 | Outside Waratek scope | Proof of concept only | The TLS protocol 1.2 and earlier, when a DHE_EXPORT ciphersuite is enabled on a server but not on a client, does not properly convey a DHE_EXPORT choice, which allows man-in-the-middle attackers to conduct cipher-downgrade attacks by rewriting a ClientHello with DHE replaced by DHE_EXPORT and then rewriting a ServerHello with DHE_EXPORT replaced by DHE, aka the "Logjam" issue. |
| CVE-2015-3456 | High | 2015-05-13 | Not applicable | Working exploit published | The Floppy Disk Controller (FDC) in QEMU, as used in Xen 4.5.x and earlier and KVM, allows local guest users to cause a denial of service (out-of-bounds write and guest crash) or possibly execute arbitrary code via the (1) FD_CMD_READ_ID, (2) FD_CMD_DRIVE_SPECIFICATION_COMMAND, or other unspecified commands, aka VENOM. |
| CVE-2015-2808 | Low | 2015-04-01 | Outside Waratek scope | Forecast only | The RC4 algorithm, as used in the TLS protocol and SSL protocol, does not properly combine state data with key data during the initialization phase, which makes it easier for remote attackers to conduct plaintext-recovery attacks against the initial bytes of a stream by sniffing network traffic that occasionally relies on keys affected by the Invariance Weakness, and then using a brute-force approach involving LSB values, aka the "Bar Mitzvah" issue. |
| CVE-2015-1803 | High | 2015-03-20 | Not applicable | No public exploit | The bdfReadCharacters function in bitmap/bdfread.c in X.Org libXfont before 1.4.9 and 1.5.x before 1.5.1 does not properly handle character bitmaps it cannot read, which allows remote authenticated users to cause a denial of service (NULL pointer dereference and crash) and possibly execute arbitrary code via a crafted BDF font file. |
| CVE-2015-0286 | Medium | 2015-03-19 | Not applicable | No public exploit | The ASN1_TYPE_cmp function in crypto/asn1/a_type.c in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a does not properly perform boolean-type comparisons, which allows remote attackers to cause a denial of service (invalid read operation and application crash) via a crafted X.509 certificate to an endpoint that uses the certificate-verification feature. |
| CVE-2014-0227 | Medium | 2015-02-16 | Outside Waratek scope | No public exploit | java/org/apache/coyote/http11/filters/ChunkedInputFilter.java in Apache Tomcat 6.x before 6.0.42, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle attempts to continue reading data after an error has occurred, which allows remote attackers to conduct HTTP request smuggling attacks or cause a denial of service (resource consumption) by streaming data with malformed chunked transfer coding. |
| CVE-2015-0255 | Medium | 2015-02-13 | Not applicable | No public exploit | X.Org Server (aka xserver and xorg-server) before 1.16.3 and 1.17.x before 1.17.1 allows remote attackers to obtain sensitive information from process memory or cause a denial of service (crash) via a crafted string length value in a XkbSetGeometry request. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-3571 | Medium | 2015-01-09 | Not applicable | No public exploit | OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via a crafted DTLS message that is processed with a different read operation for the handshake header than for the handshake body, related to the dtls1_get_record function in d1_pkt.c and the ssl3_read_n function in s3_pkt.c. |
| CVE-2014-3570 | Medium | 2015-01-09 | Not applicable | No public exploit | The BN_sqr implementation in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k does not properly calculate the square of a BIGNUM value, which might make it easier for remote attackers to defeat cryptographic protection mechanisms via unspecified vectors, related to crypto/bn/asm/mips.pl, crypto/bn/asm/x86_64-gcc.c, and crypto/bn/bn_asm.c. |
| CVE-2014-1569 | High | 2014-12-15 | Not applicable | No public exploit | The definite_length_decoder function in lib/util/quickder.c in Mozilla Network Security Services (NSS) before 3.16.2.4 and 3.17.x before 3.17.3 does not ensure that the DER encoding of an ASN.1 length is properly formed, which allows remote attackers to conduct data-smuggling attacks by using a long byte sequence for an encoding, as demonstrated by the SEC_QuickDERDecodeItem function's improper handling of an arbitrary-length encoding of 0x00. |
| CVE-2014-8102 | Medium | 2014-12-10 | Not applicable | No public exploit | The SProcXFixesSelectSelectionInput function in the XFixes extension in X.Org X Window System (aka X11 or X) X11R6.8.0 and X.Org Server (aka xserver and xorg-server) before 1.16.3 allows remote authenticated users to cause a denial of service (out-of-bounds read or write) or possibly execute arbitrary code via a crafted length value. |
| CVE-2014-7809 | Medium | 2014-12-10 | Outside Waratek scope | No public exploit | Apache Struts 2.0.0 through 2.3.x before 2.3.20 uses predictable <s:token/> values, which allows remote attackers to bypass the CSRF protection mechanism. |