
Oracle Critical Patch Update July 2015
Released July 2015 · Oracle's advisory ↗ · ← Critical Patch Update, April 2015 · Critical Patch Update, October 2015 →
171 CVEs in this release, one square each
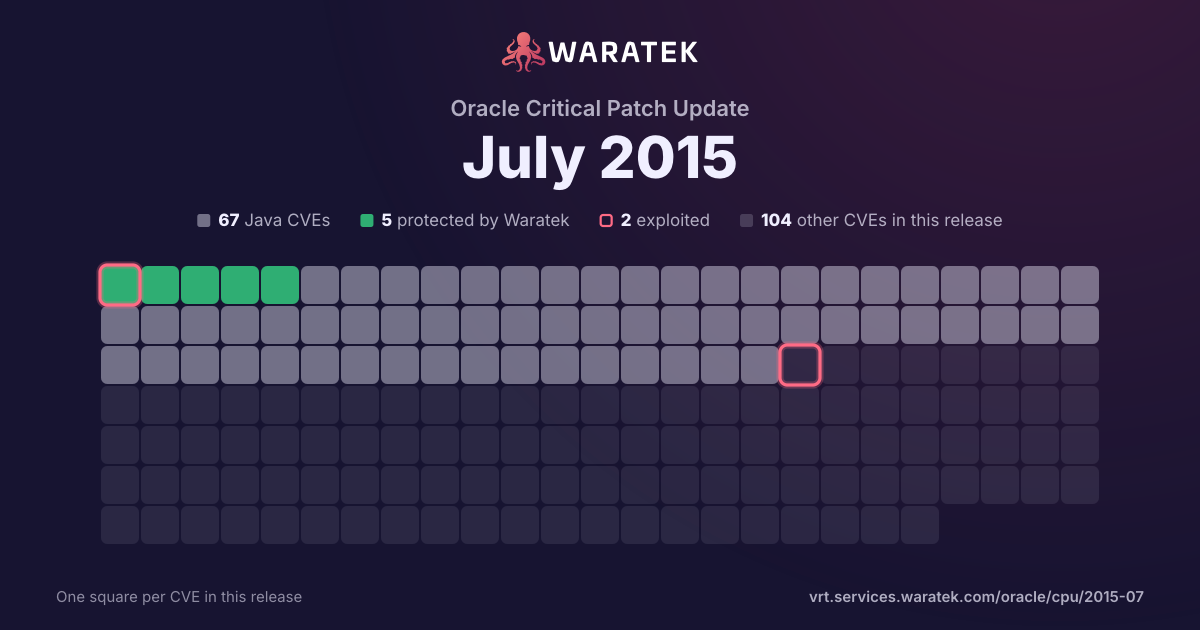
By status
5Protected by Waratek62No exploit published36Outside Waratek scope68Not applicable
2Exploited, marked by the ring
No exploit published. For 60 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 27 matches · 11 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
27matches
11in Waratek scope40.7%
1protected3.7%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
3.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
10
37.0%
Outside Waratek scope
9
33.3%
Not applicable
7
25.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
3.7%
partly blocked
0
0.0%
not blocked
26
96.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
27
100.0%
split by
peak 21 / quarter
Q2 121
Not applicable1
High1
not blocked1
No public exploit1
Q3 120
Q4 120
Q1 130
Q2 130
Q3 130
Q4 130
Q1 140
Q2 140
Q3 141
Not applicable1
High1
not blocked1
No public exploit1
Q4 142
Not applicable2
High2
not blocked2
No public exploit2
Q1 151
Not applicable1
High1
not blocked1
No public exploit1
Q2 151
No exploit published1
High1
not blocked1
No public exploit1
Q3 1521
Protected by Waratek1
No exploit published9
Outside Waratek scope9
Not applicable2
High21
blocked by ARMR today1
not blocked20
No public exploit21
Q3 12Q1 13Q3 13Q1 14Q3 14Q1 15Q3 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4760 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2015-4748 | High | 2015-07-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JRockit R28.3.6; and Java SE Embedded 7u75 and Embedded 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security. |
| CVE-2015-4745 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, and CVE-2015-2606. |
| CVE-2015-4736 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2015-4733 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to RMI. |
| CVE-2015-4732 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2015-2590. |
| CVE-2015-4731 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; Java SE Embedded 7u75; and Java SE Embedded 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JMX. |
| CVE-2015-4727 | High | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Virtualization Sun Ray Software before 5.4.4 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Web Console. |
| CVE-2015-2663 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, and 6.3.0 through 6.3.7 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Business Process Automation. |
| CVE-2015-2638 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45; JavaFX 2.2.80; and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2015-2636 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality based on Trillium, a different vulnerability than CVE-2015-0443, CVE-2015-0444, CVE-2015-0445, CVE-2015-0446, CVE-2015-2634, CVE-2015-2635, CVE-2015-4758, and CVE-2015-4759. |
| CVE-2015-2631 | High | 2015-07-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to rmformat. |
| CVE-2015-2629 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-0457. |
| CVE-2015-2628 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u95, 7u80, and 8u45, and Java SE Embedded 7u75 and 8u33 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to CORBA. |
| CVE-2015-2606 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, and CVE-2015-4745. |
| CVE-2015-2605 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2604, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2604 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2603, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2603 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2602, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2602 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Information Discovery Studio component in Oracle Fusion Middleware 2.2.2, 2.3, 2.4, 3.0, and 3.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Integrator, a different vulnerability than CVE-2015-2603, CVE-2015-2604, CVE-2015-2605, CVE-2015-2606, and CVE-2015-4745. |
| CVE-2015-2597 | High | 2015-07-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u80 and 8u45 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Install. |
| CVE-2015-2593 | High | 2015-07-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Configuration Service. |
| CVE-2014-0230 | High | 2015-06-07 | No exploit published | No public exploit | Apache Tomcat 6.x before 6.0.44, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle cases where an HTTP response occurs before finishing the reading of an entire request body, which allows remote attackers to cause a denial of service (thread consumption) via a series of aborted upload attempts. |
| CVE-2015-1803 | High | 2015-03-20 | Not applicable | No public exploit | The bdfReadCharacters function in bitmap/bdfread.c in X.Org libXfont before 1.4.9 and 1.5.x before 1.5.1 does not properly handle character bitmaps it cannot read, which allows remote authenticated users to cause a denial of service (NULL pointer dereference and crash) and possibly execute arbitrary code via a crafted BDF font file. |
| CVE-2014-1569 | High | 2014-12-15 | Not applicable | No public exploit | The definite_length_decoder function in lib/util/quickder.c in Mozilla Network Security Services (NSS) before 3.16.2.4 and 3.17.x before 3.17.3 does not ensure that the DER encoding of an ASN.1 length is properly formed, which allows remote attackers to conduct data-smuggling attacks by using a long byte sequence for an encoding, as demonstrated by the SEC_QuickDERDecodeItem function's improper handling of an arbitrary-length encoding of 0x00. |
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |
| CVE-2014-1568 | High | 2014-09-25 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.16.2.1, 3.16.x before 3.16.5, and 3.17.x before 3.17.1, as used in Mozilla Firefox before 32.0.3, Mozilla Firefox ESR 24.x before 24.8.1 and 31.x before 31.1.1, Mozilla Thunderbird before 24.8.1 and 31.x before 31.1.2, Mozilla SeaMonkey before 2.29.1, Google Chrome before 37.0.2062.124 on Windows and OS X, and Google Chrome OS before 37.0.2062.120, does not properly parse ASN.1 values in X.509 certificates, which makes it easier for remote attackers to spoof RSA signatures via a crafted certificate, aka a "signature malleability" issue. |
| CVE-2012-0036 | High | 2012-04-13 | Not applicable | No public exploit | curl and libcurl 7.2x before 7.24.0 do not properly consider special characters during extraction of a pathname from a URL, which allows remote attackers to conduct data-injection attacks via a crafted URL, as demonstrated by a CRLF injection attack on the (1) IMAP, (2) POP3, or (3) SMTP protocol. |