
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
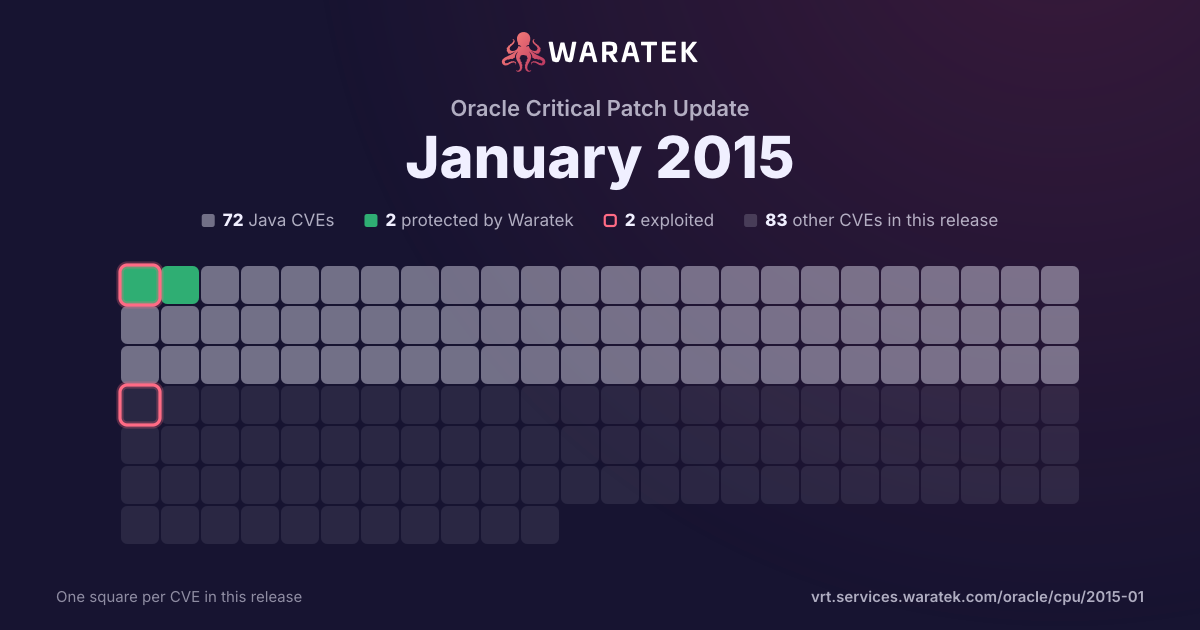
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 18 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
18matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC11.1%
2EPSS ≥ 0.511.1%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
18
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
18
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
11.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
16
88.9%
split by
peak 16 / month
Feb 141
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Mar 140
Apr 140
May 140
Jun 140
Jul 141
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Aug 140
Sep 140
Oct 140
Nov 140
Dec 140
Jan 1516
Outside Waratek scope16
Medium16
not blocked16
Working exploit published1
No public exploit15
Feb 14Mar 14Apr 14May 14Jun 14Jul 14Aug 14Sep 14Oct 14Nov 14Dec 14Jan 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0421 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to the installation process. |
| CVE-2015-0409 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.21 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2015-0407 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality via unknown vectors related to Swing. |
| CVE-2015-0406 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality and availability via unknown vectors related to Deployment. |
| CVE-2015-0403 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2015-0400 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality via unknown vectors related to Libraries. |
| CVE-2015-0382 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier and 5.6.21 and earlier allows remote attackers to affect availability via unknown vectors related to Server : Replication, a different vulnerability than CVE-2015-0381. |
| CVE-2015-0381 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier and 5.6.21 and earlier allows remote attackers to affect availability via unknown vectors related to Server : Replication, a different vulnerability than CVE-2015-0382. |
| CVE-2015-0373 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the OJVM component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-0371 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect integrity and availability via unknown vectors. |
| CVE-2014-6593 | Medium | 2015-01-21 | Outside Waratek scope | Working exploit published | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25; Java SE Embedded 7u71 and 8u6; and JRockit 27.8.4 and 28.3.4 allows remote attackers to affect confidentiality and integrity via vectors related to JSSE. |
| CVE-2014-6587 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-6578 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Workspace Manager component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to SDO_TOPO and WMSYS.LT. |
| CVE-2014-6577 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XML Developer's Kit for C component in Oracle Database Server 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality via unknown vectors. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the original researcher's claim that this is an XML external entity (XXE) vulnerability in the XML parser, which allows attackers to conduct internal port scanning, perform SSRF attacks, or cause a denial of service via a crafted (1) http: or (2) ftp: URI. |
| CVE-2014-6541 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Recovery component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2, when running on Windows, allows remote authenticated users to affect confidentiality via vectors related to DBMS_IR. |
| CVE-2014-6514 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the PL/SQL component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-0226 | Medium | 2014-07-20 | Outside Waratek scope | Working exploit published | Race condition in the mod_status module in the Apache HTTP Server before 2.4.10 allows remote attackers to cause a denial of service (heap-based buffer overflow), or possibly obtain sensitive credential information or execute arbitrary code, via a crafted request that triggers improper scoreboard handling within the status_handler function in modules/generators/mod_status.c and the lua_ap_scoreboard_worker function in modules/lua/lua_request.c. |
| CVE-2013-4286 | Medium | 2014-02-26 | Outside Waratek scope | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |