
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
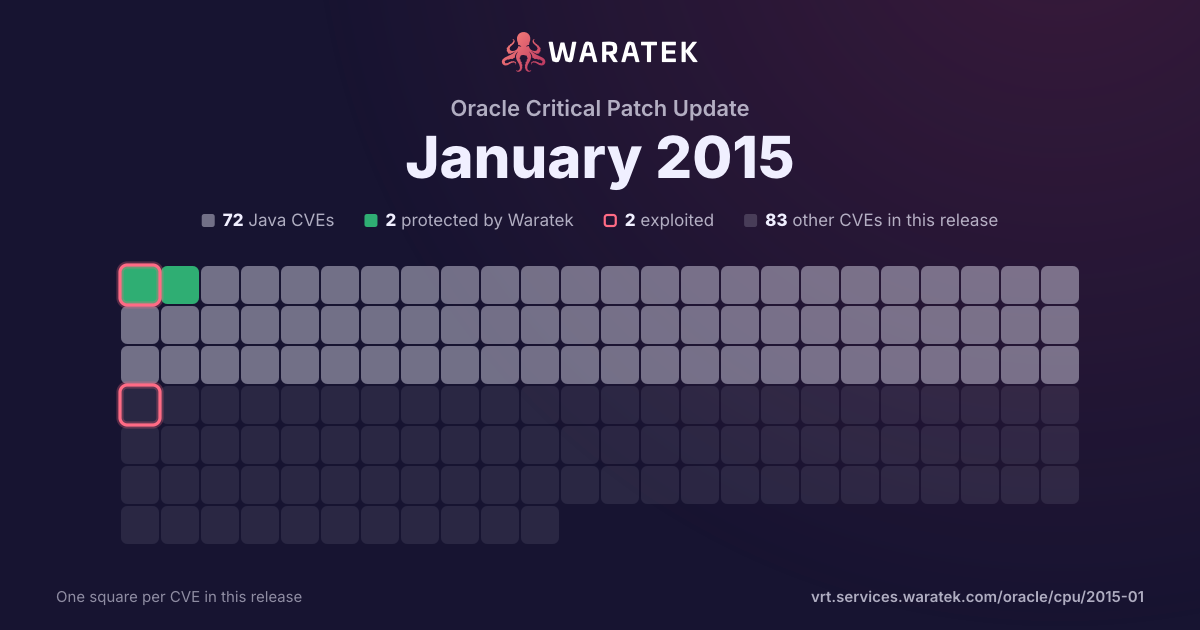
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 1 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 0 EPSS ≥ 0.5
5matches
1in Waratek scope20.0%
1protected20.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC40.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
20.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
4
80.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
20.0%
partly blocked
0
0.0%
not blocked
4
80.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
1
20.0%
Forecast only
0
0.0%
No public exploit
3
60.0%
split by
peak 2 / quarter
Q3 111
Not applicable1
High1
not blocked1
Working exploit published1
Q4 110
Q1 120
Q2 120
Q3 120
Q4 120
Q1 131
Not applicable1
High1
not blocked1
No public exploit1
Q2 130
Q3 131
Not applicable1
High1
not blocked1
No public exploit1
Q4 132
Protected by Waratek1
Not applicable1
High2
blocked by ARMR today1
not blocked1
Proof of concept only1
No public exploit1
Q3 11Q4 11Q1 12Q2 12Q3 12Q4 12Q1 13Q2 13Q3 13Q4 13
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-1741 | High | 2013-11-18 | Not applicable | No public exploit | Integer overflow in Mozilla Network Security Services (NSS) 3.15 before 3.15.3 allows remote attackers to cause a denial of service or possibly have unspecified other impact via a large size value. |
| CVE-2013-2186 | High | 2013-10-28 | Protected by Waratek | Proof of concept only | The DiskFileItem class in Apache Commons FileUpload, as used in Red Hat JBoss BRMS 5.3.1; JBoss Portal 4.3 CP07, 5.2.2, and 6.0.0; and Red Hat JBoss Web Server 1.0.2 allows remote attackers to write to arbitrary files via a NULL byte in a file name in a serialized instance. |
| CVE-2013-4784 | High | 2013-07-08 | Not applicable | No public exploit | The HP Integrated Lights-Out (iLO) BMC implementation allows remote attackers to bypass authentication and execute arbitrary IPMI commands by using cipher suite 0 (aka cipher zero) and an arbitrary password. |
| CVE-2010-5107 | High | 2013-03-07 | Not applicable | No public exploit | The default configuration of OpenSSH through 6.1 enforces a fixed time limit between establishing a TCP connection and completing a login, which makes it easier for remote attackers to cause a denial of service (connection-slot exhaustion) by periodically making many new TCP connections. |
| CVE-2011-1944 | High | 2011-09-02 | Not applicable | Working exploit published | Integer overflow in xpath.c in libxml2 2.6.x through 2.6.32 and 2.7.x through 2.7.8, and libxml 1.8.16 and earlier, allows context-dependent attackers to cause a denial of service (crash) and possibly execute arbitrary code via a crafted XML file that triggers a heap-based buffer overflow when adding a new namespace node, related to handling of XPath expressions. |