
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
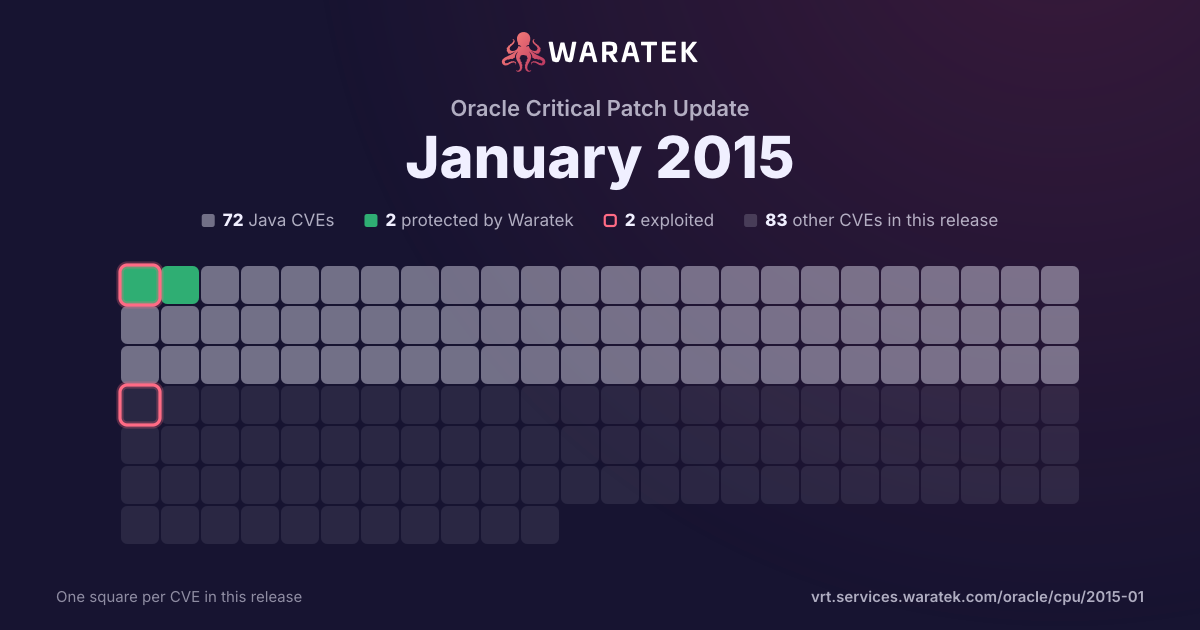
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 17 matches · 3 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
17matches
3in Waratek scope17.6%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC5.9%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
5.9%
No exploit published
2
11.8%
Outside Waratek scope
8
47.1%
Not applicable
6
35.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
17
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
5.9%
Forecast only
0
0.0%
No public exploit
16
94.1%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0437 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2015-0424 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Integrated Lights Out Manager (ILOM) component in Oracle Sun Systems Products Suite ILOM prior to 3.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to IPMI. |
| CVE-2015-0412 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JAX-WS. |
| CVE-2015-0411 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier, and 5.6.21 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Server : Security : Encryption. |
| CVE-2015-0408 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to RMI. |
| CVE-2015-0396 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Admin Console. |
| CVE-2015-0395 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-6601 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-6598 | High | 2015-01-21 | Mitigation candidate | Proof of concept only | Unspecified vulnerability in the Oracle Communications Diameter Signaling Router component in Oracle Communications Applications 3.x, 4.x, and 5.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Signaling - DPI. |
| CVE-2014-6567 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the researcher's claim that this is a stack-based buffer overflow in DBMS_AW.EXECUTE, which allows code execution via a long Current Directory Alias (CDA) command. |
| CVE-2014-6565 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Portal SEC. |
| CVE-2014-6549 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-6524 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Kernel. |
| CVE-2014-6521 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via vectors related to CDE - Power Management Utility. |
| CVE-2014-6510 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Power Management Utility. |
| CVE-2014-4259 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |