
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
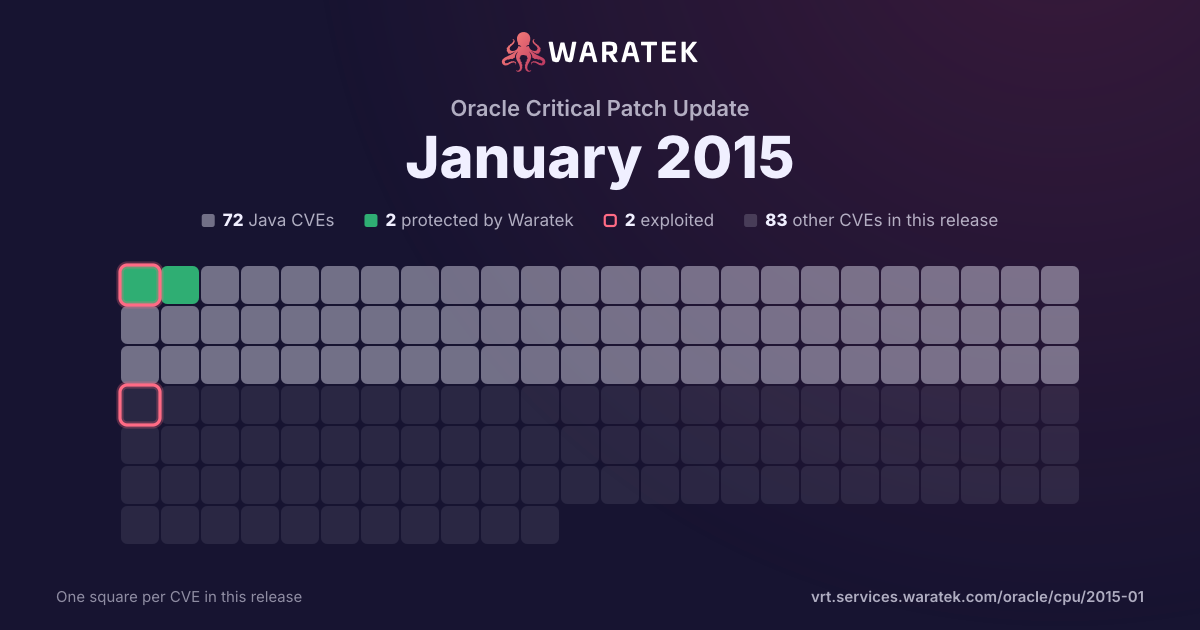
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 25 matches · 2 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 9 public PoC · 8 EPSS ≥ 0.5
25matches
2in Waratek scope8.0%
0protected0.0%
1exploited4.0%
0CISA KEV0.0%
9public PoC36.0%
8EPSS ≥ 0.532.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
8.0%
Outside Waratek scope
4
16.0%
Not applicable
19
76.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
25
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 11 / year
20031
Not applicable1
Medium1
not blocked1
Working exploit published1
20041
Not applicable1
Medium1
not blocked1
Working exploit published1
20050
20060
20070
20080
20090
20100
20115
No exploit published1
Not applicable4
High1
Medium4
not blocked5
Working exploit published3
Proof of concept only1
No public exploit1
20120
20137
Not applicable7
High3
Medium4
not blocked7
No public exploit7
201411
No exploit published1
Outside Waratek scope4
Not applicable6
High3
Medium7
Low1
not blocked11
Exploited1
Working exploit published1
Proof of concept only1
Forecast only1
No public exploit7
200320042005200620072008200920102011201220132014
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |
| CVE-2014-3566 | Low | 2014-10-15 | Outside Waratek scope | Proof of concept only | The SSL protocol 3.0, as used in OpenSSL through 1.0.1i and other products, uses nondeterministic CBC padding, which makes it easier for man-in-the-middle attackers to obtain cleartext data via a padding-oracle attack, aka the "POODLE" issue. |
| CVE-2014-1568 | High | 2014-09-25 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.16.2.1, 3.16.x before 3.16.5, and 3.17.x before 3.17.1, as used in Mozilla Firefox before 32.0.3, Mozilla Firefox ESR 24.x before 24.8.1 and 31.x before 31.1.1, Mozilla Thunderbird before 24.8.1 and 31.x before 31.1.2, Mozilla SeaMonkey before 2.29.1, Google Chrome before 37.0.2062.124 on Windows and OS X, and Google Chrome OS before 37.0.2062.120, does not properly parse ASN.1 values in X.509 certificates, which makes it easier for remote attackers to spoof RSA signatures via a crafted certificate, aka a "signature malleability" issue. |
| CVE-2014-0226 | Medium | 2014-07-20 | Outside Waratek scope | Working exploit published | Race condition in the mod_status module in the Apache HTTP Server before 2.4.10 allows remote attackers to cause a denial of service (heap-based buffer overflow), or possibly obtain sensitive credential information or execute arbitrary code, via a crafted request that triggers improper scoreboard handling within the status_handler function in modules/generators/mod_status.c and the lua_ap_scoreboard_worker function in modules/lua/lua_request.c. |
| CVE-2014-4212 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Fusion Middleware component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Process Mgmt and Notification. |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2013-5704 | Medium | 2014-04-15 | Not applicable | Forecast only | The mod_headers module in the Apache HTTP Server 2.2.22 allows remote attackers to bypass "RequestHeader unset" directives by placing a header in the trailer portion of data sent with chunked transfer coding. NOTE: the vendor states "this is not a security issue in httpd as such." |
| CVE-2014-0098 | Medium | 2014-03-18 | Not applicable | No public exploit | The log_cookie function in mod_log_config.c in the mod_log_config module in the Apache HTTP Server before 2.4.8 allows remote attackers to cause a denial of service (segmentation fault and daemon crash) via a crafted cookie that is not properly handled during truncation. |
| CVE-2013-6438 | Medium | 2014-03-18 | Not applicable | No public exploit | The dav_xml_get_cdata function in main/util.c in the mod_dav module in the Apache HTTP Server before 2.4.8 does not properly remove whitespace characters from CDATA sections, which allows remote attackers to cause a denial of service (daemon crash) via a crafted DAV WRITE request. |
| CVE-2013-4286 | Medium | 2014-02-26 | Outside Waratek scope | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |
| CVE-2013-6450 | Medium | 2014-01-01 | Not applicable | No public exploit | The DTLS retransmission implementation in OpenSSL 1.0.0 before 1.0.0l and 1.0.1 before 1.0.1f does not properly maintain data structures for digest and encryption contexts, which might allow man-in-the-middle attackers to trigger the use of a different context and cause a denial of service (application crash) by interfering with packet delivery, related to ssl/d1_both.c and ssl/t1_enc.c. |
| CVE-2013-4545 | Medium | 2013-11-23 | Not applicable | No public exploit | cURL and libcurl 7.18.0 through 7.32.0, when built with OpenSSL, disables the certificate CN and SAN name field verification (CURLOPT_SSL_VERIFYHOST) when the digital signature verification (CURLOPT_SSL_VERIFYPEER) is disabled, which allows man-in-the-middle attackers to spoof SSL servers via an arbitrary valid certificate. |
| CVE-2013-1741 | High | 2013-11-18 | Not applicable | No public exploit | Integer overflow in Mozilla Network Security Services (NSS) 3.15 before 3.15.3 allows remote attackers to cause a denial of service or possibly have unspecified other impact via a large size value. |
| CVE-2013-2877 | Medium | 2013-07-10 | Not applicable | No public exploit | parser.c in libxml2 before 2.9.0, as used in Google Chrome before 28.0.1500.71 and other products, allows remote attackers to cause a denial of service (out-of-bounds read) via a document that ends abruptly, related to the lack of certain checks for the XML_PARSER_EOF state. |
| CVE-2013-4784 | High | 2013-07-08 | Not applicable | No public exploit | The HP Integrated Lights-Out (iLO) BMC implementation allows remote attackers to bypass authentication and execute arbitrary IPMI commands by using cipher suite 0 (aka cipher zero) and an arbitrary password. |
| CVE-2013-0338 | Medium | 2013-04-25 | Not applicable | No public exploit | libxml2 2.9.0 and earlier allows context-dependent attackers to cause a denial of service (CPU and memory consumption) via an XML file containing an entity declaration with long replacement text and many references to this entity, aka "internal entity expansion" with linear complexity. |
| CVE-2010-5107 | High | 2013-03-07 | Not applicable | No public exploit | The default configuration of OpenSSH through 6.1 enforces a fixed time limit between establishing a TCP connection and completing a login, which makes it easier for remote attackers to cause a denial of service (connection-slot exhaustion) by periodically making many new TCP connections. |
| CVE-2013-1620 | Medium | 2013-02-08 | Not applicable | No public exploit | The TLS implementation in Mozilla Network Security Services (NSS) does not properly consider timing side-channel attacks on a noncompliant MAC check operation during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, a related issue to CVE-2013-0169. |
| CVE-2011-4461 | Medium | 2011-12-30 | No exploit published | No public exploit | Jetty 8.1.0.RC2 and earlier computes hash values for form parameters without restricting the ability to trigger hash collisions predictably, which allows remote attackers to cause a denial of service (CPU consumption) by sending many crafted parameters. |
| CVE-2011-3607 | Medium | 2011-11-08 | Not applicable | Working exploit published | Integer overflow in the ap_pregsub function in server/util.c in the Apache HTTP Server 2.0.x through 2.0.64 and 2.2.x through 2.2.21, when the mod_setenvif module is enabled, allows local users to gain privileges via a .htaccess file with a crafted SetEnvIf directive, in conjunction with a crafted HTTP request header, leading to a heap-based buffer overflow. |
| CVE-2011-3368 | Medium | 2011-10-05 | Not applicable | Working exploit published | The mod_proxy module in the Apache HTTP Server 1.3.x through 1.3.42, 2.0.x through 2.0.64, and 2.2.x through 2.2.21 does not properly interact with use of (1) RewriteRule and (2) ProxyPassMatch pattern matches for configuration of a reverse proxy, which allows remote attackers to send requests to intranet servers via a malformed URI containing an initial @ (at sign) character. |
| CVE-2011-3389 | Medium | 2011-09-06 | Not applicable | Proof of concept only | The SSL protocol, as used in certain configurations in Microsoft Windows and Microsoft Internet Explorer, Mozilla Firefox, Google Chrome, Opera, and other products, encrypts data by using CBC mode with chained initialization vectors, which allows man-in-the-middle attackers to obtain plaintext HTTP headers via a blockwise chosen-boundary attack (BCBA) on an HTTPS session, in conjunction with JavaScript code that uses (1) the HTML5 WebSocket API, (2) the Java URLConnection API, or (3) the Silverlight WebClient API, aka a "BEAST" attack. |
| CVE-2011-1944 | High | 2011-09-02 | Not applicable | Working exploit published | Integer overflow in xpath.c in libxml2 2.6.x through 2.6.32 and 2.7.x through 2.7.8, and libxml 1.8.16 and earlier, allows context-dependent attackers to cause a denial of service (crash) and possibly execute arbitrary code via a crafted XML file that triggers a heap-based buffer overflow when adding a new namespace node, related to handling of XPath expressions. |
| CVE-2004-0230 | Medium | 2004-08-18 | Not applicable | Working exploit published | TCP, when using a large Window Size, makes it easier for remote attackers to guess sequence numbers and cause a denial of service (connection loss) to persistent TCP connections by repeatedly injecting a TCP RST packet, especially in protocols that use long-lived connections, such as BGP. |
| CVE-2003-0001 | Medium | 2003-01-17 | Not applicable | Working exploit published | Multiple ethernet Network Interface Card (NIC) device drivers do not pad frames with null bytes, which allows remote attackers to obtain information from previous packets or kernel memory by using malformed packets, as demonstrated by Etherleak. |