
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
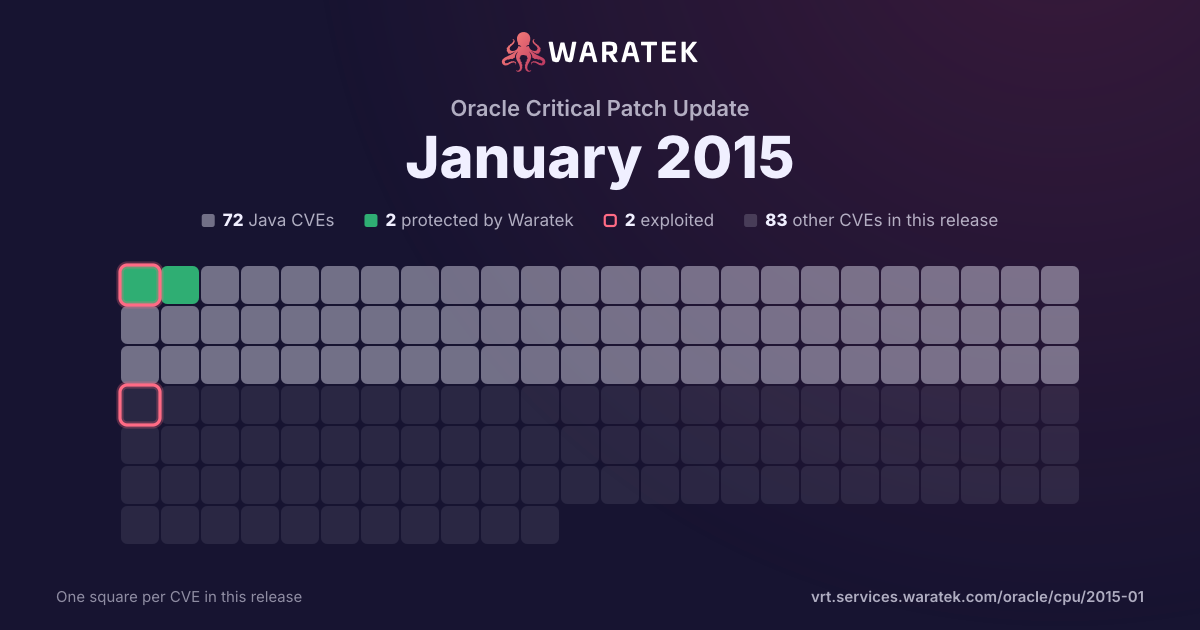
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 128 matches · 68 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
128matches
68in Waratek scope53.1%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC1.6%
1EPSS ≥ 0.50.8%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
0.8%
No exploit published
67
52.3%
Outside Waratek scope
28
21.9%
Not applicable
32
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
128
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
0.8%
Proof of concept only
1
0.8%
Forecast only
0
0.0%
No public exploit
126
98.4%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-6574 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM for Process component in Oracle Supply Chain Products Suite 6.1.0.3 allows remote attackers to affect integrity via unknown vectors related to Testing Protocol Library. |
| CVE-2014-6573 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 11.1.3 and 12.1.4 allows remote attackers to affect integrity via unknown vectors related to User Interface Framework. |
| CVE-2014-6572 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to List of Values. |
| CVE-2014-6571 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Web Listener, a different vulnerability than CVE-2011-1944. |
| CVE-2014-6570 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via unknown vectors related to File System, a different vulnerability than CVE-2014-6600 and CVE-2015-0397. |
| CVE-2014-6569 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality via vectors related to CIE Related Components. |
| CVE-2014-6568 | Low | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier, and 5.6.21 and earlier, allows remote authenticated users to affect availability via vectors related to Server : InnoDB : DML. |
| CVE-2014-6567 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the researcher's claim that this is a stack-based buffer overflow in DBMS_AW.EXECUTE, which allows code execution via a long Current Directory Alias (CDA) command. |
| CVE-2014-6566 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote authenticated users to affect integrity via unknown vectors related to Portal. |
| CVE-2014-6565 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Portal SEC. |
| CVE-2014-6556 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to AD_DDL. |
| CVE-2014-6549 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-6548 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle SOA Suite component in Oracle Fusion Middleware 11.1.1.7 allows local users to affect confidentiality, integrity, and availability via vectors related to B2B Engine. |
| CVE-2014-6541 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Recovery component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2, when running on Windows, allows remote authenticated users to affect confidentiality via vectors related to DBMS_IR. |
| CVE-2014-6528 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - System Management component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Server Infrastructure. |
| CVE-2014-6526 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Directory Server Enterprise Edition component in Oracle Fusion Middleware 7.0 allows remote attackers to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-6525 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Templates. |
| CVE-2014-6524 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Kernel. |
| CVE-2014-6521 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via vectors related to CDE - Power Management Utility. |
| CVE-2014-6518 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 allows local users to affect integrity and availability via vectors related to Unix File System (UFS). |
| CVE-2014-6514 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the PL/SQL component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-6510 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Power Management Utility. |
| CVE-2014-6509 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect availability via unknown vectors related to Kernel. |
| CVE-2014-6481 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 allows remote attackers to affect confidentiality via vectors related to KSSL. |
| CVE-2014-6480 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-4279 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote authenticated users to affect integrity via vectors related to PIA Core Technology. |
| CVE-2014-4259 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-0191 | Medium | 2015-01-21 | Not applicable | No public exploit | The xmlParserHandlePEReference function in parser.c in libxml2 before 2.9.2, as used in Web Listener in Oracle HTTP Server in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 and other products, loads external parameter entities regardless of whether entity substitution or validation is enabled, which allows remote attackers to cause a denial of service (resource consumption) via a crafted XML document. |