
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
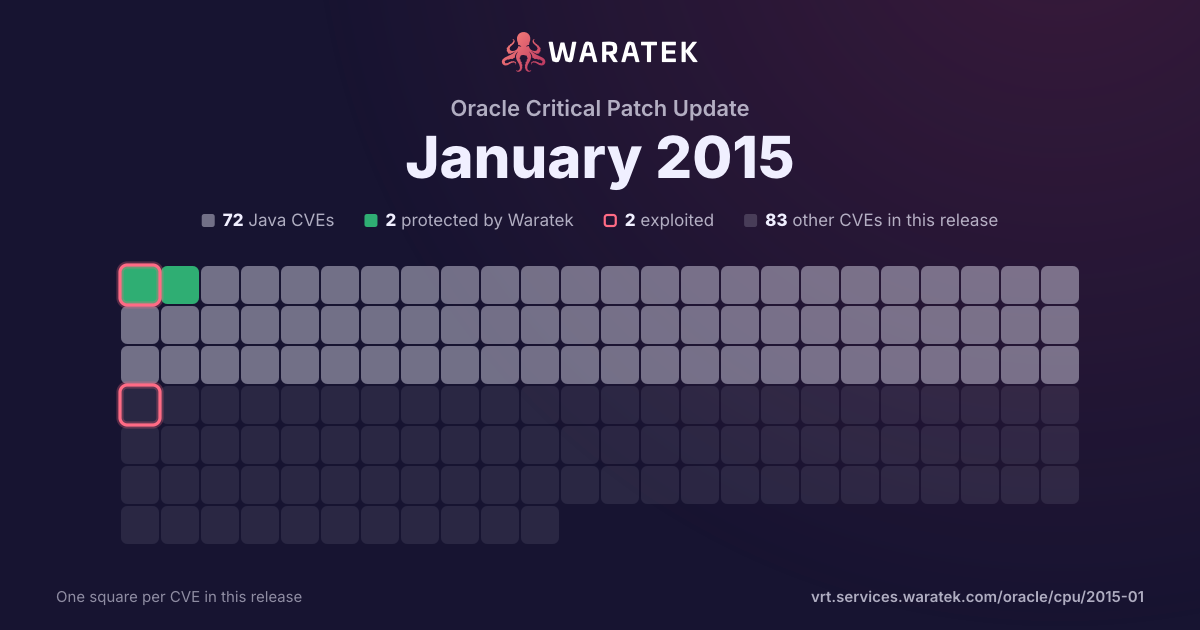
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 136 matches · 70 in Waratek scope · 1 protected · 2 exploited · 0 CISA KEV · 6 public PoC · 6 EPSS ≥ 0.5
136matches
70in Waratek scope51.5%
1protected0.7%
2exploited1.5%
0CISA KEV0.0%
6public PoC4.4%
6EPSS ≥ 0.54.4%
Protected by Waratek
1
0.7%
Rule in development
0
0.0%
Mitigation candidate
1
0.7%
No exploit published
68
50.0%
Outside Waratek scope
31
22.8%
Not applicable
35
25.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
0.7%
partly blocked
0
0.0%
not blocked
135
99.3%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 128 / month
Apr 142
Protected by Waratek1
Not applicable1
High1
Medium1
blocked by ARMR today1
not blocked1
Exploited1
Forecast only1
May 140
Jun 141
Outside Waratek scope1
High1
not blocked1
Exploited1
Jul 142
No exploit published1
Outside Waratek scope1
Medium2
not blocked2
Working exploit published1
No public exploit1
Aug 140
Sep 141
Not applicable1
High1
not blocked1
No public exploit1
Oct 142
Outside Waratek scope1
Not applicable1
High1
Low1
not blocked2
Proof of concept only1
No public exploit1
Nov 140
Dec 140
Jan 15128
Mitigation candidate1
No exploit published67
Outside Waratek scope28
Not applicable32
High16
Medium86
Low26
not blocked128
Working exploit published1
Proof of concept only1
No public exploit126
Apr 14May 14Jun 14Jul 14Aug 14Sep 14Oct 14Nov 14Dec 14Jan 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-6574 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM for Process component in Oracle Supply Chain Products Suite 6.1.0.3 allows remote attackers to affect integrity via unknown vectors related to Testing Protocol Library. |
| CVE-2014-6573 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 11.1.3 and 12.1.4 allows remote attackers to affect integrity via unknown vectors related to User Interface Framework. |
| CVE-2014-6572 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to List of Values. |
| CVE-2014-6571 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Web Listener, a different vulnerability than CVE-2011-1944. |
| CVE-2014-6570 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11 allows local users to affect availability via unknown vectors related to File System, a different vulnerability than CVE-2014-6600 and CVE-2015-0397. |
| CVE-2014-6569 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality via vectors related to CIE Related Components. |
| CVE-2014-6568 | Low | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier, and 5.6.21 and earlier, allows remote authenticated users to affect availability via vectors related to Server : InnoDB : DML. |
| CVE-2014-6567 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the researcher's claim that this is a stack-based buffer overflow in DBMS_AW.EXECUTE, which allows code execution via a long Current Directory Alias (CDA) command. |
| CVE-2014-6566 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote authenticated users to affect integrity via unknown vectors related to Portal. |
| CVE-2014-6565 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Portal SEC. |
| CVE-2014-6556 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to AD_DDL. |
| CVE-2014-6549 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-6548 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle SOA Suite component in Oracle Fusion Middleware 11.1.1.7 allows local users to affect confidentiality, integrity, and availability via vectors related to B2B Engine. |
| CVE-2014-6541 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Recovery component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2, when running on Windows, allows remote authenticated users to affect confidentiality via vectors related to DBMS_IR. |
| CVE-2014-6528 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - System Management component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Server Infrastructure. |
| CVE-2014-6526 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Directory Server Enterprise Edition component in Oracle Fusion Middleware 7.0 allows remote attackers to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-6525 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Templates. |
| CVE-2014-6524 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Kernel. |
| CVE-2014-6521 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via vectors related to CDE - Power Management Utility. |
| CVE-2014-6518 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 allows local users to affect integrity and availability via vectors related to Unix File System (UFS). |
| CVE-2014-6514 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the PL/SQL component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-6510 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Power Management Utility. |
| CVE-2014-6509 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect availability via unknown vectors related to Kernel. |
| CVE-2014-6481 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 allows remote attackers to affect confidentiality via vectors related to KSSL. |
| CVE-2014-6480 | Medium | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-4279 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote authenticated users to affect integrity via vectors related to PIA Core Technology. |
| CVE-2014-4259 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-0191 | Medium | 2015-01-21 | Not applicable | No public exploit | The xmlParserHandlePEReference function in parser.c in libxml2 before 2.9.2, as used in Web Listener in Oracle HTTP Server in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 and other products, loads external parameter entities regardless of whether entity substitution or validation is enabled, which allows remote attackers to cause a denial of service (resource consumption) via a crafted XML document. |
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |
| CVE-2014-3566 | Low | 2014-10-15 | Outside Waratek scope | Proof of concept only | The SSL protocol 3.0, as used in OpenSSL through 1.0.1i and other products, uses nondeterministic CBC padding, which makes it easier for man-in-the-middle attackers to obtain cleartext data via a padding-oracle attack, aka the "POODLE" issue. |
| CVE-2014-1568 | High | 2014-09-25 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.16.2.1, 3.16.x before 3.16.5, and 3.17.x before 3.17.1, as used in Mozilla Firefox before 32.0.3, Mozilla Firefox ESR 24.x before 24.8.1 and 31.x before 31.1.1, Mozilla Thunderbird before 24.8.1 and 31.x before 31.1.2, Mozilla SeaMonkey before 2.29.1, Google Chrome before 37.0.2062.124 on Windows and OS X, and Google Chrome OS before 37.0.2062.120, does not properly parse ASN.1 values in X.509 certificates, which makes it easier for remote attackers to spoof RSA signatures via a crafted certificate, aka a "signature malleability" issue. |
| CVE-2014-0226 | Medium | 2014-07-20 | Outside Waratek scope | Working exploit published | Race condition in the mod_status module in the Apache HTTP Server before 2.4.10 allows remote attackers to cause a denial of service (heap-based buffer overflow), or possibly obtain sensitive credential information or execute arbitrary code, via a crafted request that triggers improper scoreboard handling within the status_handler function in modules/generators/mod_status.c and the lua_ap_scoreboard_worker function in modules/lua/lua_request.c. |
| CVE-2014-4212 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Fusion Middleware component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Process Mgmt and Notification. |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2013-5704 | Medium | 2014-04-15 | Not applicable | Forecast only | The mod_headers module in the Apache HTTP Server 2.2.22 allows remote attackers to bypass "RequestHeader unset" directives by placing a header in the trailer portion of data sent with chunked transfer coding. NOTE: the vendor states "this is not a security issue in httpd as such." |