
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
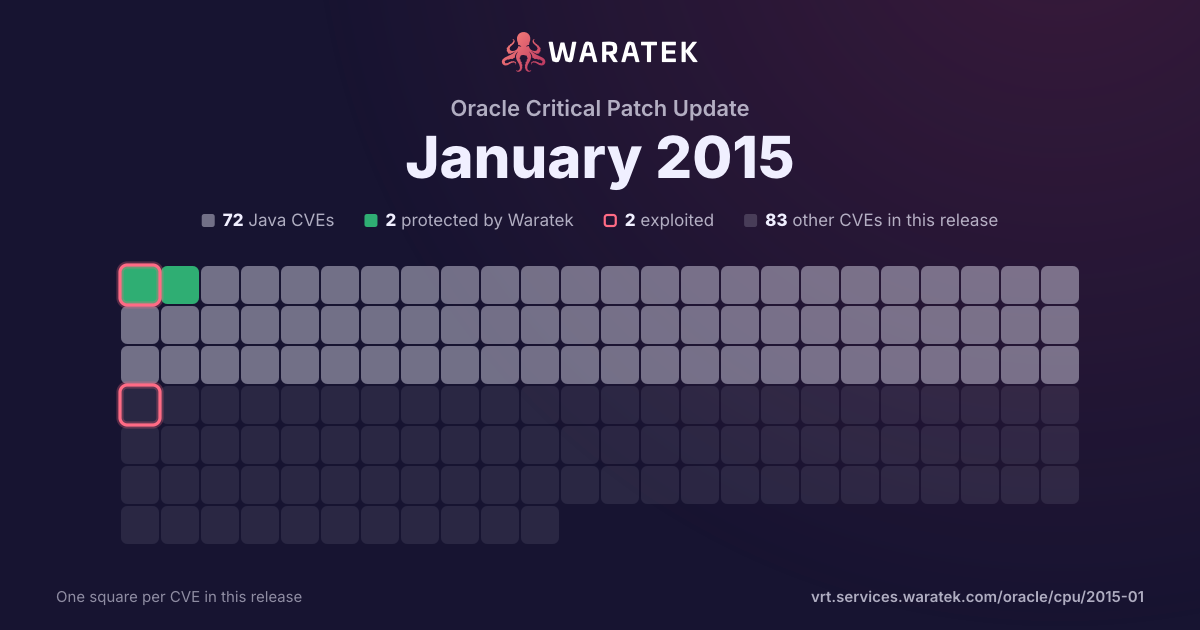
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 20 matches · 2 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
20matches
2in Waratek scope10.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
10.0%
Outside Waratek scope
8
40.0%
Not applicable
10
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
20
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
20
100.0%
split by
peak 15 / quarter
Q1 131
Not applicable1
High1
not blocked1
No public exploit1
Q2 130
Q3 131
Not applicable1
High1
not blocked1
No public exploit1
Q4 131
Not applicable1
High1
not blocked1
No public exploit1
Q1 140
Q2 140
Q3 141
Not applicable1
High1
not blocked1
No public exploit1
Q4 141
Not applicable1
High1
not blocked1
No public exploit1
Q1 1515
No exploit published2
Outside Waratek scope8
Not applicable5
High15
not blocked15
No public exploit15
Q1 13Q2 13Q3 13Q4 13Q1 14Q2 14Q3 14Q4 14Q1 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0437 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2015-0424 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Integrated Lights Out Manager (ILOM) component in Oracle Sun Systems Products Suite ILOM prior to 3.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to IPMI. |
| CVE-2015-0412 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JAX-WS. |
| CVE-2015-0411 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier, and 5.6.21 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Server : Security : Encryption. |
| CVE-2015-0408 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to RMI. |
| CVE-2015-0396 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Admin Console. |
| CVE-2015-0395 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u75, 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-6601 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u85, 7u72, and 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-6567 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the researcher's claim that this is a stack-based buffer overflow in DBMS_AW.EXECUTE, which allows code execution via a long Current Directory Alias (CDA) command. |
| CVE-2014-6565 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 9.1.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Portal SEC. |
| CVE-2014-6549 | High | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u25 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-6524 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Kernel. |
| CVE-2014-6521 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, integrity, and availability via vectors related to CDE - Power Management Utility. |
| CVE-2014-6510 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Power Management Utility. |
| CVE-2014-4259 | High | 2015-01-21 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to System management. |
| CVE-2014-3567 | High | 2014-10-19 | Not applicable | No public exploit | Memory leak in the tls_decrypt_ticket function in t1_lib.c in OpenSSL before 0.9.8zc, 1.0.0 before 1.0.0o, and 1.0.1 before 1.0.1j allows remote attackers to cause a denial of service (memory consumption) via a crafted session ticket that triggers an integrity-check failure. |
| CVE-2014-1568 | High | 2014-09-25 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.16.2.1, 3.16.x before 3.16.5, and 3.17.x before 3.17.1, as used in Mozilla Firefox before 32.0.3, Mozilla Firefox ESR 24.x before 24.8.1 and 31.x before 31.1.1, Mozilla Thunderbird before 24.8.1 and 31.x before 31.1.2, Mozilla SeaMonkey before 2.29.1, Google Chrome before 37.0.2062.124 on Windows and OS X, and Google Chrome OS before 37.0.2062.120, does not properly parse ASN.1 values in X.509 certificates, which makes it easier for remote attackers to spoof RSA signatures via a crafted certificate, aka a "signature malleability" issue. |
| CVE-2013-1741 | High | 2013-11-18 | Not applicable | No public exploit | Integer overflow in Mozilla Network Security Services (NSS) 3.15 before 3.15.3 allows remote attackers to cause a denial of service or possibly have unspecified other impact via a large size value. |
| CVE-2013-4784 | High | 2013-07-08 | Not applicable | No public exploit | The HP Integrated Lights-Out (iLO) BMC implementation allows remote attackers to bypass authentication and execute arbitrary IPMI commands by using cipher suite 0 (aka cipher zero) and an arbitrary password. |
| CVE-2010-5107 | High | 2013-03-07 | Not applicable | No public exploit | The default configuration of OpenSSH through 6.1 enforces a fixed time limit between establishing a TCP connection and completing a login, which makes it easier for remote attackers to cause a denial of service (connection-slot exhaustion) by periodically making many new TCP connections. |