
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
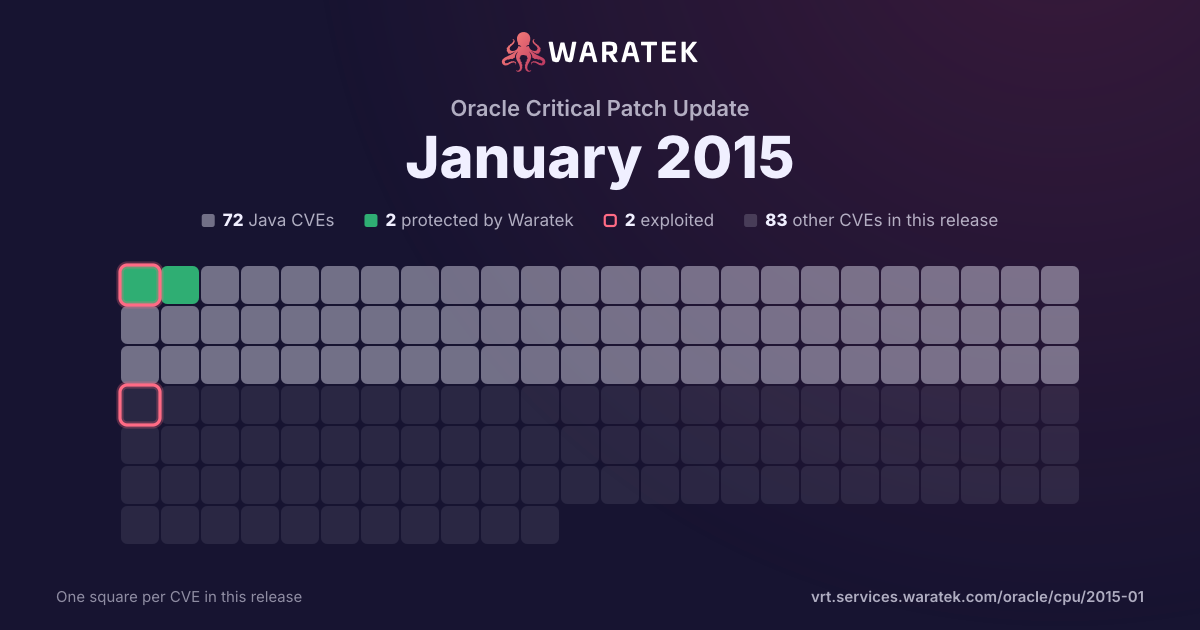
By status
2Protected by Waratek2Mitigation candidate74No exploit published23Outside Waratek scope54Not applicable
2Exploited, marked by the ring
No exploit published. For 71 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 22 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
22matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
22
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
22
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
22
100.0%
split by
peak 19 / quarter
Q4 111
No exploit published1
Medium1
not blocked1
No public exploit1
Q1 120
Q2 120
Q3 120
Q4 120
Q1 130
Q2 130
Q3 130
Q4 130
Q1 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q2 140
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 140
Q1 1519
No exploit published19
High1
Medium15
Low3
not blocked19
No public exploit19
Q1 12Q3 12Q1 13Q3 13Q1 14Q3 14Q1 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0434 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5, 11.1.1.7, 11.1.2.1, and 11.1.2.2 allows remote attackers to affect confidentiality via vectors related to Integration with OAM. |
| CVE-2015-0420 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Forms component in Oracle Fusion Middleware 11.1.1.7 and 11.1.2.2 allows remote attackers to affect confidentiality via unknown vectors related to Forms Services. |
| CVE-2015-0414 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle SOA Suite component in Oracle Fusion Middleware 11.1.1.7 and 12.1.3.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Fabric Layer. |
| CVE-2015-0401 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Directory Server Enterprise Edition component in Oracle Fusion Middleware 7.0 and 11.1.1.7 allows remote authenticated users to affect integrity via unknown vectors related to Admin Console. |
| CVE-2015-0399 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 10.1.3.4.2 and 11.1.1.7 allows remote authenticated users to affect confidentiality via unknown vectors related to Analytics Web General. |
| CVE-2015-0396 | High | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Admin Console. |
| CVE-2015-0389 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle OpenSSO component in Oracle Fusion Middleware 8.0 Update 2 Patch 5 allows remote authenticated users to affect integrity via vectors related to SAML, a different vulnerability than CVE-2014-6592. |
| CVE-2015-0386 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect availability via unknown vectors related to Web Listener, a different vulnerability than CVE-2013-0338, CVE-2013-2877, and CVE-2014-0191. |
| CVE-2015-0376 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Content component in Oracle Fusion Middleware 11.1.1.8.0 allows remote attackers to affect integrity via unknown vectors related to Content Server. |
| CVE-2015-0372 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Containers for J2EE component in Oracle Fusion Middleware 10.1.3.5 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2015-0367 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5, 11.1.1.7, 11.1.2.1, and 11.1.2.2 allows remote attackers to affect integrity via vectors related to SSO Engine. |
| CVE-2015-0362 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to BI Publisher Security. |
| CVE-2014-6592 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle OpenSSO component in Oracle Fusion Middleware 8.0 Update 2 Patch 5 allows remote authenticated users to affect integrity via vectors related to SAML, a different vulnerability than CVE-2015-0389. |
| CVE-2014-6580 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Reports Developer component in Oracle Fusion Middleware 11.1.1.7 and 11.1.2.2 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2014-6576 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Adaptive Access Manager component in Oracle Fusion Middleware 11.1.1.5, 11.1.1.7, 11.1.2.1, and 11.1.2.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to OAM Integration. |
| CVE-2014-6571 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Web Listener, a different vulnerability than CVE-2011-1944. |
| CVE-2014-6569 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality via vectors related to CIE Related Components. |
| CVE-2014-6548 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle SOA Suite component in Oracle Fusion Middleware 11.1.1.7 allows local users to affect confidentiality, integrity, and availability via vectors related to B2B Engine. |
| CVE-2014-6526 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Directory Server Enterprise Edition component in Oracle Fusion Middleware 7.0 allows remote attackers to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-4212 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Fusion Middleware component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Process Mgmt and Notification. |
| CVE-2013-4286 | Medium | 2014-02-26 | No exploit published | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |
| CVE-2011-4461 | Medium | 2011-12-30 | No exploit published | No public exploit | Jetty 8.1.0.RC2 and earlier computes hash values for form parameters without restricting the ability to trigger hash collisions predictably, which allows remote attackers to cause a denial of service (CPU consumption) by sending many crafted parameters. |