
Oracle Critical Patch Update January 2015
Released January 2015 · Oracle's advisory ↗ · ← Critical Patch Update, October 2014 · Critical Patch Update, April 2015 →
155 CVEs in this release, one square each
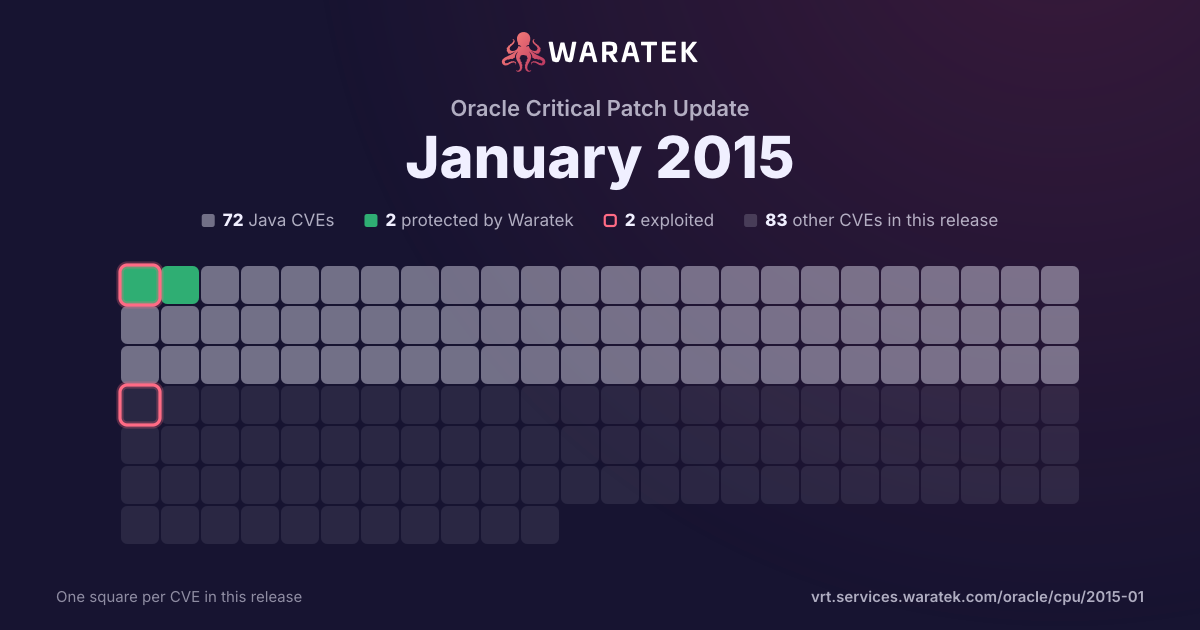
By status
2Protected by Waratek1Mitigation candidate69No exploit published32Outside Waratek scope51Not applicable
2Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 10 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
10matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
10
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
10
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
10
100.0%
split by
peak 10 / month
Jan 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0415 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 12.1.3 allows remote authenticated users to affect integrity via unknown vectors related to Session Management. |
| CVE-2015-0404 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Error Messages. |
| CVE-2015-0393 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to DB Privileges. NOTE: the previous information is from the January 2015 CPU. Oracle has not commented on the researcher's claim that the PUBLIC role is granted the INDEX privilege for the DUAL table during a "seeded install," which allows remote authenticated users to gain SYSDBA privileges and execute arbitrary code. |
| CVE-2015-0380 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Telecommunications Billing Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to OA Based UI for Bill Summary. |
| CVE-2014-6583 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 11.5.10.2, 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, and 12.1.3. allows remote attackers to affect confidentiality and integrity via unknown vectors related to Audience. |
| CVE-2014-6582 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HCM Configuration Workbench component in Oracle E-Business Suite 11.5.10.2, 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality via unknown vectors related to Rapid Implementation. |
| CVE-2014-6581 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Intelligence component in Oracle E-Business Suite 11.5.10.2, 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Extract/Load Programs. |
| CVE-2014-6572 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.0.4, 12.0.5, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to List of Values. |
| CVE-2014-6556 | Medium | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to AD_DDL. |
| CVE-2014-6525 | Low | 2015-01-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect integrity via unknown vectors related to Templates. |