
Oracle Critical Patch Update October 2014
Released October 2014 · Oracle's advisory ↗ · ← Critical Patch Update, July 2014 · Critical Patch Update, January 2015 →
137 CVEs in this release, one square each
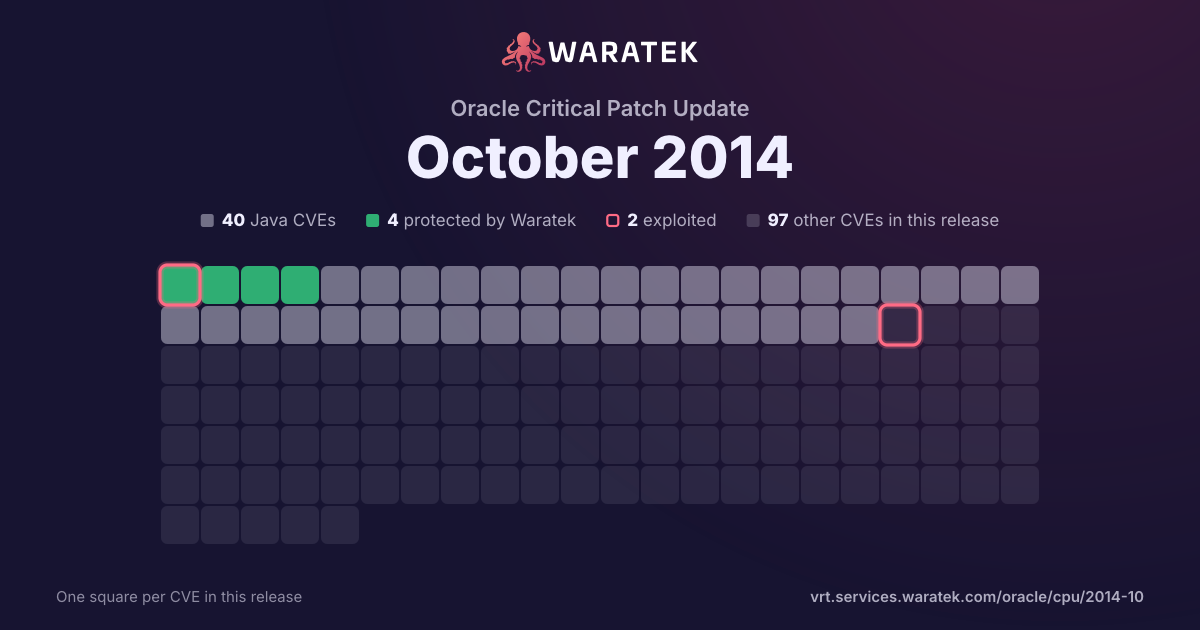
By status
4Protected by Waratek1Mitigation candidate35No exploit published60Outside Waratek scope37Not applicable
2Exploited, marked by the ring
No exploit published. For 32 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
3matches
1in Waratek scope33.3%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC66.7%
1EPSS ≥ 0.533.3%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
33.3%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
3
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
66.7%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
33.3%
split by
peak 1 / month
Dec 121
Not applicable1
Medium1
not blocked1
Working exploit published1
Jan 130
Feb 130
Mar 130
Apr 130
May 130
Jun 130
Jul 130
Aug 130
Sep 130
Oct 130
Nov 131
Not applicable1
High1
not blocked1
No public exploit1
Dec 130
Jan 140
Feb 140
Mar 140
Apr 141
Mitigation candidate1
High1
not blocked1
Working exploit published1
Dec 12Feb 13Apr 13Jun 13Aug 13Oct 13Dec 13Feb 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0050 | High | 2014-04-01 | Mitigation candidate | Working exploit published | MultipartStream.java in Apache Commons FileUpload before 1.3.1, as used in Apache Tomcat, JBoss Web, and other products, allows remote attackers to cause a denial of service (infinite loop and CPU consumption) via a crafted Content-Type header that bypasses a loop's intended exit conditions. |
| CVE-2013-1741 | High | 2013-11-18 | Not applicable | No public exploit | Integer overflow in Mozilla Network Security Services (NSS) 3.15 before 3.15.3 allows remote attackers to cause a denial of service or possibly have unspecified other impact via a large size value. |
| CVE-2012-5615 | Medium | 2012-12-03 | Not applicable | Working exploit published | Oracle MySQL 5.5.38 and earlier, 5.6.19 and earlier, and MariaDB 5.5.28a, 5.3.11, 5.2.13, 5.1.66, and possibly other versions, generates different error messages with different time delays depending on whether a user name exists, which allows remote attackers to enumerate valid usernames. |