
Oracle Critical Patch Update April 2014
Released April 2014 · Oracle's advisory ↗ · ← Critical Patch Update, January 2014 · Critical Patch Update, July 2014 →
104 CVEs in this release, one square each
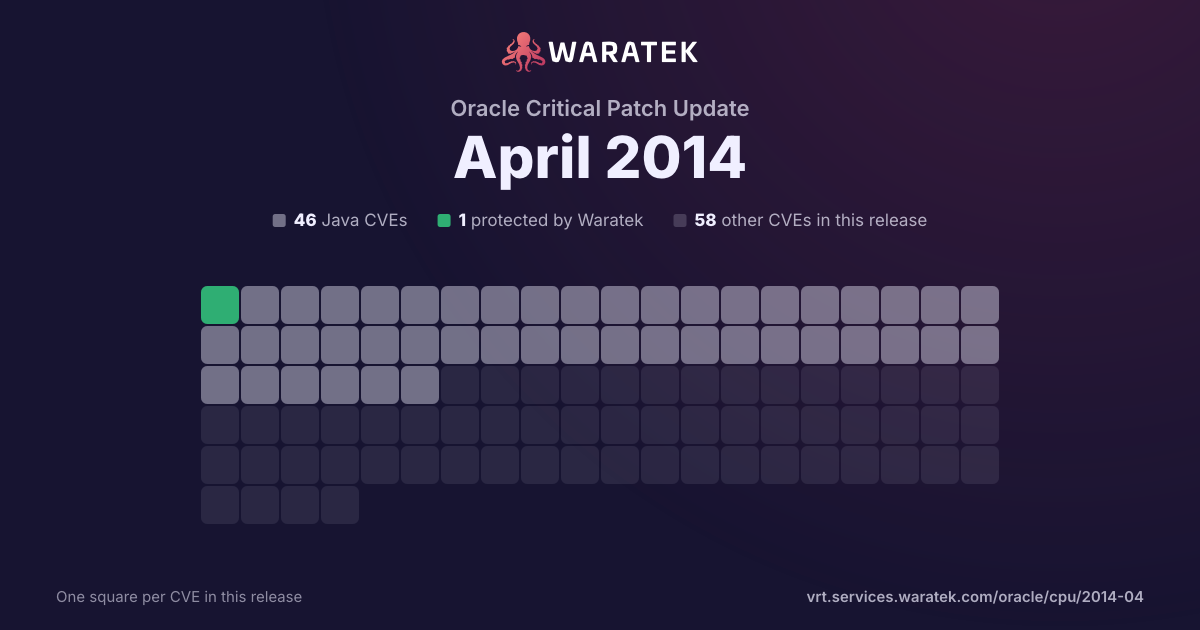
By status
1Protected by Waratek2Mitigation candidate43No exploit published33Outside Waratek scope25Not applicable
No exploit published. For 41 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 25 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
25matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC4.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
25
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
25
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
4.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
24
96.0%
split by
peak 20 / month
Feb 131
Not applicable1
Medium1
not blocked1
No public exploit1
Mar 130
Apr 130
May 130
Jun 130
Jul 130
Aug 130
Sep 130
Oct 130
Nov 131
Not applicable1
Medium1
not blocked1
No public exploit1
Dec 130
Jan 142
Not applicable2
High1
Medium1
not blocked2
No public exploit2
Feb 140
Mar 141
Not applicable1
Medium1
not blocked1
Working exploit published1
Apr 1420
Not applicable20
Medium15
Low5
not blocked20
No public exploit20
Feb 13Apr 13Jun 13Aug 13Oct 13Dec 13Feb 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-2463 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop (SGD) component in Oracle Virtualization 4.63, 4.71, 5.0, and 5.1 allows remote attackers to affect integrity via unknown vectors related to Workspace Web Application, a different vulnerability than CVE-2014-4232. |
| CVE-2014-2451 | Low | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.15 and earlier allows remote authenticated users to affect availability via unknown vectors related to Privileges. |
| CVE-2014-2450 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.15 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2014-2444 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.15 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to InnoDB. |
| CVE-2014-2442 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.15 and earlier allows remote authenticated users to affect availability via vectors related to MyISAM. |
| CVE-2014-2441 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 4.1.32, 4.2.24, and 4.3.10 allows local users to affect confidentiality, integrity, and availability via vectors related to Graphics driver (WDDM) for Windows guests. |
| CVE-2014-2440 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Client component in Oracle MySQL 5.5.36 and earlier and 5.6.16 and earlier allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-2439 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop (SGD) component in Oracle Virtualization 5.0 and 5.1 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Workspace Web Application. |
| CVE-2014-2438 | Low | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.35 and earlier and 5.6.15 and earlier allows remote authenticated users to affect availability via unknown vectors related to Replication. |
| CVE-2014-2436 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.36 and earlier and 5.6.16 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to RBR. |
| CVE-2014-2435 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.16 and earlier allows remote authenticated users to affect availability via unknown vectors related to InnoDB. |
| CVE-2014-2434 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.15 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2014-2432 | Low | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability Oracle the MySQL Server component 5.5.35 and earlier and 5.6.15 and earlier allows remote authenticated users to affect availability via unknown vectors related to Federated. |
| CVE-2014-2431 | Low | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.36 and earlier and 5.6.16 and earlier allows remote attackers to affect availability via unknown vectors related to Options. |
| CVE-2014-2430 | Low | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.36 and earlier and 5.6.16 and earlier allows remote authenticated users to affect availability via unknown vectors related to Performance Schema. |
| CVE-2014-2419 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.35 and earlier and 5.6.15 and earlier allows remote authenticated users to affect availability via unknown vectors related to Partition. |
| CVE-2014-0447 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via unknown vectors related to Kernel, a different vulnerability than CVE-2013-5876. |
| CVE-2014-0442 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9, 10, and 11.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Print Filter Utility. |
| CVE-2014-0421 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10, when running on the SPARC64-X Platform, allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-0384 | Medium | 2014-04-16 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.35 and earlier and 5.6.15 and earlier allows remote authenticated users to affect availability via vectors related to XML. |
| CVE-2014-0981 | Medium | 2014-03-31 | Not applicable | Working exploit published | VBox/GuestHost/OpenGL/util/net.c in Oracle VirtualBox before 3.2.22, 4.0.x before 4.0.24, 4.1.x before 4.1.32, 4.2.x before 4.2.24, and 4.3.x before 4.3.8, when using 3D Acceleration allows local guest OS users to execute arbitrary code on the Chromium server via crafted Chromium network pointer in a (1) CR_MESSAGE_READBACK or (2) CR_MESSAGE_WRITEBACK message to the VBoxSharedCrOpenGL service, which triggers an arbitrary pointer dereference and memory corruption. NOTE: this issue was MERGED with CVE-2014-0982 because it is the same type of vulnerability affecting the same set of versions. All CVE users should reference CVE-2014-0981 instead of CVE-2014-0982. |
| CVE-2013-6954 | Medium | 2014-01-12 | Not applicable | No public exploit | The png_do_expand_palette function in libpng before 1.6.8 allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via (1) a PLTE chunk of zero bytes or (2) a NULL palette, related to pngrtran.c and pngset.c. |
| CVE-2013-6462 | High | 2014-01-09 | Not applicable | No public exploit | Stack-based buffer overflow in the bdfReadCharacters function in bitmap/bdfread.c in X.Org libXfont 1.1 through 1.4.6 allows remote attackers to cause a denial of service (crash) or possibly execute arbitrary code via a long string in a character name in a BDF font file. |
| CVE-2013-6629 | Medium | 2013-11-19 | Not applicable | No public exploit | The get_sos function in jdmarker.c in (1) libjpeg 6b and (2) libjpeg-turbo through 1.3.0, as used in Google Chrome before 31.0.1650.48, Ghostscript, and other products, does not check for certain duplications of component data during the reading of segments that follow Start Of Scan (SOS) JPEG markers, which allows remote attackers to obtain sensitive information from uninitialized memory locations via a crafted JPEG image. |
| CVE-2013-1620 | Medium | 2013-02-08 | Not applicable | No public exploit | The TLS implementation in Mozilla Network Security Services (NSS) does not properly consider timing side-channel attacks on a noncompliant MAC check operation during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, a related issue to CVE-2013-0169. |