
Oracle Critical Patch Update April 2014
Released April 2014 · Oracle's advisory ↗ · ← Critical Patch Update, January 2014 · Critical Patch Update, July 2014 →
104 CVEs in this release, one square each
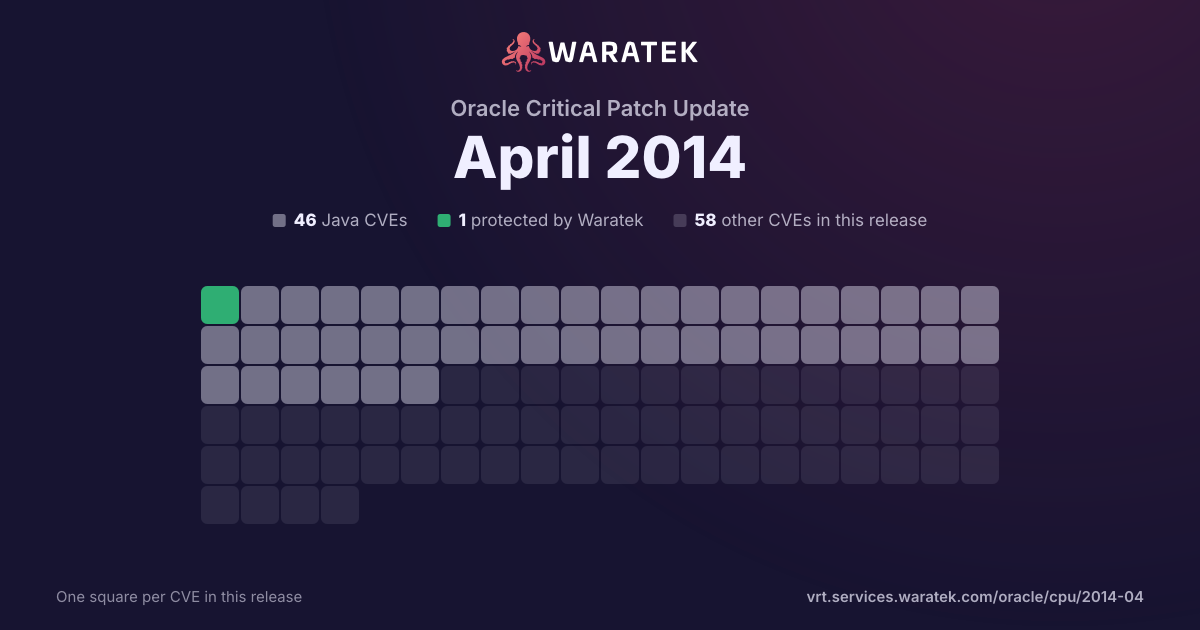
By status
1Protected by Waratek2Mitigation candidate43No exploit published33Outside Waratek scope25Not applicable
No exploit published. For 41 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 102 matches · 46 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 3 public PoC · 0 EPSS ≥ 0.5
102matches
46in Waratek scope45.1%
1protected1.0%
0exploited0.0%
0CISA KEV0.0%
3public PoC2.9%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
1.0%
Rule in development
0
0.0%
Mitigation candidate
2
2.0%
No exploit published
43
42.2%
Outside Waratek scope
33
32.4%
Not applicable
23
22.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
1.0%
partly blocked
0
0.0%
not blocked
101
99.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
3
2.9%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
99
97.1%
split by
peak 98 / month
Jan 142
Not applicable2
High1
Medium1
not blocked2
No public exploit2
Feb 141
No exploit published1
Medium1
not blocked1
No public exploit1
Mar 141
Not applicable1
Medium1
not blocked1
Working exploit published1
Apr 1498
Protected by Waratek1
Mitigation candidate2
No exploit published42
Outside Waratek scope33
Not applicable20
High23
Medium62
Low13
blocked by ARMR today1
not blocked97
Working exploit published2
No public exploit96
Jan 14Feb 14Mar 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-6954 | Medium | 2014-01-12 | Not applicable | No public exploit | The png_do_expand_palette function in libpng before 1.6.8 allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via (1) a PLTE chunk of zero bytes or (2) a NULL palette, related to pngrtran.c and pngset.c. |
| CVE-2013-6462 | High | 2014-01-09 | Not applicable | No public exploit | Stack-based buffer overflow in the bdfReadCharacters function in bitmap/bdfread.c in X.Org libXfont 1.1 through 1.4.6 allows remote attackers to cause a denial of service (crash) or possibly execute arbitrary code via a long string in a character name in a BDF font file. |