
Oracle Critical Patch Update April 2014
Released April 2014 · Oracle's advisory ↗ · ← Critical Patch Update, January 2014 · Critical Patch Update, July 2014 →
104 CVEs in this release, one square each
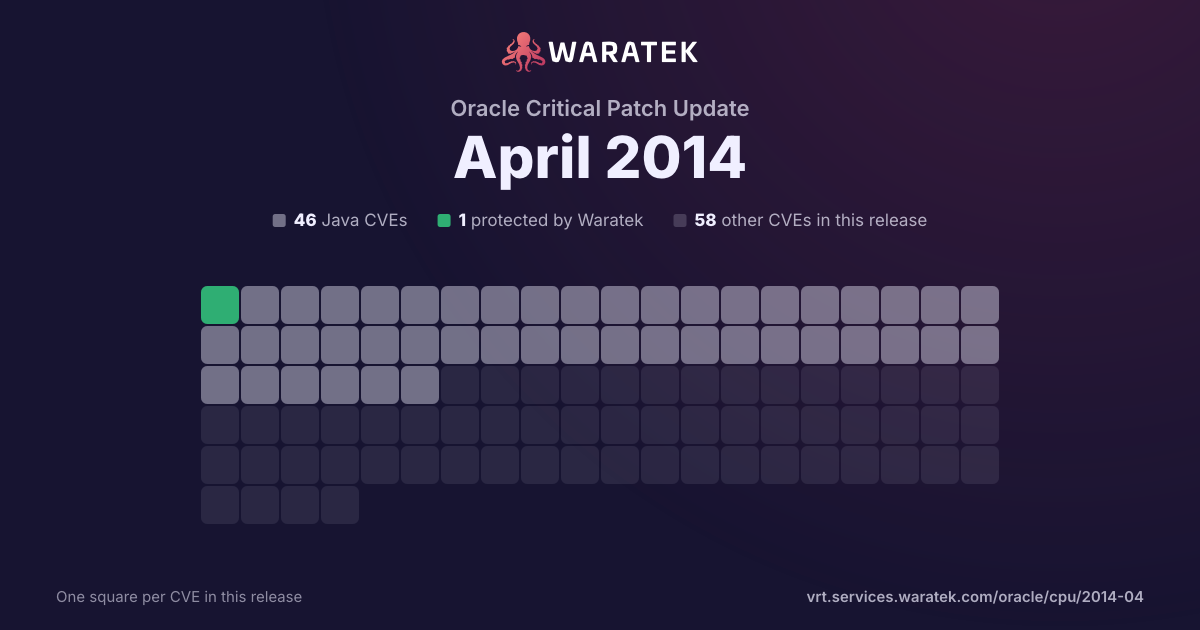
By status
1Protected by Waratek2Mitigation candidate43No exploit published33Outside Waratek scope25Not applicable
No exploit published. For 41 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 101 matches · 44 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
101matches
44in Waratek scope43.6%
1protected1.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
1
1.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
43
42.6%
Outside Waratek scope
33
32.7%
Not applicable
24
23.8%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
1.0%
partly blocked
0
0.0%
not blocked
100
99.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
101
100.0%
split by
peak 96 / month
Feb 131
Not applicable1
Medium1
not blocked1
No public exploit1
Mar 130
Apr 130
May 130
Jun 130
Jul 130
Aug 130
Sep 130
Oct 130
Nov 131
Not applicable1
Medium1
not blocked1
No public exploit1
Dec 130
Jan 142
Not applicable2
High1
Medium1
not blocked2
No public exploit2
Feb 141
No exploit published1
Medium1
not blocked1
No public exploit1
Mar 140
Apr 1496
Protected by Waratek1
No exploit published42
Outside Waratek scope33
Not applicable20
High23
Medium60
Low13
blocked by ARMR today1
not blocked95
No public exploit96
Feb 13Apr 13Jun 13Aug 13Oct 13Dec 13Feb 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-1620 | Medium | 2013-02-08 | Not applicable | No public exploit | The TLS implementation in Mozilla Network Security Services (NSS) does not properly consider timing side-channel attacks on a noncompliant MAC check operation during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, a related issue to CVE-2013-0169. |