
Oracle Critical Patch Update October 2012
Released October 2012 · Oracle's advisory ↗ · ← Critical Patch Update, July 2012 · Java SE Critical Patch Update, October 2012 →
107 CVEs in this release, one square each
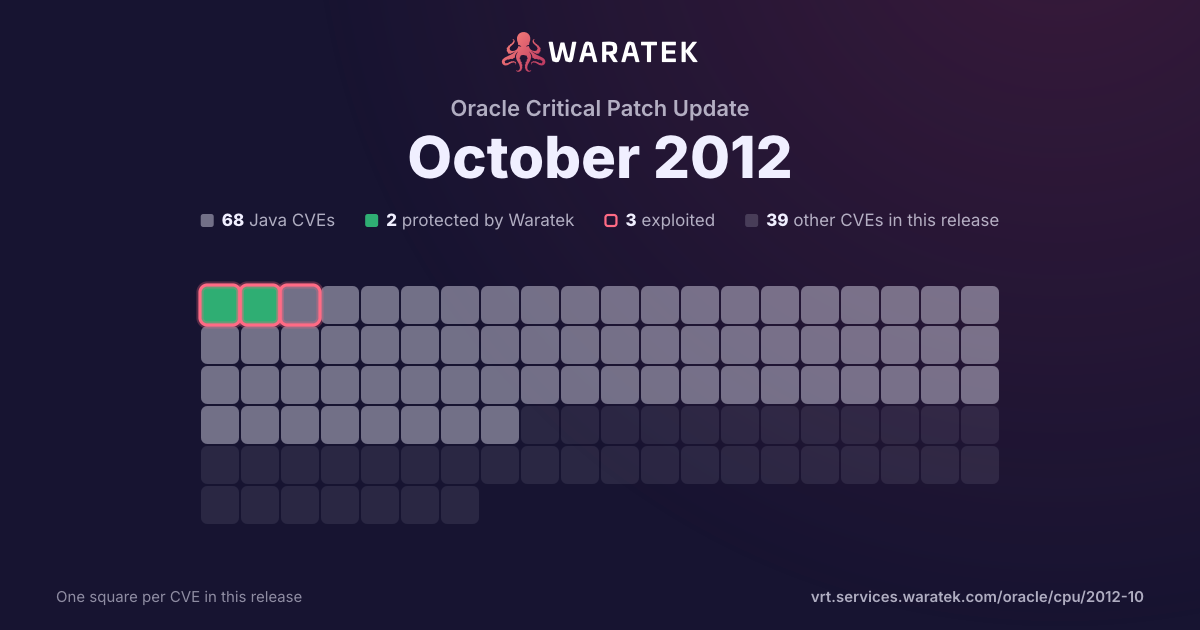
By status
2Protected by Waratek6Mitigation candidate62No exploit published4Outside Waratek scope33Not applicable
3Exploited, marked by the ring
No exploit published. For 61 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 14 matches · 1 protected · 2 exploited · 1 CISA KEV · 5 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
1
7.1%
Rule in development
0
0.0%
Mitigation candidate
5
35.7%
No exploit published
8
57.1%
blocked by ARMR today
1
7.1%
partly blocked
0
0.0%
not blocked
12
85.7%
not established
1
7.1%
unrecorded
0
0.0%
Exploited
2
14.3%
Working exploit published
4
28.6%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
8
57.1%
split by
peak 13 / month
Sep 111
No exploit published1
Medium1
not blocked1
No public exploit1
Oct 110
Nov 110
Dec 110
Jan 120
Feb 120
Mar 120
Apr 120
May 120
Jun 120
Jul 120
Aug 120
Sep 120
Oct 1213
Protected by Waratek1
Mitigation candidate5
No exploit published7
Medium13
blocked by ARMR today1
not blocked11
not established1
Exploited2
Working exploit published4
No public exploit7
Oct 11Dec 11Feb 12Apr 12Jun 12Aug 12Oct 12
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2012-3194 | Medium | 2012-10-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle BI Publisher component in Oracle Fusion Middleware 10.1.3.4.2, 11.1.1.5.0, 11.1.1.6.0, and 11.1.1.6.2 allows remote attackers to affect integrity via unknown vectors related to Administration. |
| CVE-2012-3186 | Medium | 2012-10-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 6.1, 6.2, 6.3.x, 7, 7.0.1, 7.0.2, 7.0.3, 7.5, 7.6.1, 7.6.2, and 11.1.1.6.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Advanced UI, a different vulnerability than CVE-2012-3183 and CVE-2012-3185. |
| CVE-2012-3185 | Medium | 2012-10-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 6.1, 6.2, 6.3.x, 7, 7.0.1, 7.0.2, 7.0.3, 7.5, 7.6.1, 7.6.2, and 11.1.1.6.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Advanced UI, a different vulnerability than CVE-2012-3183 and CVE-2012-3186. |
| CVE-2012-3184 | Medium | 2012-10-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 6.1, 6.2, 6.3.x, 7, 7.0.1, 7.0.2, 7.0.3, 7.5, 7.6.1, 7.6.2, and 11.1.1.6.0 allows remote attackers to affect integrity via unknown vectors related to Advanced UI. |
| CVE-2012-3183 | Medium | 2012-10-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 6.1, 6.2, 6.3.x, 7, 7.0.1, 7.0.2, 7.0.3, 7.5, 7.6.1, 7.6.2, and 11.1.1.6.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Advanced UI, a different vulnerability than CVE-2012-3185 and CVE-2012-3186. |
| CVE-2012-3175 | Medium | 2012-10-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Server Single Sign-On component in Oracle Fusion Middleware 10.1.4.3.0 allows remote attackers to affect integrity via unknown vectors related to Redirects, a different vulnerability than CVE-2012-0518. |
| CVE-2012-3153 | Medium | 2012-10-16 | Protected by Waratek | Exploited | Unspecified vulnerability in the Oracle Reports Developer component in Oracle Fusion Middleware 11.1.1.4, 11.1.1.6, and 11.1.2.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Servlet. NOTE: the previous information is from the October 2012 CPU. Oracle has not commented on claims from the original researcher that the PARSEQUERY function allows remote attackers to obtain database credentials via reports/rwservlet/parsequery, and that this issue occurs in earlier versions. NOTE: this can be leveraged with CVE-2012-3152 to execute arbitrary code by uploading a .jsp file. |
| CVE-2012-1686 | Medium | 2012-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Business Intelligence Enterprise Edition component in Oracle Fusion Middleware 11.1.1.6 and other versions allows remote attackers to affect integrity via unknown vectors related to Installation. |
| CVE-2012-0518 | Medium | 2012-10-16 | Mitigation candidate | Exploited | Unspecified vulnerability in the Oracle Application Server Single Sign-On component in Oracle Fusion Middleware 10.1.4.3.0 allows remote attackers to affect integrity via unknown vectors related to Redirects, a different vulnerability than CVE-2012-3175. |
| CVE-2012-0107 | Medium | 2012-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Imaging and Process Management component in Oracle Fusion Middleware 10.1.3.6.0 allows remote attackers to affect availability via unknown vectors related to Web. |
| CVE-2012-0106 | Medium | 2012-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Imaging and Process Management component in Oracle Fusion Middleware 10.1.3.6.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Web. |
| CVE-2012-0093 | Medium | 2012-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Imaging and Process Management component in Oracle Fusion Middleware 10.1.3.6.0 allows remote attackers to affect integrity via unknown vectors related to Web, a different vulnerability than CVE-2012-0071. |
| CVE-2012-0071 | Medium | 2012-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Imaging and Process Management component in Oracle Fusion Middleware 10.1.3.6.0 allows remote attackers to affect integrity via unknown vectors related to Web, a different vulnerability than CVE-2012-0093. |
| CVE-2011-1411 | Medium | 2011-09-02 | No exploit published | No public exploit | Shibboleth OpenSAML library 2.4.x before 2.4.3 and 2.5.x before 2.5.1, and IdP before 2.3.2, allows remote attackers to forge messages and bypass authentication via an "XML Signature wrapping attack." |