
Oracle Critical Patch Update July 2012
Released July 2012 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2012 · Critical Patch Update, October 2012 →
87 CVEs in this release, one square each
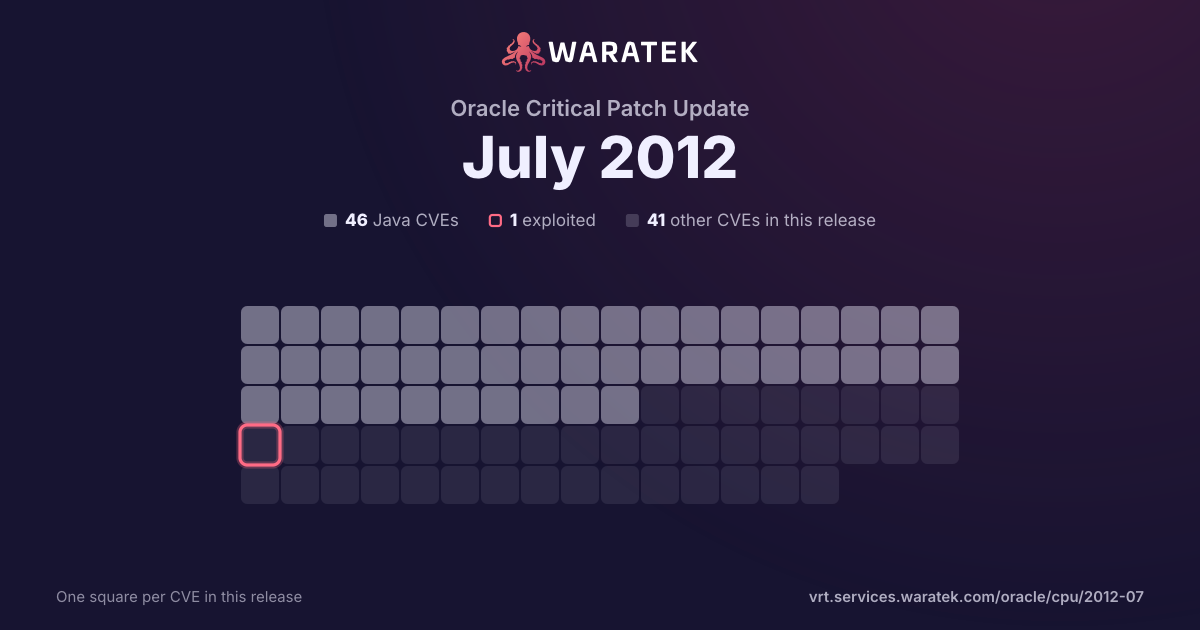
By status
3Mitigation candidate43No exploit published8Outside Waratek scope33Not applicable
1Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Overview 1 match · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV
1match
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
1
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Oct 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-3368 | Medium | 2011-10-05 | Not applicable | Working exploit published | The mod_proxy module in the Apache HTTP Server 1.3.x through 1.3.42, 2.0.x through 2.0.64, and 2.2.x through 2.2.21 does not properly interact with use of (1) RewriteRule and (2) ProxyPassMatch pattern matches for configuration of a reverse proxy, which allows remote attackers to send requests to intranet servers via a malformed URI containing an initial @ (at sign) character. |