
Oracle Critical Patch Update July 2012
Released July 2012 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2012 · Critical Patch Update, October 2012 →
87 CVEs in this release, one square each
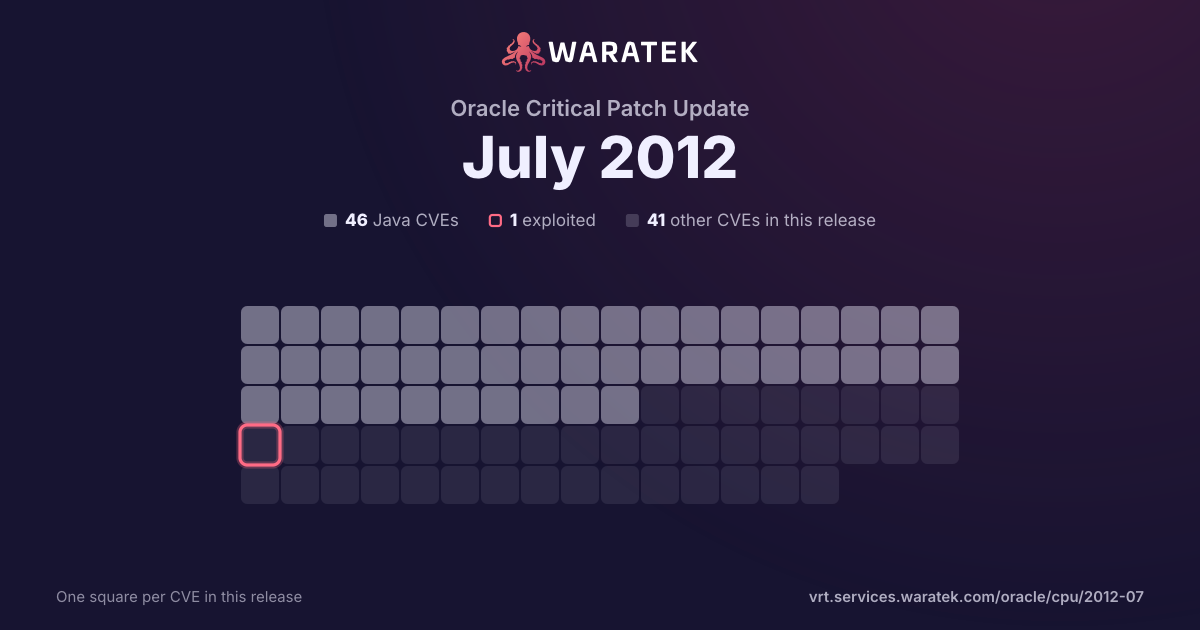
By status
3Mitigation candidate43No exploit published8Outside Waratek scope33Not applicable
1Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Overview 7 matches · 2 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
7matches
2in Waratek scope28.6%
0protected0.0%
1exploited14.3%
0CISA KEV0.0%
2public PoC28.6%
1EPSS ≥ 0.514.3%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
28.6%
Outside Waratek scope
0
0.0%
Not applicable
5
71.4%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
7
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
14.3%
Working exploit published
0
0.0%
Proof of concept only
1
14.3%
Forecast only
0
0.0%
No public exploit
5
71.4%
split by
peak 4 / quarter
Q4 081
Not applicable1
High1
not blocked1
Proof of concept only1
Q1 090
Q2 090
Q3 090
Q4 090
Q1 100
Q2 100
Q3 100
Q4 100
Q1 110
Q2 110
Q3 111
Not applicable1
High1
not blocked1
Exploited1
Q4 110
Q1 120
Q2 121
Not applicable1
High1
not blocked1
No public exploit1
Q3 124
No exploit published2
Not applicable2
High4
not blocked4
No public exploit4
Q1 09Q3 09Q1 10Q3 10Q1 11Q3 11Q1 12Q3 12
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2012-3135 | High | 2012-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JRockit component in Oracle Fusion Middleware 28.2.3 and before, and 27.7.2 and earlier, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2012-3125 | High | 2012-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8, 9, and 10 allows remote attackers to affect availability, related to TCP/IP. |
| CVE-2012-3120 | High | 2012-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8 allows remote attackers to affect availability, related to TCP/IP. |
| CVE-2012-1740 | High | 2012-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Express Listener component in Oracle Application Express Listener 1.1-ea, 1.1.1, 1.1.2, and 1.1.3 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2011-2699 | High | 2012-05-24 | Not applicable | No public exploit | The IPv6 implementation in the Linux kernel before 3.1 does not generate Fragment Identification values separately for each destination, which makes it easier for remote attackers to cause a denial of service (disrupted networking) by predicting these values and sending crafted packets. |
| CVE-2011-3192 | High | 2011-08-29 | Not applicable | Exploited | The byterange filter in the Apache HTTP Server 1.3.x, 2.0.x through 2.0.64, and 2.2.x through 2.2.19 allows remote attackers to cause a denial of service (memory and CPU consumption) via a Range header that expresses multiple overlapping ranges, as exploited in the wild in August 2011, a different vulnerability than CVE-2007-0086. |
| CVE-2008-4609 | High | 2008-10-20 | Not applicable | Proof of concept only | The TCP implementation in (1) Linux, (2) platforms based on BSD Unix, (3) Microsoft Windows, (4) Cisco products, and probably other operating systems allows remote attackers to cause a denial of service (connection queue exhaustion) via multiple vectors that manipulate information in the TCP state table, as demonstrated by sockstress. |